The cybercrime ecosystem is built on a foundation of shifting aliases, encrypted messaging apps, and strict operational security, yet even the most industrious cybercriminals eventually trip over their own digital footprints. The cybercrime group known as Qilin has rapidly ascended to become the world’s most active ransomware affiliate program, claiming at least 365 victim organizations in a mere three-month span. However, a meticulous paper trail spanning nearly a decade has linked the group’s top administrator to a real-world identity: a 36-year-old man living in St. Petersburg, Russia.
Operating continuously since September 2002—as highlighted in a comprehensive threat intelligence report released this month by cybersecurity firm NCC Group—the Russia-based Qilin gang currently stands as the most industrious ransomware-as-a-service (RaaS) operation in the threat landscape. For comparison, earlier this year, investigative reporting also turned its lens toward the administrative apparatus of the second most active ransomware operation, a collective known as The Gentlemen.
Qilin’s operational model relies on aggressive recruitment, drawing in affiliates by offering them a massive cut—at least 80 percent—of any extortion payment successfully squeezed from compromised victims. Members of the affiliate program utilize a standard "double extortion" methodology, which involves siphoning sensitive, proprietary data from a network before deploying encryption software and threatening to leak the stolen files publicly if demands are not met.
Unlike many Russian-speaking ransomware partnerships that maintain insular recruitment networks, Qilin has proven notably flexible, willingly collaborating with English-speaking affiliates. The gang’s primary leader has openly discussed these partnerships on Telegram, noting collaborations with notorious cybercrime actors and syndicates such as Scattered Spider and RansomHub.
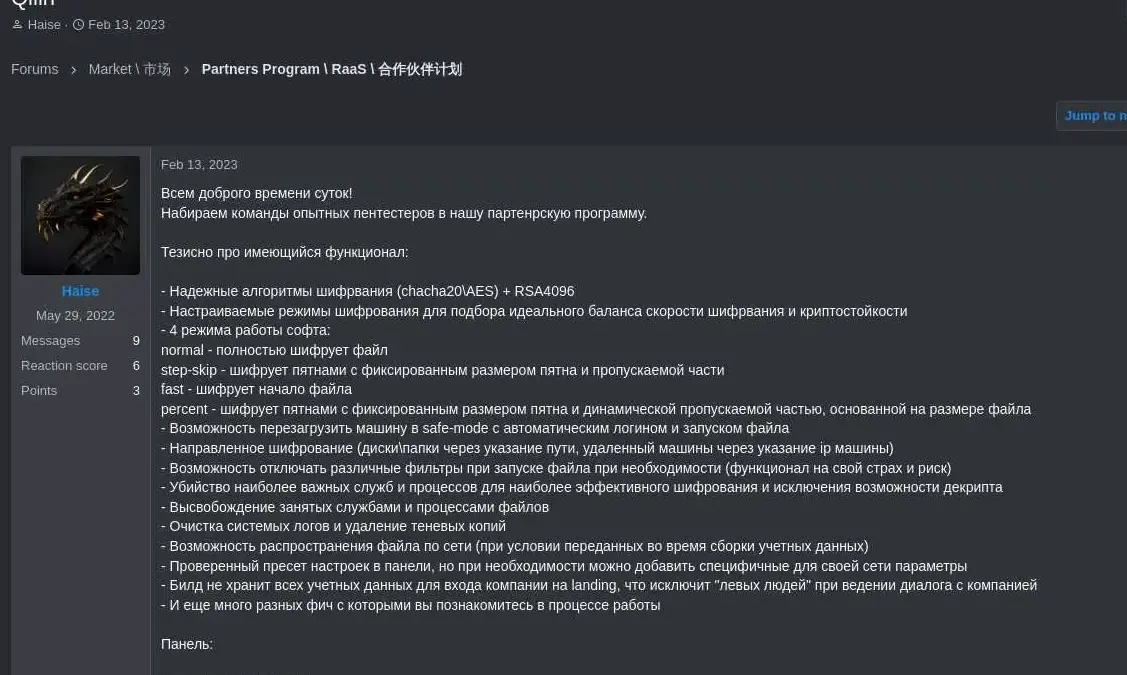
At the helm of Qilin is an administrator who operates under the handle “Haise.” Cybercriminals routinely cycle through nicknames as a standard operational security measure, a tactic designed to sever connections to older identities that might have compromised their real-life details or maintained sloppy hygiene regarding digital attribution. Nevertheless, even cautious threat actors frequently find themselves forced to reference past monikers when applying for membership on new, heavily vetted illicit forums—forums that are inevitably vulnerable to law enforcement seizures or data breaches. That exact vulnerability proved to be the undoing of the Qilin administrator.

According to intelligence gathered by the cyber threat intelligence platform Intel 471, an operator using the handle Haise applied for membership in June 2022 to RAMP, a closely guarded Russian cybercrime forum intentionally established as a sanctuary for ransomware affiliate programs. Records of direct messages recovered from RAMP—which was seized by the FBI in January 2026—reveal that the forum’s administrator approved Haise’s application while explicitly cross-referencing him with his Telegram username: Alexbigboss44.
A deeper search within Intel 471’s historical archives for the handle Alexbigboss44 demonstrates that this exact Telegram account was previously shared by a user named “Rjun” on prominent Russian cybercrime forums Exploit and XSS as early as 2020. According to the cyber intelligence firm Flashpoint, Alexbigboss44 was a prolific participant across various cybercriminal forums and Telegram channels, focusing heavily on the illicit trade of web traffic, access logs, and compromised corporate network credentials. Flashpoint’s analysis indicates that this user was deeply involved in acquiring massive volumes of Facebook logs and Google Ads accounts to facilitate fraudulent advertising and gambling schemes, operating effectively as a broker and manager of traffic-laundering networks.
The crucial connection between the modern Qilin administrator Haise and the older Rjun and Alexbigboss44 identities was brought to light earlier this month by IntelHawk, an artificial intelligence-powered platform specializing in de-anonymizing threat actors through historical usernames, stylometric analysis, and other behavioral signals.
IntelHawk founder and chief technology officer Leo Bogod noted that an exhaustive analysis of these overlapping digital identities reveals a clear evolutionary trajectory. The persona progressed from a relatively novice arbitrageur and credit card fraudster active between 2018 and 2019 into a sophisticated, experienced organizer of complex cybercrime operations between 2020 and 2023, steadily pivoting toward advanced malware, botnets, and resilient payment infrastructure.
Tracing these identities backward reveals an extensive historical web. Intel 471 established that by the time Alexbigboss44 was petitioning for entry into RAMP, the Rjun persona was already a long-standing, established member of several other historical Russian criminal forums, including Darkmarket, Verified, and Zloy. Crucially, records show that Rjun registered across all of these platforms using a specific email address: [email protected].
Identity threat protection firm Spycloud identified that this exact email address had previously utilized the password “Rjun132.” When queried through the breach-tracking service Constella Intelligence, the [email protected] address appeared within internal records maintained by gosuslugi.ru, the official digital portal for state and municipal services in the Russian Federation.

That specific digital ecosystem suffered a massive data breach in late 2025, which reportedly exposed more than 20 million records containing full legal names, dates of birth, and associated mobile phone numbers. According to the leaked Gosuslugi database indexed by Constella, the email address belongs to 36-year-old Aleksey Mikhailovich Yakovtsev, a resident of St. Petersburg, Russia.
Additional corroborating data uncovered by Flashpoint indicates that Haise maintained a long-running Telegram account associated with user ID 118329521, logging over 5,000 individual messages originating from the account since 2018. Public and institutional records from Russia’s education oversight body, Rosobrnadzor, indicate that Mr. Yakovtsev completed his early education in Murmansk and subsequently earned a master’s degree specializing in computing and information systems.
Running a query on that specific Telegram user ID within Constella connects the account to the Russian mobile phone number +79602347275. Pivoting on that phone number yields further links to alternative email addresses, including [email protected] and [email protected]. According to IntelHawk, the phone number is officially registered to Yakovtsev’s biological sister, and Aleksey frequently utilized his sister’s email addresses when registering user accounts across various web services.
That same phone number surfaces repeatedly within airline passenger manifests obtained from Russian travel agencies that suffered cybersecurity breaches in recent years. These travel records establish that Aleksey Yakovtsev, born on August 18, 1990, traveled by air between St. Petersburg and Murmansk on at least three separate occasions between 2013 and 2014.
More recent travel manifests indicate that while Mr. Yakovtsev has not recorded international air travel outside of Russia, he frequently flies domestically between St. Petersburg and Sochi. Frequently referred to as the "Russian Riviera," Sochi is the nation’s premier resort city situated along the Black Sea coast, located roughly 1,200 miles south of St. Petersburg by air.
Attempts to reach Mr. Yakovtsev for comment via his known email addresses and phone numbers were ultimately unsuccessful. Independent investigations by anonymous open-source intelligence researchers, including the X account GangExposed—which has a documented track record of successfully de-anonymizing high-profile ransomware operators—arrived at strikingly similar conclusions regarding Haise’s true identity, publicly crediting IntelHawk’s platform for instrumental assistance in connecting the digital dots.