U.S. federal investigators pursuing the prolific ShinyHunters hacking group—which recently shocked the cybersecurity community by stealing highly sensitive data from the FBI—have identified executives at two different ransomware negotiation firms who maintained unusually close and suspicious relations with the extortion syndicate. Sources close to the ongoing investigation revealed that one of these executives, based inside the United States, even went so far as to help ShinyHunters operate an active pressure website designed to coerce victims into meeting exorbitant ransom demands.
Hackers aligned with the ShinyHunters brand have claimed credit for dozens of major corporate and institutional data breaches since 2019. In its early days, the group was primarily operated by cybercriminals residing in France. However, as those original members were systematically arrested, prosecuted, and jailed one by one, control over the lucrative ShinyHunters name eventually passed to a young administrator known online as "Rey." This key figure was identified last year as a teenage hacker hailing from Amman, Jordan. According to official figures released by the FBI, ShinyHunters has successfully extorted more than $70 million from corporate and public sector victims so far this year alone.
The group’s brazen activities reached a crescendo in late September, when hackers associated with ShinyHunters compromised the FBI recruitment website, fbijobs.gov. The attackers immediately taunted federal law enforcement by threatening to publish the stolen files online. According to reports, the compromised trove included deeply sensitive personnel information, such as medical and psychological records, Social Security numbers, home addresses, and specific details regarding the professional specializations and units of individual bureau employees.
This unprecedented breach of an FBI-affiliated portal prompted the agency to move with uncommon speed, arresting, detaining, and questioning individuals who had maintained any form of communication with Rey or other primary ShinyHunters suspects. On October 3, Reuters reported that Rey had been detained by authorities in Jordan and was actively cooperating with the FBI’s sweeping investigation.
Rey’s rise to power within the syndicate had been made possible following the sudden neutralization of a senior member. On the evening of September 15, 2026, law enforcement officers in the Netherlands executed a high-stakes raid, arresting convicted hacker and primary ShinyHunters suspect Pepijn van der Stap. Dutch police reportedly deployed flash-bang grenades in a tactical effort to stun and apprehend Van der Stap precisely as he was actively logged into various online accounts.
According to sources close to the unfolding investigation, authorities managed to apprehend Van der Stap while he was actively using his Signal instant messaging account. This immediate physical intervention allowed investigators to access and read recent, unencrypted communications with his most frequent contacts, including ransomware negotiators operating out of Canada and the United States.
Multiple well-placed sources told KrebsOnSecurity that Van der Stap’s recovered Signal messages served as the crucial key to unraveling an entirely separate, dark plot: a murder-for-hire scheme that surfaced immediately in the wake of his arrest. The Dutch news outlet RTL reported last month that two planned murders were allegedly slated to be committed abroad, with strong investigative indications suggesting that Van der Stap had personally issued the orders for the attacks, though officials noted there was no indication those violent directives were ever successfully carried out.

The international dragnet soon widened significantly. On October 9, KrebsOnSecurity broke the news that the FBI had arrested a 54-year-old Canadian cybersecurity executive named Edward Dubrovsky in direct connection with the expansive ShinyHunters investigation. Dubrovsky, who had recently published a book on handling corporate cyber extortion that explicitly recommended always engaging directly with hackers, was formally charged with threatening to disclose stolen data and interfering with interstate commerce through extortion, according to federal court records. Politico reported that federal prosecutors requested Dubrovsky remain in custody pending trial, and that all records related to his specific criminal case remain strictly under seal.
A confidential source close to the investigation revealed that Van der Stap’s recovered Signal chat logs demonstrated frequent, direct conversations between the Dutch hacker, Mr. Dubrovsky, and at least one executive at a large, U.S.-based consulting firm. Disturbingly, these messages showed that these corporate executives frequently possessed detailed knowledge of brand-new ShinyHunters victims long before the target organizations themselves had even discovered or realized they had been breached.
That same investigative source shared another potentially explosive finding uncovered by federal agents: the Dutch hacker’s chats proved that Mr. Dubrovsky was fully aware that ShinyHunters had exfiltrated highly sensitive data straight from primary FBI servers. Despite this knowledge, Dubrovsky never notified the bureau of the catastrophic data breach prior to ShinyHunters publicly announcing the hack and threatening on Twitter/X to publish the agency’s deeply personal personnel files.
SHINYWIRE
As the probe deepened, KrebsOnSecurity learned from two independent sources close to the ShinyHunters investigation that FBI agents believe at least one executive at a prominent U.S.-based consulting firm played an active, operational role in running the now-defunct ShinyHunters victim extortion website, known as "shinywire[.]com." While KrebsOnSecurity has chosen to withhold the specific name of the U.S. company and the suspected executive for the time being, given that formal criminal charges have not yet been filed, the entity is described as a prestigious firm employing more than 1,000 associates.
The Shinywire website remained active from approximately May 3, 2026, until October 16, hosting profiles for nearly 100 corporate and institutional organizations that had fallen victim to ShinyHunters breaches. Each specific entry on the portal aggressively urged victim companies to engage with the cybercrime syndicate to discuss financial terms for payment. To apply maximum pressure, the pages featured authentic samples of stolen corporate files and explicitly promised that the entirety of the pilfered data would be published publicly online if the targeted enterprise ignored their demands.
Cached records and indexing tools like urlscan.io captured numerous extortion listings on the site, including one targeting Intuitive Surgical, a major American medical technology company that was breached in March 2026 after an employee fell victim to a sophisticated, targeted phishing email. Under the operational model of the site, victim organizations that refused to engage in negotiations within a strict seven-day window found their stolen data permanently published on the main ShinyHunters victim-shaming blog, which was hosted exclusively on the Tor anonymity network.
The widening scandal has also exposed bitter internal corporate warfare within the cybersecurity industry. In a story published on October 15, The Globe and Mail reported that a few months prior to his arrest by the FBI, Edward Dubrovsky had alleged in Canadian court documents that he had become collateral damage in a malicious campaign orchestrated by a former business partner seeking to entirely destroy another industry executive.

Court filings showed Dubrovsky had filed a lawsuit in Ontario against Daniel Tobok, the former chief executive of Cypfer, a prominent cybersecurity firm founded in Toronto with international offices spanning the United States, Britain, the Netherlands, the United Arab Emirates, and Mexico. Dubrovsky and Tobok initially became business partners in 2017 and subsequently built Cypfer together, with Dubrovsky serving as a managing partner and chief operating officer. However, by 2024, their relationship deteriorated significantly, with Dubrovsky accusing Tobok of gradually freezing him out of core business matters and making increasingly erratic corporate decisions.
Tobok strongly denied the allegations and filed a robust counterclaim, accusing Dubrovsky of unlawfully accessing confidential corporate information and engaging in unfair competition through his work with another firm, CyberSteward Inc. Tobok further asserted that Dubrovsky had repeatedly misrepresented himself as an original founder of Cypfer, pointing out that Dubrovsky held no equity shares in the company.
GHOSTBYTE
The investigation into the broader ecosystem of ransomware negotiation and facilitation took another intriguing turn when interviews with several former colleagues of Mr. Tobok revealed that, as far back as eight years ago, he was widely known among early ransomware purveyors by a specific moniker: "Ghostbyte."
In 2018, a Canadian company fell victim to an intrusion by Dharma, a prolific, Russian-language ransomware affiliate program that first emerged in 2016. When the victim company informed the Dharma ransomware representative that they were leaning toward paying the ransom because critical encrypted files were unrecoverable, they expressed a need for a reliable guarantee that the cybercriminals would actually honor their word once paid.
A redacted copy of the Dharma representative’s email reply directed the desperate victim to contact a specific individual at a Canadian IT firm that specialized in providing such trust guarantees. The cybercriminal explicitly recommended reaching out to the email address [email protected]. The Dharma representative wrote in the email that if the victim wanted enforceable guarantees, they could write to the designated IT company, take up the phone, and negotiate terms directly, noting that the specific Canadian firm frequently solved such extortion dilemmas locally.
While it remains unclear whether Mr. Tobok ever personally utilized the Ghostbyte address provided by the Dharma affiliate, and despite the fact that Tobok has declined multiple media requests for comment, digital intelligence records complicate the picture. According to the breach tracking service Constella Intelligence, an email address frequently utilized by Mr. Tobok—[email protected]—is directly associated with two online accounts that utilized "ghostbyte" as their chosen username, including a Snapchat profile.
Furthermore, Constella discovered that the Dharma representative’s listed email address, [email protected], was tied directly to a specific cryptocurrency wallet address that processed 38 transactions totaling roughly 43 bitcoin, representing an estimated $3.5 million at today’s market value, with its most recent recorded transaction dated February 2019.

In an official statement released on October 14, Cypfer forcefully distanced itself from the unfolding criminal proceedings, stating that the company’s core business model does not include making or facilitating ransomware payments. Furthermore, Cypfer asserted that corporate leadership only learned of Dubrovsky’s arrest when the news broke publicly in the media.
The company spokesperson emphasized that Cypfer had received no prior outreach from law enforcement and, to their knowledge, was not the target of any active government investigation. The statement clarified that CyberSteward and Cypfer operate as entirely separate entities with zero overlapping officers, directors, or employees. Additionally, Cypfer noted it was recently acquired by the Apros Group, a holding company led by Jason Hogg, a former FBI special agent and former CEO of Aon Cyber Solutions Group. In 2020, Aon had previously acquired Cytelligence, a security consulting firm where Tobok served as founder and CEO and Dubrovsky served as a managing partner.
CONFLICTING INTERESTS
The legal and ethical landscape surrounding ransomware negotiations remains fraught with complexity. Under current U.S. law, it is not strictly illegal for corporate victims to pay hackers to obtain decryption keys or secure promises to delete stolen files, provided the recipient group is not formally sanctioned by the U.S. Treasury Department’s Office of Foreign Assets Control. Because ShinyHunters is not currently on any government sanctions list, victims have historically had legal leeway to pay.
Industry experts note that organizations targeted by ransomware are typically directed by their cyber insurance providers to engage specific incident response firms. However, not all digital forensics and breach response companies agree to facilitate extortion payments on behalf of their clients. When principled firms refuse to reward cybercriminals, they are frequently dismissed by anxious executives and replaced by negotiation firms that exhibit fewer ethical qualms.
The dangers of paying extortionists were starkly illustrated in December 2024, when ShinyHunters launched a massive campaign against education technology giant PowerSchool, stealing private records belonging to 62 million students and 9.5 million teachers across the U.S. and Canada. PowerSchool reportedly paid a $2.85 million ransom demand, assisted by CyberSteward according to publicly available breach documentation. Despite the payout, the threat actors’ associate Matthew Lane—a 20-year-old college student from Sterling, Massachusetts—was later convicted and sentenced in November 2025 to four years in federal prison for his role in the hack.
Crucially, paying the ransom did not stop secondary extortion. By May 2025, individual school districts began receiving independent ransom demands utilizing samples of the very same stolen PowerSchool data. While investigators have not alleged that ShinyHunters orchestrated the second wave of extortion, the incident underscores a grim reality recognized by cybersecurity professionals: there is no technical mechanism to verify that threat actors have permanently deleted stolen data, nor can a payout prevent malicious third parties from abusing the exact same leaked records.
Leading cyber incident response firms, including Coveware and Unit 221B, have consistently warned corporate victims against paying ShinyHunters, publicly pointing out that supposedly "destroyed" victim data is routinely retained, resold, or leveraged to directly target and extort a company’s downstream clients later.

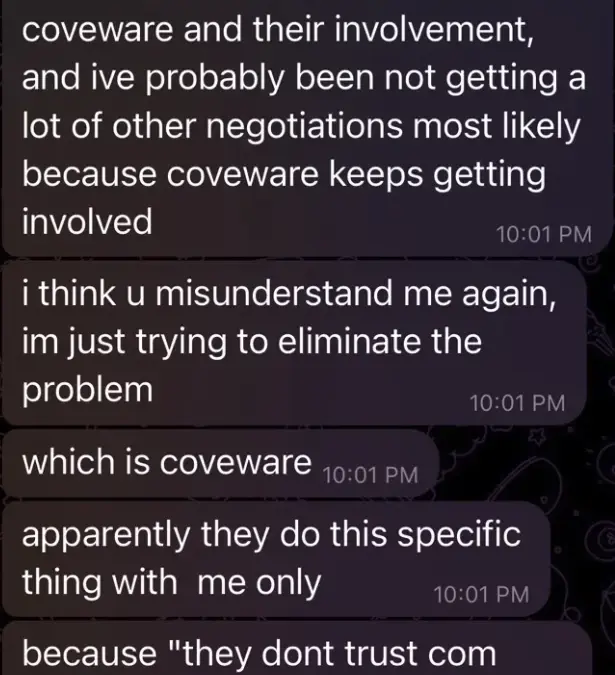
The FBI echoed those precise warnings in a formal public service announcement on May 15, 2026, explicitly advising against paying the ShinyHunters syndicate. This principled stance, however, made the FBI and defensive firms primary targets for hacker retaliation. Internal Telegram chats recovered by investigators revealed just how intensely frustrated the ShinyHunters leadership was with Coveware’s relentless public advice urging victims not to pay.
In private conversations dated May 6, 2026, the main ShinyHunters Telegram account complained bitterly to a co-conspirator that Coveware’s public warnings were actively ruining their payment rates and business model. The administrator lamented that the majority of compromised companies would have paid if not for what they termed Coveware’s misinformation, adding in an earlier April chat that they were actively trying to "eliminate the problem" posed by Coveware’s interference. Coveware declined to comment when approached for this story.
Mark Camillo, chief executive of CyberAcuView—an industry association established in 2021 by a consortium of major cyber insurers—pointed out that the commercial incentives within the negotiation sector often create severe conflicts of interest. While some incident response firms charge flat retainer fees, others operating as specialized ransomware negotiators charge a direct percentage of the total ransom amount paid to the hackers.
Camillo noted that this percentage-based model introduces an inherent conflict, as the negotiator becomes financially incentivized to drive up the payout size and discourage aggressive bargaining to lower the ransom. It has increasingly come to the industry’s attention that many negotiators charge undisclosed percentages of the final payment transaction, a practice Camillo argues makes little sense if they are acting as trusted fiduciary advisors. He emphasized the urgent need for greater transparency across the insurance and negotiation ecosystem to ensure no entity profits purely from the sheer magnitude of a cyber extortion payment.
Federal prosecutors have increasingly targeted these misaligned financial incentives through direct criminal enforcement. On October 7, the Department of Justice charged MonsterCloud CEO Zohar Pinhasi with wire fraud and conspiracy. Prosecutors alleged that Pinhasi charged customers millions of dollars for technical remediation while secretly going behind their backs to pay hackers directly, funneling $8 million to ransomware groups while billing clients a total of $19 million.
Similarly, in July, Angelo Martino, a 41-year-old ransomware negotiator based in Land O’Lakes, Florida, was sentenced to 70 months in federal prison for conspiring with the Blackcat/ALPHV ransomware syndicate to extort multiple corporate victims. According to the DOJ, Martino accepted payments from the cybercriminals in exchange for feeding them confidential information regarding his employer’s negotiation strategies, directly enabling the hackers to maximize their extortion profits at the expense of victimized companies.