U.S. federal investigators probing the notorious "ShinyHunters" cybercrime syndicate—which recently compromised highly sensitive files belonging to the Federal Bureau of Investigation—have identified executives at two separate ransomware negotiation firms maintaining unusually close ties to the extortion group. According to sources close to the unfolding federal probe, one of these executives in the United States allegedly assisted ShinyHunters in operating a dedicated website designed to pressure breached organizations into coughing up ransom payments.
The ShinyHunters collective has claimed responsibility for dozens of high-profile data breaches dating back to 2019, an era when the enterprise was largely directed by cybercriminals residing in France. As law enforcement dismantled the original roster through targeted arrests and incarcerations, leadership of the brand eventually gravitated toward an individual known as "Rey." Last year, federal authorities identified Rey as a teenage hacker operating out of Amman, Jordan. The FBI estimates that ShinyHunters has successfully extorted more than $70 million from corporate and governmental victims over the course of the current year alone.
The gravity of the threat escalated sharply in late September, when ShinyHunters compromised the FBI recruitment portal, fbijobs.gov. The hackers publicly taunted the federal law enforcement agency by threatening to leak stolen personnel files. According to reports, these compromised documents included sensitive medical and psychological records, Social Security numbers, home addresses, and detailed information regarding individual employee specializations and organizational units.
This brazen attack on federal infrastructure prompted the FBI to act with extraordinary velocity, detaining and questioning individuals who maintained any digital footprint or communication history with Rey or other key ShinyHunters suspects. On October 3, Reuters reported that Rey had been detained by authorities in Jordan and was actively cooperating with the FBI.
Rey’s consolidation of power over the hacking group followed the sudden disruption of a senior operational figure. On the evening of September 15, 2026, Dutch law enforcement officers arrested Pepijn van der Stap, a convicted hacker and prime suspect in the ShinyHunters investigation. Reports indicate that Dutch police deployed flash-bang grenades to disorient Van der Stap as he remained actively logged into multiple online accounts.

According to investigative sources, the raid occurred while Van der Stap was utilizing his Signal instant messaging application, granting police immediate access to recent communications with frequent contacts. These contacts reportedly included ransomware negotiators situated in Canada and the United States. Multiple knowledgeable sources confirmed to KrebsOnSecurity that Van der Stap’s recovered messaging history proved instrumental in unraveling a separate murder-for-hire plot that surfaced immediately following his apprehension. Dutch media outlet RTL reported last month that two foreign murders were allegedly commissioned, with indications pointing to Van der Stap as the individual who issued the directives, though no evidence suggests the plots were ever executed.
On October 9, KrebsOnSecurity broke the news that the FBI had arrested Edward Dubrovsky, a 54-year-old Canadian cybersecurity executive, in connection with the sprawling ShinyHunters investigation. Dubrovsky, who recently authored a book on handling cyber extortion that advised victims to consistently engage with threat actors, faces federal charges of threatening to disclose hacked data and interfering with interstate commerce through extortion, according to court documents filed in the docket. Politico reported that federal prosecutors have requested Dubrovsky remain detained pending trial, and that case records have been placed under seal.
A source close to the investigation disclosed that Van der Stap’s decrypted Signal chats revealed frequent conversations between the Dutch hacker, Dubrovsky, and at least one executive at a prominent U.S.-based consulting firm. These communications allegedly demonstrated that the executives often possessed detailed knowledge of fresh ShinyHunters victims before the targeted organizations themselves realized they had been breached. Furthermore, investigators uncovered evidence indicating Dubrovsky was aware that ShinyHunters had exfiltrated sensitive data from FBI servers well before the group publicly threatened to publish the personnel files on Twitter and X, yet he never notified the bureau.
SHINYWIRE
Federal investigators believe at least one executive at a major U.S. consulting firm played an active operational role in running "shinywire[.]com," a now-defunct extortion portal utilized by ShinyHunters. While KrebsOnSecurity has chosen to withhold the names of the U.S. firm and the suspected executive pending formal criminal charges, the enterprise is described as a prestigious organization boasting more than 1,000 associates.
The Shinywire website operated from roughly May 3, 2026, until October 16, cataloging nearly 100 organizations compromised by ShinyHunters. Each entry functioned as an aggressive pressure tactic, urging victims to open lines of communication with the cybercrime ring to negotiate payment terms. The pages featured samples of stolen documentation alongside explicit warnings that the full cache would be dumped publicly online if demands went ignored.

Cached internet records captured extortion listings targeting entities such as Intuitive Surgical, an American medical technology firm breached in March 2026 after an employee fell victim to a targeted phishing email campaign that compromised corporate credentials. Under ShinyHunters’ standard operational model, victim organizations that refused to engage within a strict seven-day window found their stolen records permanently published on the group’s shaming blog, which is exclusively accessible via the Tor anonymity network.
The Globe and Mail reported on October 15 that months prior to his arrest, Dubrovsky had filed a lawsuit in Ontario alleging he had become collateral damage in a scorched-earth campaign by a former business partner aiming to undermine another industry figure. The litigation targeted Daniel Tobok, the former chief executive of Cypfer, an international cybersecurity firm founded in Toronto with offices spanning the United States, Britain, the Netherlands, the United Arab Emirates, and Mexico. Dubrovsky and Tobok initially partnered in 2017 to build Cypfer, where Dubrovsky served as managing partner and chief operating officer. By 2024, however, a severe falling out occurred, with Dubrovsky alleging that Tobok gradually pushed him out of corporate operations and enacted increasingly capricious business decisions. Tobok denied the allegations and filed a counterclaim accusing Dubrovsky of misappropriating confidential information and competing unfairly through an alternative venture called CyberSteward Inc., while asserting that Dubrovsky was merely an employee rather than a founding shareholder.
GHOSTBYTE
Interviews with former colleagues of Daniel Tobok reveal that as far back as eight years ago, he was recognized within ransomware circles by the moniker "Ghostbyte." In 2018, a Canadian enterprise fell victim to Dharma, a prolific Russian-language ransomware affiliate program active since 2016. When the victim informed Dharma representatives that they were inclined to pay the ransom because locked files were unrecoverable, they requested guarantees that the threat actors would honor the agreement.
A redacted copy of the Dharma representative’s response directed the victim to contact an individual at a Canadian IT firm specializing in such matters, recommending an email address associated with the handle "[email protected]." The representative advised the company to establish a service contract with the suggested IT firm to facilitate the transaction.
While it remains unproven whether Tobok actively monitored or utilized the Ghostbyte email address, breach-tracking intelligence from Constella Intelligence indicates that a primary email address frequently used by Tobok—[email protected]—was linked to online accounts utilizing the username "ghostbyte," including a Snapchat profile. Constella’s analysis further tied the Dharma representative’s fallback email address to a cryptocurrency wallet that processed 38 transactions totaling roughly 43 bitcoin, valued at approximately $3.5 million at current market rates, with its final recorded transaction dating to February 2019.

Cypfer issued a statement on October 14 maintaining that the firm does not facilitate ransomware payments and stating that leadership learned of Dubrovsky’s arrest through media coverage. A company spokesperson emphasized that Cypfer had received no inquiries from law enforcement and was not the target of any ongoing investigation. The statement noted that CyberSteward and Cypfer operate as entirely separate corporate entities sharing no officers, directors, or employees, and highlighted Cypfer’s recent acquisition by Apros Group, a holding company led by Jason Hogg, a former FBI special agent and former CEO of Aon Cyber Solutions Group. Aon previously acquired Cytelligence in 2020, a security consultancy where Tobok served as founder and CEO and Dubrovsky operated as managing partner.
CONFLICTING INTERESTS
Paying ransoms to secure decryption keys or promises of data deletion is not inherently illegal under United States law, provided the victim organization does not disburse funds to a terrorist organization or a group explicitly sanctioned by the U.S. Treasury Department. ShinyHunters currently lacks formal designation on government sanctions lists.
Insurance providers frequently direct cyberattack victims toward specialized incident response firms. However, because not all forensics companies are willing to broker extortion payments, clients frequently pivot away from firms with strict ethical policies toward those willing to execute payouts.
In December 2024, ShinyHunters targeted educational technology provider PowerSchool, exfiltrating records belonging to 62 million students and 9.5 million teachers across the U.S. and Canada. PowerSchool reportedly paid a $2.85 million ransom. Documentation regarding the incident indicated that PowerSchool utilized the services of CyberSteward during the ordeal. A 20-year-old ShinyHunters affiliate from Massachusetts was subsequently sentenced to four years in prison for his role in the PowerSchool intrusion.
Despite the ransom payment, the breach yielded secondary extortion attempts. By May 2025, individual school districts began receiving independent ransom demands utilizing identical stolen file samples, illustrating the fundamental reality that threat actors provide no verifiable assurance that exfiltrated data has been permanently destroyed.

Leading incident response organizations, including Coveware and Unit 221B, have consistently warned victims against paying ShinyHunters, emphasizing that purloined data is frequently retained, resold, or weaponized against clients at a later date. The FBI issued a public service announcement on May 15, 2026, echoing these warnings and advising against capitulating to the syndicate’s demands.
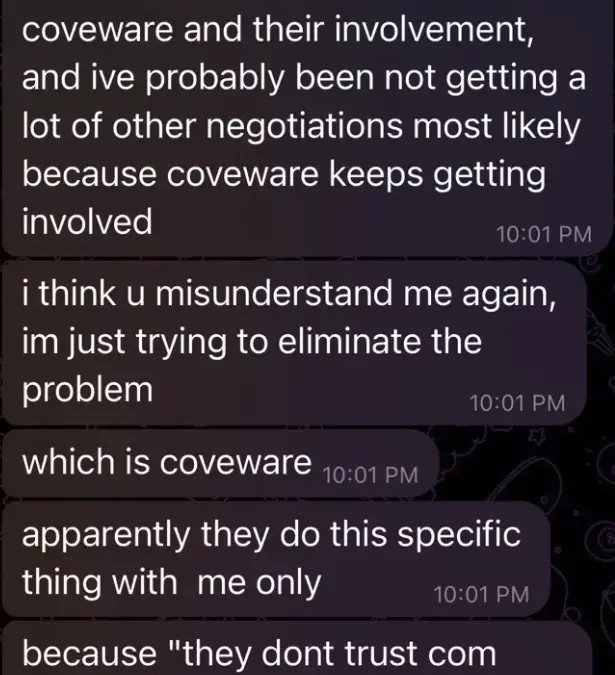
Internal communications reviewed by federal investigators highlight the friction caused by these advisories. Private Telegram chats from May 2026 show ShinyHunters leadership lamenting that Coveware’s public guidance was actively subverting their extortion revenue. The group’s primary administrator complained to an associate that prospective victims would have paid were it not for Coveware’s intervention, going so far as to state intentions to "eliminate the problem." Coveware declined to comment on the matter.
Mark Camillo, chief executive of CyberAcuView—an industry association established by major cyber insurance carriers—pointed out that payment-brokering firms often charge a percentage of the total ransom disbursed. This fee structure creates an inherent conflict of interest, incentivizing negotiators to inflate ransom payouts rather than negotiate reductions. Camillo noted that while firms defend these charges by citing the operational risks of handling volatile cryptocurrency floats and high-risk exchange fees, the ecosystem requires greater transparency to eliminate misaligned financial motivations.
Federal prosecutors have increasingly targeted compromised negotiators. On October 7, the Department of Justice charged MonsterCloud CEO Zohar Pinhasi with wire fraud and conspiracy, alleging he charged clients millions for remediation while secretly paying hackers a fraction of the cost. Similarly, in July, Florida ransomware negotiator Angelo Martino was sentenced to 70 months in prison for conspiring with the Blackcat/ALPHV ransomware collective to extract maximal payouts by leaking confidential client negotiation strategies.