
The international investigation has accelerated dramatically following a series of high-profile cyberattacks, most notably an intrusion in late September targeting the FBI recruitment portal, fbijobs.gov. Hackers aligned with ShinyHunters brazenly taunted federal law enforcement by threatening to publicly release a treasure trove of stolen personnel files. This data reportedly encompassed highly sensitive internal records, including medical and psychological evaluations, Social Security numbers, residential addresses, and specific unit specializations for bureau employees.
Ever since the group burst onto the cybercriminal landscape in 2019—initially operated primarily by operatives based in France—it has claimed responsibility for dozens of massive corporate and institutional data breaches. As those early founders were systematically arrested or imprisoned by international law enforcement, control over the ShinyHunters brand eventually transitioned to an administrator known as "Rey," who was publicly unmasked last year as a teenage hacker residing in Amman, Jordan. According to federal estimates, the syndicate has successfully extorted more than $70 million from corporate and government victims over the course of the year.
The breach of the FBI jobs portal triggered an immediate and aggressive response from federal authorities, who moved swiftly to detain and interrogate individuals suspected of maintaining communications with Rey and other key suspects. Reuters reported that Rey was detained by Jordanian authorities and has since been cooperating with the FBI.

Rey’s consolidation of power within the syndicate followed the sudden neutralization of a senior European operative. On the evening of September 15, Dutch law enforcement executed a dramatic raid, utilizing flash-bang grenades to stun and apprehend convicted hacker and ShinyHunters suspect Pepijn van der Stap as he actively logged into various online accounts. Sources close to the probe revealed that authorities arrested Van der Stap while he was logged into his Signal instant messaging account, granting investigators immediate, real-time access to his recent communications with frequent contacts, which included commercial ransomware negotiators located in both Canada and the United States.
Analysis of Van der Stap’s decrypted messaging logs proved to be a watershed moment for law enforcement, unraveling not only financial extortion networks but also pointing toward a chilling murder-for-hire plot. Dutch media outlet RTL reported that two murders were allegedly planned to be carried out abroad, with investigators finding indications that Van der Stap issued the orders for the planned attacks, though there is no evidence that those directives were ever successfully executed.
The digital trail soon led directly to the executive suites of the cybersecurity industry. On October 9, federal authorities arrested Edward Dubrovsky, a 54-year-old Canadian cybersecurity executive, in connection with the sprawling ShinyHunters investigation. Dubrovsky, who recently published a book on handling cyber extortion that advised victims to consistently engage with threat actors, faces federal charges including threatening to disclose compromised data and interfering with interstate commerce through extortion. Federal prosecutors requested that Dubrovsky remain in federal custody pending trial, and court records associated with the case have been placed under seal.
Investigative sources revealed that Van der Stap’s Signal archive demonstrated regular, detailed correspondence between the Dutch hacker, Dubrovsky, and at least one executive at a major U.S.-based consulting firm. Remarkably, these messages showed that the executives frequently possessed precise details regarding newly targeted organizations even before the victim entities themselves had discovered or realized they had been breached. Furthermore, federal investigators discovered that Dubrovsky was fully aware that ShinyHunters had exfiltrated sensitive data from FBI servers long before the group publicly threatened to publish the personnel files on social media, yet he failed to notify the bureau.

SHINYWIRE
As the probe widened, investigators zeroed in on a dedicated extortion portal orchestrated by the hackers, known as "shinywire[.]com." Sources close to the investigation disclosed that federal agents believe at least one executive at a prominent U.S. consulting firm played an active, operational role in maintaining the site. While investigators have refrained from publicly naming the U.S. company or the specific executive pending formal criminal charges, the firm in question is an elite enterprise employing more than 1,000 professionals.
The Shinywire platform remained active from early May until mid-October, cataloging nearly 100 corporate and institutional organizations compromised by ShinyHunters. Each victim listing featured samples of stolen proprietary files and explicitly warned that the data would be permanently leaked unless the organization engaged with the extortionists to negotiate payment terms. Victims who refused to communicate within a strict seven-day window found their complete data archives dumped onto the syndicate’s primary shaming blog, which is accessible exclusively via the Tor anonymity network.
Cached records from monitoring services such as urlscan.io highlighted listings targeting major corporate entities, including Intuitive Surgical, an American medical technology company that suffered a breach earlier in the year after an employee fell victim to a targeted phishing campaign.
The fallout from the investigation has also exposed deep corporate fractures and personal feuds within the upper echelons of the cybersecurity consulting sector. Court documents filed in Ontario revealed that months prior to his arrest, Edward Dubrovsky had launched a lawsuit against Daniel Tobok, the former chief executive of Cypfer, a prominent Toronto-founded incident response firm with global operations. Dubrovsky alleged that he had been made collateral damage in a malicious campaign by his former business partner designed to ruin another industry executive. The two men had co-founded Cypfer together following years of partnership, but experienced a bitter falling out characterized by accusations of exclusion and capricious management decisions. Tobok denied the allegations, filing a counterclaim accusing Dubrovsky of misappropriating confidential information and engaging in unfair competition through another venture known as CyberSteward Inc.

GHOSTBYTE
Interviews with former colleagues of Daniel Tobok revealed that dating back roughly eight years, the executive had been known within certain ransomware circles by a distinct alias: Ghostbyte. In 2018, a Canadian enterprise was targeted by Dharma, a prolific Russian-language ransomware affiliate operation. Faced with unrecoverable encrypted files, the victim company sought guarantees from the threat actors that their data would indeed be decrypted and kept private if a ransom was paid.
In email correspondence reviewed by investigators, a Dharma representative advised the victim to bypass traditional channels and establish contact with a specific IT professional in Canada who specialized in securing such guarantees, directing them to an email address linked to the handle "ghostbyte." While it remains undetermined whether Tobok actively utilized the specific address provided by the ransomware affiliate, digital intelligence firm Constella Intelligence identified that an email address frequently used by Tobok was tied to multiple online accounts bearing the username ghostbyte, including a Snapchat profile. Furthermore, financial tracking revealed that cryptocurrency wallets associated with the Dharma representative had processed substantial bitcoin transactions totaling millions of dollars.
Representatives for Cypfer issued statements emphasizing that the firm’s official business model does not involve facilitating or making ransomware payments, noting that company leadership learned of Dubrovsky’s arrest through media reports. Cypfer stressed that it had received no outreach from law enforcement and was not the target of any active investigation. The firm recently underwent an acquisition by the Apros Group, a holding company led by Jason Hogg, a former FBI special agent and former CEO of Aon Cyber Solutions Group. Aon had previously acquired Cytelligence, a security consulting firm where Tobok served as founder and CEO and Dubrovsky operated as a managing partner.
CONFLICTING INTERESTS
Under U.S. law, paying a ransom to recover encrypted systems or secure promises of data deletion is not inherently illegal, provided the extortionist group is not designated as a sanctioned entity by the U.S. Treasury Department. Because ShinyHunters has not received official government sanctions, victim organizations frequently find themselves navigating complex dilemmas, often directed by cyber insurance providers to retain specialized incident response firms.

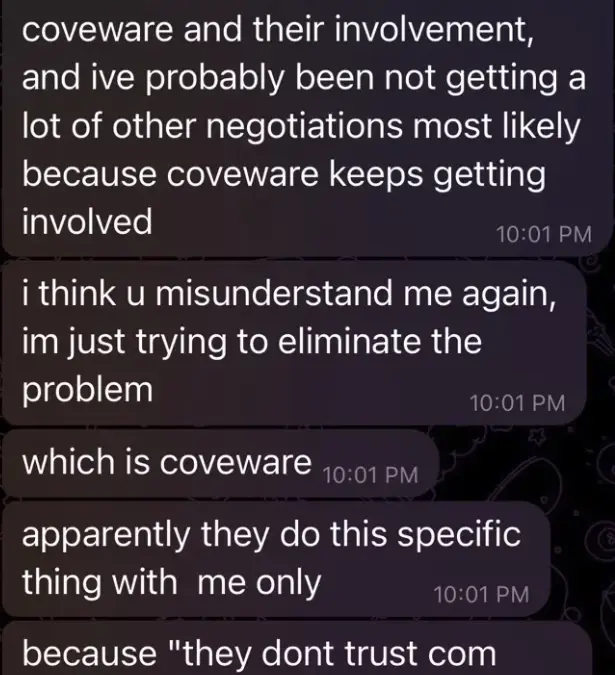
However, philosophical divisions run deep within the breach response industry. While firms like Coveware and Unit 221B consistently advise clients against paying ShinyHunters—warning that cybercriminals frequently retain or resell stolen data regardless of payment—other firms readily facilitate transactions. This divergence has placed remediation firms in the crosshairs of the hackers themselves. Internal Telegram chats reviewed by investigators revealed intense frustration among ShinyHunters leaders, who explicitly complained that Coveware’s steadfast refusal advice was severely damaging their monetization rates and actively plotting to "eliminate the problem."
Industry leaders have increasingly pointed to inherent conflicts of interest within the negotiation ecosystem. Mark Camillo, chief executive of CyberAcuView, an organization established by cyber insurance carriers, noted that while some firms charge flat retainers, others derive their fees as a direct percentage of the total ransom paid. This financial structure creates perverse incentives for negotiators to maximize payouts rather than aggressively negotiate down demands.
Federal prosecutors have increasingly targeted these compromised arrangements. The U.S. Department of Justice charged MonsterCloud CEO Zohar Pinhasi with wire fraud and conspiracy, alleging he secretly paid ransomware groups millions behind his clients’ backs while inflating remediation bills. Similarly, a Florida-based ransomware negotiator was sentenced to prison for conspiring with the BlackCat/ALPHV syndicate to feed confidential victim negotiation strategies directly to hackers to maximize extortion payouts.
Leave a Reply