Federal Bureau of Investigation agents in Pennsylvania have arrested a prominent Canadian cybersecurity executive on federal cyber extortion and conspiracy charges, marking a dramatic escalation in an ongoing investigation into the notorious ShinyHunters hacking group. Multiple sources close to the inquiry confirmed the arrest to KrebsOnSecurity, which follows a brazen cyberattack by the syndicate that compromised sensitive personnel files and internal records belonging to thousands of federal agents.
The arrest was initially reported by The New York Times, which revealed that federal law enforcement took a Canadian man into custody in Pennsylvania on suspicion of assisting ShinyHunters. While neither the Times nor an official social media statement from FBI Director Kash Patel explicitly identified the individual at the time, federal court records and industry sources confirmed the suspect is Edward Dubrovsky, a well-known Canadian security professional and author specializing in ransomware negotiations.
According to sources familiar with the matter, Dubrovsky was visiting Pennsylvania to attend a major cyber insurance conference when federal agents moved in to make the arrest. Investigators believe Dubrovsky’s professional background in handling ransomware negotiations and cyber extortion advisory services intersects with the wide-reaching federal probe into the syndicate. Furthermore, sources indicated that control and oversight of the sprawling ShinyHunters investigation have recently been centralized at an FBI field office in Texas, signaling the growing scale and priority of the case within the federal law enforcement apparatus.
An online review of industry events shows that the Cyber Risk Summit was held at the Loews Philadelphia Hotel from October 5 to October 7. While the conference featured numerous sponsors, summit documentation lists a Canadian security firm known as Cypfer as its primary sponsor. Public professional networking profiles indicate that Dubrovsky was historically associated with Cypfer, though a corporate spokesperson clarified that he served as a managing director prior to his resignation in December 2025, rather than holding a founder or co-founder title as his profile claimed. Following his departure from Cypfer, Dubrovsky became associated with CyberSteward, another Canadian security firm and conference sponsor. Approximately one month prior to his arrest, Dubrovsky shared on professional platforms that he intended to attend the Philadelphia summit alongside members of the CyberSteward team, looking forward to continuing industry discussions regarding global ransomware advisory and compliant-driven settlement services.

Federal court filings indicate that an individual named Edward Dobrovsky—with a slight spelling variation in the surname—was formally charged in Pennsylvania on October 8 with conspiracy to threaten to impair the confidentiality of information with the intent to extort money, alongside charges of interference with commerce by threats. While the core criminal complaint and several related documents remain sealed by the court, an indexed summary of the charges became publicly available through legal documentation platforms.
U.S. Bureau of Prisons records initially placed a 54-year-old Edward Dubrovsky at a federal holding facility in Philadelphia. However, court docket entries show that a notice was filed on October 9 transferring the legal proceedings to the U.S. District Court for the Eastern District of Texas, aligning with reports that Texas has become the central hub for the federal government’s crackdown on the ShinyHunters network. The FBI has declined to comment on the ongoing legal proceedings.
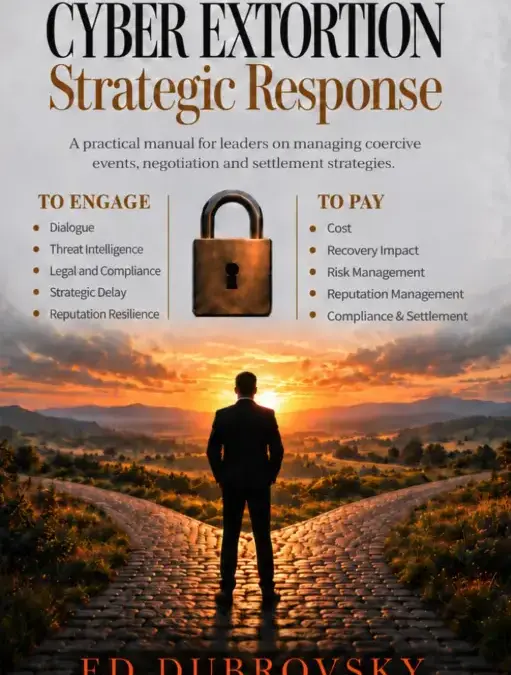
Dubrovsky is widely recognized in cybersecurity circles as a specialist in crisis management and the author of "Cyber Extortion Strategic Response," a 252-page publication focusing on decision-making processes during corporate ransomware attacks. Promotional summaries for the book emphasize the author’s premise that active communication with malicious actors is distinct from agreeing to financial ransom demands, noting that engagement can serve tactical goals such as information gathering, claim verification, and buying critical time for victimized organizations.
At the time of his initial court appearance, Dubrovsky had not yet retained legal counsel or been assigned a public defender, and he could not be immediately reached for comment. Representatives for CyberSteward have not yet issued a public statement regarding the arrest.
The arrest of the cybersecurity executive unfolds against the backdrop of an intense international manhunt targeting the core infrastructure of ShinyHunters. The syndicate has historically relied on targeted phishing campaigns and compromised credentials to infiltrate corporate software-as-a-service environments, siphoning massive volumes of proprietary data and threatening public exposure unless substantial cryptocurrency ransoms are paid. According to official federal estimates, the hacking collective has successfully extorted more than $70 million from corporate and organizational victims throughout the year.

Law enforcement pressure on the group has intensified significantly in recent weeks. Sources indicate that federal investigators have spent considerable time analyzing digital hardware and devices seized by Dutch law enforcement last month during the arrest of Pepijn van der Stap, a reformed cybercriminal apprehended in connection with the broader ShinyHunters investigation. Furthermore, legal and intelligence sources suggest that additional criminal charges against principals at other firms specializing in ransomware negotiation could be forthcoming as the inquiry widens.
The pressure on the hacking collective also triggered erratic and brazen behavior from within the group’s leadership ranks. Immediately following the arrest of Van der Stap, an operative utilizing the alias "Rey" assumed operational control of ShinyHunters. The newly elevated administrator began openly taunting federal authorities over a major security breach that allowed the group to compromise data from the FBI’s online recruitment portal, exposing sensitive personal details including unit assignments, professional specializations, and confidential medical and psychological evaluations.
Investigative reporting from Reuters revealed that the individual operating under the handle "Rey" was actually a teenager named Saif Al-din Khader. Law enforcement agencies subsequently detained Khader, who has reportedly begun cooperating with federal investigators. Additional reporting detailed how Khader was apprehended just as the cybercrime collective attempted to execute an extortion scheme against a digital navigation and aviation unit recently divested by Boeing.
As federal authorities continue to examine seized electronic evidence, cross-border cooperation between North American and European law enforcement agencies remains active. The investigation into both the hackers and the intermediaries who navigate the murky waters of digital extortion is expected to yield further developments as court proceedings advance in Texas.