
Recent measurements investigating the surprisingly high volume of repeat queries in the Domain Name System (DNS) have yielded an unexpected discovery: simply adding a second authoritative nameserver to a domain significantly reduces the number of duplicate queries sent by recursive resolvers.
The findings provide a fresh look at underlying operational dynamics across the global internet, shedding light on how recursive resolvers and modern ISP infrastructure handle negative or missing responses. The research follows an initial study published in early September 2026 under the title "What part of ‘No!’ is so hard for the DNS to understand?" That earlier analysis examined a scenario where millions of users were tasked with resolving a unique DNS name specifically designed to bypass conventional DNS caching.
During the initial measurement window from August 5 to August 11, 2026, researchers tracked various negative response types alongside standard control tests. The baseline measurements revealed distinct behavioral patterns depending on the type of response returned by the single authoritative nameserver configured for the test zones.
When dealing with definitive negative responses such as NXDOMAIN and NODATA, or standard positive responses, the query repetition profile remained relatively modest. On average, tests recorded about four queries total. Roughly 55% to 60% of these test cases completed successfully with a single query. Where repetition did occur, the average number of repeat queries hovered between four and six.
However, when the DNS infrastructure encountered non-definitive responses, the behavior changed drastically. For instance, a REFUSED response completed with a single query roughly 40% of the time, but triggered an average of 11 additional repeat queries in other instances. More extreme patterns emerged with SERVFAIL and NO RESPONSE outcomes, which drove up averages significantly. SERVFAIL cases recorded an average of 51.73 queries per test, while NO RESPONSE scenarios surged to an average of 83.46 queries per test, with the vast majority being repetitive transmissions of the original query.
The original methodology utilized a single nameserver that was authoritative for each zone. The global internet was divided into six distinct geographical zones for the measurement setup: North America, South America, Europe and Africa, India, Asia, and China. Within each of these zones, a single dual-stack authoritative nameserver was deployed, providing both IPv4 and IPv6 addresses.
This setup prompted an obvious operational question: would the volume of queries increase or decrease if a zone was served by more than one dual-stack nameserver? Traditional networking expectations suggested that adding authoritative servers might increase the repeat query count. The common assumption was that obsessive recursive resolvers would query every available authoritative nameserver with the identical query to verify that all servers responded with mutually consistent data.

To test this hypothesis, researchers repeated the control measurement using two authoritative dual-stack nameservers instead of one. The results completely defied conventional expectations.
With a single nameserver, approximately 58% of the test cases completed the experiment using a single DNS query for each query type. When a second nameserver was introduced, that single-query completion rate jumped to 71%. Simultaneously, the overall average number of queries per test dropped from 3.43 down to 2.57. Furthermore, in instances where queries were repeated, the average number of repeat queries fell from 3.8 down to 2.6.
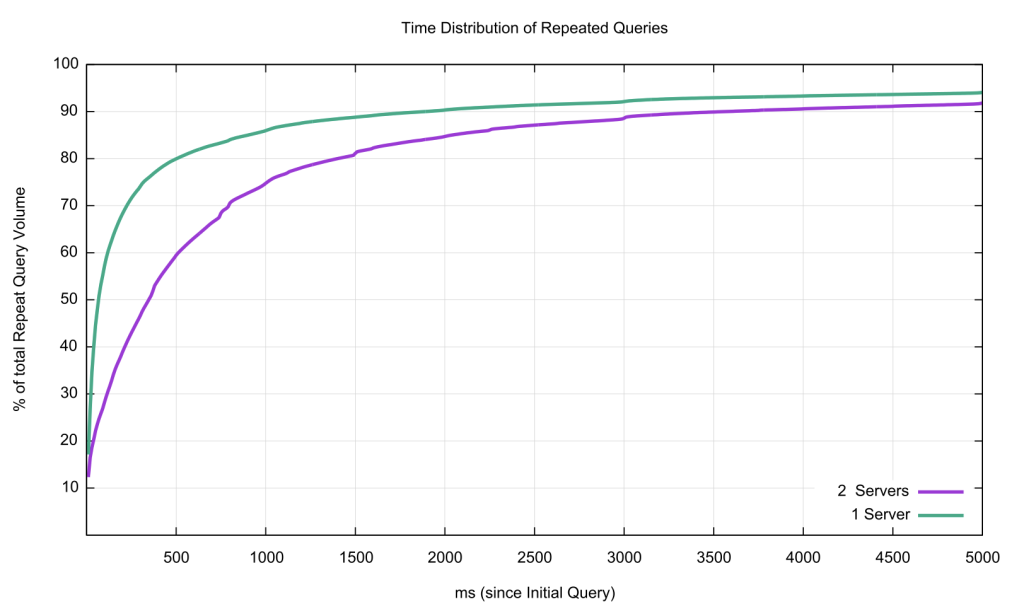
Analyzing the temporal distribution of these repeat queries offered further clues into resolver mechanics. When looking at the cumulative distribution over time, the most notable difference in query duplication occurred during the very first second of DNS name resolution. Slightly more than 85% of duplicate queries arrived within that initial window when using a single nameserver. In contrast, that figure dropped to 75% when two nameservers were present.
The two-nameserver configuration also displayed traits resembling an exponential backoff behavior, characterized by slight peaks in repeat queries at 0.75 seconds, 1.5 seconds, and 3 seconds. Across both configurations, roughly 90% of all repeated queries were observed within five seconds of the initial lookup.
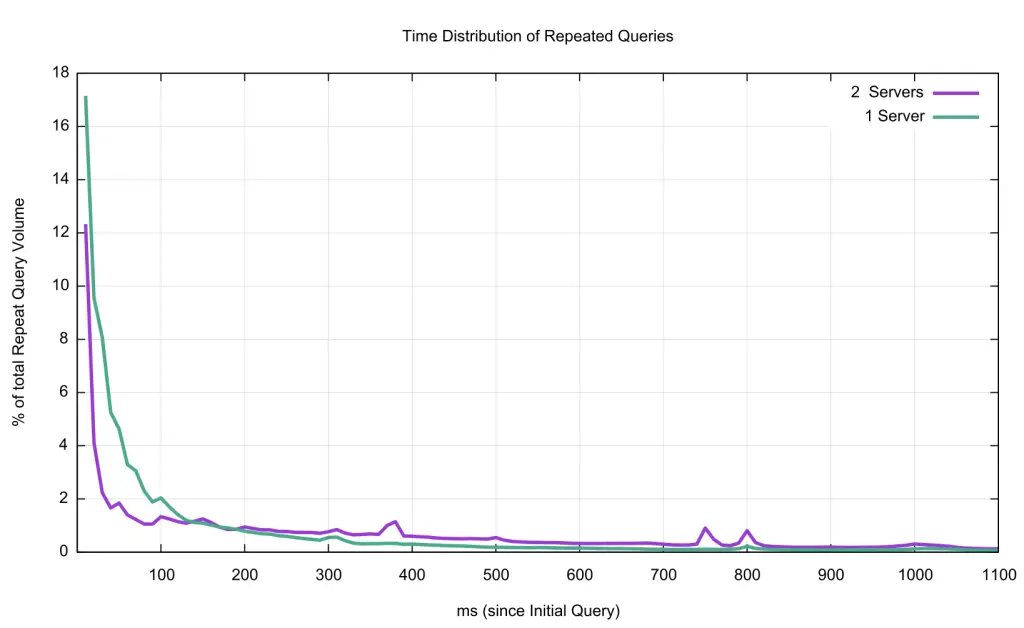
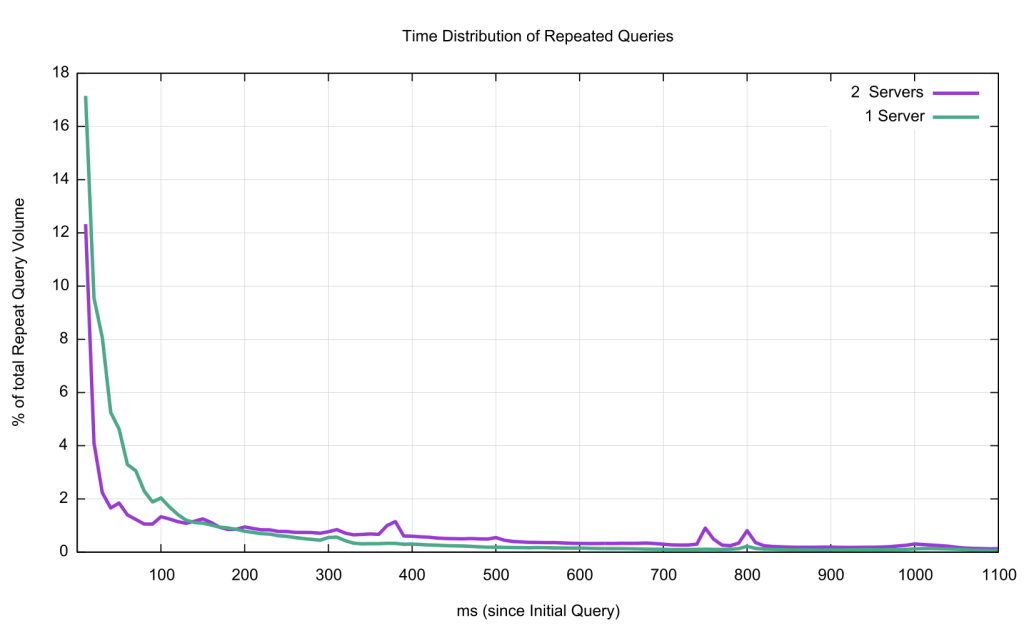
A more granular view of the timing distribution revealed even sharper operational nuances. In the single-nameserver setup, 17% of all repeated queries materialized within 10 milliseconds of the initial query—a rapid-fire duplication pattern well below the typical User Datagram Protocol timeout values of individual resolvers. When a second nameserver was introduced, this rapid-fire duplication dropped to 12% of all repeated queries. While the single-nameserver configuration showed local peaks of duplicate queries at 100ms, 310ms, and 800ms, the two-nameserver setup exhibited peaks at 50ms, 100ms, 310ms, 370ms, 750ms, and 800ms.
Investigating the root cause of this rapid-fire duplication points toward the architecture of modern resolver farms. Large consumer internet service providers routinely handle query volumes that surpass the capacity of individual computing platforms. To manage this scale, operators commonly deploy resolver farms featuring a front-end query dispatcher that sits in front of a cluster of individual recursive resolvers.
A prominent example of this architectural pattern is PowerDNS’s DNSdist tool. In many standard configurations, a front-end dispatcher interacts with the public internet via a public IP address while utilizing private IP addresses internally to route traffic among individual recursive backend engines. Consequently, an entire resolver farm appears to the outside world as a single entity behind a single public IP address.
The query repetition behavior observed during the measurements is now widely attributed to the internal mechanics of these front-end systems rather than faulty implementation in recursive resolver codebases. When facing a domain backed by only a single authoritative nameserver, a front-end dispatcher may duplicate incoming queries across multiple internal resolver instances simultaneously to optimize resolution speed and enhance service resilience.
While observing a drop in query repetition upon adding a second authoritative server remains counterintuitive, it underscores the opaque nature of how the modern DNS handles individual queries. Nevertheless, the empirical findings validate longstanding operational advice. Maintaining a minimum of two nameservers to serve a zone remains a cornerstone of sound DNS configuration, demonstrating a practical benefit in keeping recursive resolvers stable across the broader internet ecosystem.
Leave a Reply