The complex architecture that allows IPv4 and IPv6 networks to coexist securely is facing fresh scrutiny following the publication of new cybersecurity research. In a paper accepted for the USENIX Security 2026 conference, a team of researchers from Tsinghua University has detailed a novel Pulsing Denial-of-Service technique known as TED. The method exposes how permissive tunnel hosts and complex IPv6 Extension Headers can be manipulated to transform transparent network relays into programmable delay lines, creating a unique challenge for global network operators.
IP tunneling has long served as a vital mechanism for modern networking, enabling seamless site interconnection, mobile communications, satellite connectivity, and virtual private networks by encapsulating data packets within outer IP headers. Under normal operating conditions, a destination endpoint simply removes the outer header and forwards the inner packet to its final destination. However, the researchers discovered that this transparency can quickly transform into a significant security blind spot when the encapsulated traffic carries complex chains of IPv6 Extension Headers, such as Fragment, Routing, and Destination Options headers.
Why Revisit Tunnel Security?
The research stems from a fundamental vulnerability shared by several widely deployed tunnel protocols: they frequently provide neither authentication nor encryption by default. Without effective peer validation and robust forwarding controls, an exposed endpoint can easily accept encapsulated traffic from unauthorized senders, effectively acting as an open relay that forwards decapsulated inner packets without proper authorization or filtering.
Furthermore, routers, firewalls, and tunnel implementations handle IPv6 Extension Headers with notable inconsistency. During their extensive internet measurements, the researchers observed that many tunnel hosts routinely inspected only the bare minimum required for basic forwarding. This lax inspection allowed deeply nested inner headers to survive the decapsulation process entirely intact, bypassing normalization or rejection checks that should have stopped malformed or suspicious traffic.
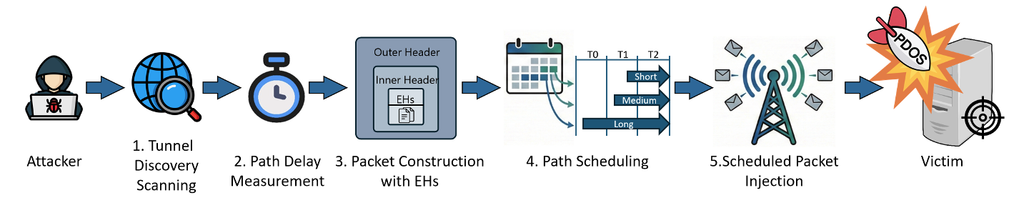
Tunnels accomplish far more than simple traffic relaying; the complex processing required for Extension Headers, combined with multi-hop routing paths, introduces varying and partly controllable delays. By employing reverse-order scheduling—where packets destined for long paths are transmitted before those assigned to short paths—an attacker can leverage accurate delay estimates to cause disparate data streams to converge precisely at a chosen target and time.
From Transparent Forwarding to a Programmable Pulse
The newly detailed technique organizes its operational cycle into five distinct phases, moving from initial host discovery to precise timing synchronization. The process begins with the identification of permissive tunnel hosts, followed by the measurement of EH-aware delays, the construction of deeply nested packets, and the careful scheduling of a common arrival window at the targeted destination.
Executing this technique requires specific operational prerequisites. Attackers must possess raw-packet transmission capabilities, network paths must permit nested encapsulation alongside relevant Extension Headers, and the target environment must lack rigorous source address validation. Moreover, one-way delay estimates must align closely with reality, as unforeseen route changes, network filtering, packet loss, and clock drift can quickly erode synchronization fidelity. Consequently, the research highlights a measured and conditional attack surface rather than a universal vulnerability capable of targeting any host at any given moment.
Examining the Exposed Attack Surface
To quantify the scope of the problem, the research team conducted an extensive series of internet-wide scans between June 2025 and January 2026. Performing 44 separate scans at randomized intervals across approximately 3.7 billion IPv4 addresses and 20 million IPv6 Hitlist addresses, they identified nearly two million cumulative hosts that successfully passed forwarding tests across six distinct tunnel protocols.
The observed protocols included classic 6to4 configurations, 4in6 setups, Generic Routing Encapsulation (GRE), GRE6, IPIP, and IP6IP6 tunnels. The cumulative results revealed hundreds of thousands of responsive hosts for several protocols, underscoring the widespread prevalence of permissive tunnel configurations across global public infrastructure.
The interaction with IPv6 Extension Headers proved equally significant during the measurements. Average EH survivability exceeded seventy percent among the tested IPv6 tunnel hosts, and a vast majority of cases demonstrated a measurable increase in processing delay following the insertion of Extension Headers. Across controlled testing environments, the vast majority of one-way-delay estimation errors remained within narrow margins, validating the feasibility of tightly controlled pulse windows.

Insights from Controlled Experiments
To ensure safety and ethical rigor, the researchers avoided targeting operational third-party services. Instead, they deployed six controlled dual-stack targets across geographically diverse regions, including China, Japan, Germany, and the United States. By carefully measuring Path MTU limits, capping intermediate hosts, and repeating scenarios multiple times, they gathered granular comparative data.
While a single-hop baseline transmitted thousands of packets through naturally distributed tunnel delays, the multi-hop pulse technique redistributed large volumes of traffic across a span of several seconds. The results showed that the vast majority of packets converged within a fraction of a second, creating a narrow arrival window where the peak packet rate vastly exceeded the sender’s average transmission rate.
The researchers emphasize that this amplification metric measures temporal concentration—the target’s peak packet rate divided by the average send rate—rather than byte amplification or artificial traffic generation by the tunnel hosts themselves. Instead, it demonstrates how widely dispersed traffic can be artificially synchronized into an intense instantaneous burst capable of overwhelming a target link or buffer queue.
Operational Challenges and Practical Mitigations
For network operators, the primary challenge lies in visibility. While conventional application-layer defenses easily block abused Domain Name System or Network Time Protocol services, this technique operates entirely below the application layer. The target destination observes ordinary decapsulated traffic originating from multiple legitimate-looking paths, while each intermediate network observes only a modest local rate, failing to inspect deeply enough to recognize a coordinated, multi-path pulse.
Furthermore, tunnel exposure frequently crosses critical administrative boundaries. The research team identified numerous responsive GRE and GRE6 addresses within specific Autonomous System prefixes, with reverse DNS entries occasionally associating them with user terminals and ground points of presence operated by satellite internet providers. Although the researchers strictly avoided utilizing operational satellite services as victims, the findings serve as a stark reminder that strict inbound filtering rules may still admit selected encapsulation protocols, inadvertently extending relay exposure into satellite and mobile networks.
Network administrators can take immediate, practical steps to mitigate these risks by modernizing their infrastructure policies. Recommendations include restricting tunnel peers to explicitly configured or authenticated endpoints, disabling open internet-facing decapsulation, and implementing rigorous ingress and egress source address validation for both outer and inner packets.
Operators should also limit packet recursion by dropping or quarantining unexpected nesting depths, as nesting levels greater than one are exceedingly rare in legitimate enterprise deployments. Additionally, network teams should constrain risky Extension Header chains by blocking deprecated routing headers, limiting repeated fragment headers, and rejecting unneeded combinations through role-specific allowlists rather than indiscriminate blocking.
Enhancing operational visibility is equally crucial. By exposing telemetry counters for tunnel depth, extension header types, processing failures, and unexpected inner source addresses, operators can better inspect and normalize traffic before forwarding. Implementing short-window queue, loss, and arrival-rate monitoring can also help teams detect coordinated pulses before they impact critical systems, ensuring that infrastructure remains resilient against complex, multi-layered transport exploits.