
Federal law enforcement authorities have arrested a prominent executive at a Canadian cybersecurity firm in connection with an intensifying, high-stakes investigation into the notorious ShinyHunters hacking group. The syndicate recently managed to infiltrate the Federal Bureau of Investigation itself, relieving the agency of sensitive, non-public data concerning thousands of law enforcement personnel.
According to multiple sources familiar with the matter, the arrest took place in Pennsylvania. The New York Times was first to report that federal agents had taken a Canadian man into custody on suspicion of providing assistance to the ShinyHunters collective, though initial official announcements refrained from naming the suspect. A brief statement posted to social media by FBI Director Kash Patel confirmed the arrest but similarly omitted specific personal details regarding the individual in custody.
Sources close to the ongoing investigation indicate that the Canadian executive was visiting Pennsylvania to attend a prominent cyber insurance and risk management conference. The suspect’s professional background is deeply intertwined with the specialized sector of handling ransomware negotiations and extortion advisories on behalf of corporate clients facing digital coercion. Furthermore, sources have confirmed that control and oversight of the sprawling ShinyHunters investigation have now been centralized at a primary FBI field office located in Texas.
An examination of public schedules and online registries reveals that the Cyber Risk Summit was convened at the Loews Philadelphia Hotel. The multi-day conference drew numerous sponsors from across the insurance and security sectors. According to the summit’s official documentation, its single largest corporate sponsor was Cypfer, a prominent Canadian cybersecurity organization specializing in incident response and digital threat mitigation.
Public professional network profiles indicate that one of Cypfer’s early figures was Edward Dubrovsky. Dubrovsky subsequently transitioned to another Canadian security firm and conference sponsor, CyberSteward. Approximately one month prior to the unfolding events, Dubrovsky shared updates online indicating his intention to travel to the Cyber Risk Summit alongside members of the CyberSteward team to participate in industry dialogues.

A spokesperson for Cypfer subsequently clarified that Dubrovsky was not a founder or co-founder of the firm as his professional profile had claimed, but rather served in the capacity of managing director before ultimately submitting his resignation in November 2025.
In a public post leading up to the conference, Dubrovsky had expressed enthusiasm for ongoing industry discourse, writing that he looked forward to continuing conversations surrounding strategy and compliant-driven coercive ransomware advisory, negotiations, and global settlement services.
Federal court records reveal that an individual named Edward Dobrovsky—noting a minor spelling variation in the surname—was formally arrested in Pennsylvania on cyber extortion and conspiracy charges. A significant portion of the foundational court documents, including the primary criminal complaint, have been placed under seal by the court. However, a select number of filings were indexed publicly on legal monitoring platforms, including a summary of the charges brought against the defendant. The documents charge the individual with conspiracy to threaten to impair the confidentiality of information with the intent to extort money, alongside charges of interference with commerce by threats.
Inmate locator records maintained by the U.S. Bureau of Prisons indicate that a 54-year-old named Edward Dubrovsky is currently being detained at a federal detention facility in Philadelphia. Concurrently, court dockets reflect a procedural transfer on October 9 moving the case to the U.S. District Court for the Eastern District of Texas, which sources identify as the current nerve center for the federal government’s comprehensive ShinyHunters probe. The FBI has consistently declined to comment on the specifics of the ongoing prosecution.
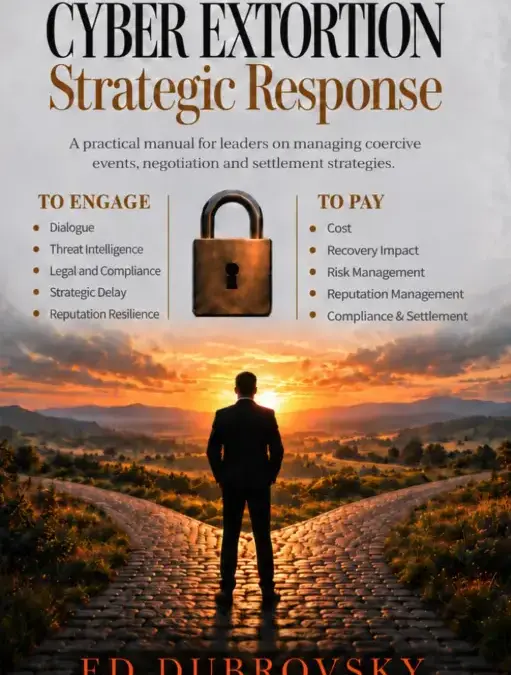
In addition to his corporate advisory roles, Dubrovsky’s professional profile notes that he is the author of a comprehensive text on cyber extortion response. The 252-page volume purports to guide organizations beyond the initial ransom note and into the critical decision-making processes that dictate how an enterprise responds, recovers, and protects core assets following a breach. An excerpt from the book’s retail description emphasizes a central tenet of modern incident management: communicating with a digital criminal is fundamentally distinct from negotiating a payment, and negotiation itself does not constitute a commitment to fulfill financial demands. The text argues that active engagement can serve alternate tactical objectives, including testing adversary claims, intelligence gathering, buying operational time, and preserving strategic options while leadership evaluates subsequent moves.
Mr. Dubrovsky could not be reached immediately for comment following his apprehension. Inquiries directed to other executives at CyberSteward yielded no immediate response. Available judicial records indicate that the defendant does not currently retain private legal representation and has yet to have a public defender formally appointed by the court.

The ShinyHunters cybercrime syndicate has established a reputation for utilizing sophisticated phishing campaigns and stolen credentials to siphon massive repositories of proprietary data from corporate accounts residing on software-as-a-service platforms. The group typically leverages this stolen material by threatening public disclosure unless substantial cryptocurrency ransoms are satisfied. According to federal estimates, the collective has successfully extorted upward of $70 million from corporate and organizational victims throughout the course of the year.
Law enforcement operations against the group have accelerated following a series of international breakthroughs. Sources report that federal investigators have spent weeks poring over digital devices and hardware seized last month when Dutch police apprehended reformed hacker Pepijn van der Stap in connection with the broader ShinyHunters inquiry. Furthermore, investigators indicate that criminal charges against principals at additional firms specializing in ransomware negotiation may be imminent.
The pressure on the hacking collective mounted rapidly following Van der Stap’s apprehension. An operative operating under the online moniker "Rey" assumed operational control of ShinyHunters and began publicly taunting federal authorities regarding a major data breach. The group claimed responsibility for infiltrating an online recruitment portal utilized by the FBI itself, acquiring personnel records detailing unit assignments, specialized roles, and sensitive medical and psychiatric files.
Investigative reports subsequently identified "Rey" as a teenager named Saif Al-din Khader. Law enforcement detained the young hacker, who is reportedly cooperating with federal investigators. The apprehension occurred as the cybercrime unit allegedly attempted an extortion scheme targeting a digital aviation and navigation unit that had been divested by aerospace giant Boeing late the previous year.
As federal authorities continue to execute search warrants, analyze seized digital evidence, and examine the intersection between corporate incident response firms and cybercriminal extortionists, the investigation remains exceptionally dynamic.
Leave a Reply