As global networks continue the complex, multi-year transition from IPv4 to IPv6, network operators rely heavily on IP tunneling protocols to bridge compatibility gaps. These mechanisms allow packets to be encapsulated within outer IP headers, supporting everything from seamless IPv4 and IPv6 coexistence and site-to-site interconnections to virtual private networks, mobile services, and satellite infrastructures. However, a groundbreaking new cybersecurity study reveals that this foundational architectural transparency harbors a significant and largely overlooked security blind spot.
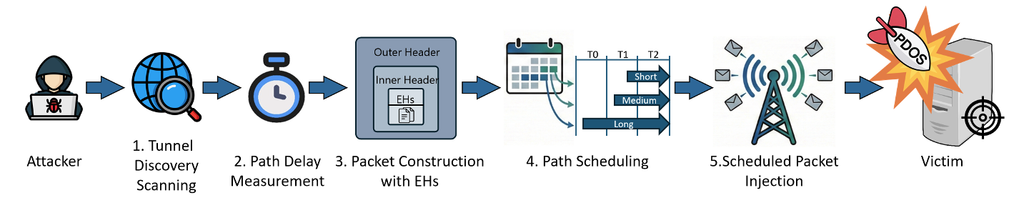
In a research paper presented at the USENIX Security 2026 conference, a team of computer scientists from Tsinghua University—comprising Le Gai, Lin He, Ying Liu, Zedong Jia, Daguo Cheng, and Chentian Wei—introduced a sophisticated threat vector dubbed TED. This newly unveiled Pulsing Denial-of-Service (PDoS) technique demonstrates how permissive, misconfigured, or unsecured tunnel hosts can be inadvertently transformed into programmable delay lines. By exploiting complex IPv6 Extension Header (EH) chains and nested routing paths, the technique allows bad actors to manipulate packet transit times with surgical precision, compressing dispersed traffic streams into sudden, high-intensity arrival bursts at targeted network destinations.
Unlike conventional denial-of-service vectors that rely heavily on third-party application-layer infrastructure such as the Domain Name System, the Network Time Protocol, or expansive Content Distribution Networks to amplify or distribute traffic, TED operates entirely at the network and transport layers. It harnesses the inherent physical properties and routing behaviors of the underlying internet infrastructure itself, raising urgent questions about how autonomous systems manage encapsulation, packet forwarding, and header inspection.
Reassessing the Vulnerability of Legacy and Modern Tunnels
To understand the mechanics behind TED, security analysts must revisit the fundamental assumptions of tunnel security. Several widely deployed and standard tunneling protocols—including classic mechanisms like 6to4, IPIP, and generic routing encapsulation (GRE), alongside their IPv6-native counterparts—provide neither built-in authentication nor mandatory encryption by default. Without strict peer validation, robust cryptographic verification, and stringent forwarding controls, an exposed network endpoint can easily accept encapsulated traffic from unauthorized external senders.
In practice, this turns the host into an open relay. Once the endpoint receives a packet, it strips away the outer IP header and blindly forwards the inner packet toward its ultimate destination without verifying whether the original transmission was legitimate.
Compounding this relay risk is the complex architecture of IPv6. The protocol permits various extension headers—such as Fragment, Routing, and Destination Options headers—to be chained together sequentially. However, routers, corporate firewalls, and tunnel implementations across the global internet handle these specialized headers with frustrating inconsistency. During extensive measurements, the research team discovered that many tunnel hosts inspect only the bare minimum required to satisfy basic packet forwarding. Consequently, deeply nested inner headers frequently survive the decapsulation process entirely intact, bypassing normalization, scrubbing, or rejection filters that might otherwise neutralize potential threats.
Tunnels, therefore, accomplish much more than simple traffic relaying. The intricate processing required for complex extension headers, combined with multi-hop routing paths, creates distinct and partly controllable packet delays. By leveraging reverse-order scheduling—where long-path packets are deliberately transmitted before short-path packets—an attacker can calculate precise transit durations to ensure that packets originating from disparate geographic locations converge at a precise target at the exact same moment.
Evaluating the Global Attack Surface
The researchers mapped out the sheer scale of this exposed infrastructure through an extensive series of Internet-wide scans conducted between June 2025 and January 2026. Over the course of 44 randomized scanning intervals covering approximately 3.7 billion IPv4 addresses and 20 million IPv6 Hitlist addresses, the team identified nearly two million unique hosts that successfully passed forwarding tests across six distinct tunnel protocols.
The cumulative findings highlighted widespread exposure across multiple protocol implementations. Observed vulnerable hosts included hundreds of thousands of addresses utilizing legacy and modern architectures, such as 6to4, 4in6, GRE, GRE6, IPIP, and IP6IP6 implementations. The researchers emphasize that these figures represent a cumulative inventory rather than a static live census, meaning that specific addresses, routing policies, and operational filtering rules naturally fluctuate over time. Nevertheless, the data confirms that a massive pool of permissive relay endpoints remains accessible across the global public internet.
Furthermore, the interaction with IPv6 extension headers proved substantial. Average EH survivability exceeded seventy percent among the tested IPv6 tunnel hosts, and the vast majority of test cases demonstrated a measurable, significant increase in processing delay following the insertion of extension headers. Controlled delay-estimation experiments revealed that the vast majority of one-way-delay calculations remained within a tight margin of error, validating the operational feasibility of a narrow twenty-millisecond pulse window.

Controlled Experiments and Temporal Concentration
To evaluate the real-world impact of the technique without disrupting operational services or targeting third-party networks, the researchers deployed six controlled, dual-stack experimental targets strategically situated in disparate regions, including China, Japan, Germany, and the United States. By meticulously measuring path maximum transmission unit limits, capping intermediate host packet rates, and repeating controlled scenarios multiple times, the team established a clear baseline comparison.
A standard single-hop baseline transmitting thousands of packets through natural, unmanaged tunnel delays produced a broad, diffuse traffic profile. In contrast, deploying the multi-hop scheduling techniques of TED successfully synchronized tens of thousands of packets across a multi-second transmission window. The vast majority of these packets arrived at the controlled target within a fraction of a second, with the peak arrival rate inside the critical twenty-millisecond window skyrocketing to over 180 times the sender’s average transmission rate.
This dramatic metric measures temporal concentration rather than byte amplification. The tunnel hosts themselves do not generate artificial traffic volume; instead, they act as temporal lenses, successfully synchronizing widely dispersed, low-rate traffic into a sudden, highly concentrated instantaneous burst capable of overwhelming downstream link capacity or exhausting router queue buffers.
Practical Mitigations for Network Operators
As networking professionals digest these findings, cybersecurity experts emphasize that traditional defenses are insufficient to counter infrastructure-level pulsing techniques. Because TED operates beneath application-layer visibility, conventional defenses designed to block abused DNS or NTP services are ineffective. To the targeted network, the incoming assault simply appears as ordinary decapsulated traffic arriving legitimately from a multitude of diverse routing paths. Meanwhile, each intermediate network observes only a modest local packet rate, failing to recognize that it is participating in a larger, coordinated pulsing campaign.
To mitigate these risks, network operators and infrastructure vendors must adopt a proactive, multi-layered defense strategy. First, organizations should strictly restrict tunnel peers by accepting encapsulated traffic exclusively from pre-configured or cryptographically authenticated endpoints, effectively disabling open, internet-facing decapsulation services. Second, rigorous source address validation must be applied to both outer and inner packets, cross-referencing inner sources against verified customer bases and expected address prefixes.
Operators should also implement strict limits on packet recursion and nesting depth, dropping or quarantining unexpected nested structures, as legitimate network designs rarely require nesting depths greater than one. Additionally, risky extension header chains—such as deprecated routing headers and excessive fragment headers—should be tightly constrained or blocked entirely unless specifically required by authorized network functions. Implementing comprehensive monitoring to detect sudden anomalies in short-window queue behavior, packet loss, and arrival rates can also help identify when low local tunnel rates are covertly combining into dangerous destination bursts.
Ultimately, the research serves as a critical reminder of the unforeseen security complexities inherent in network protocol transitions. As organizations continue modernizing their infrastructure, securing encapsulation boundaries and ensuring transparent extension header processing will remain paramount to maintaining internet stability and resilience.