
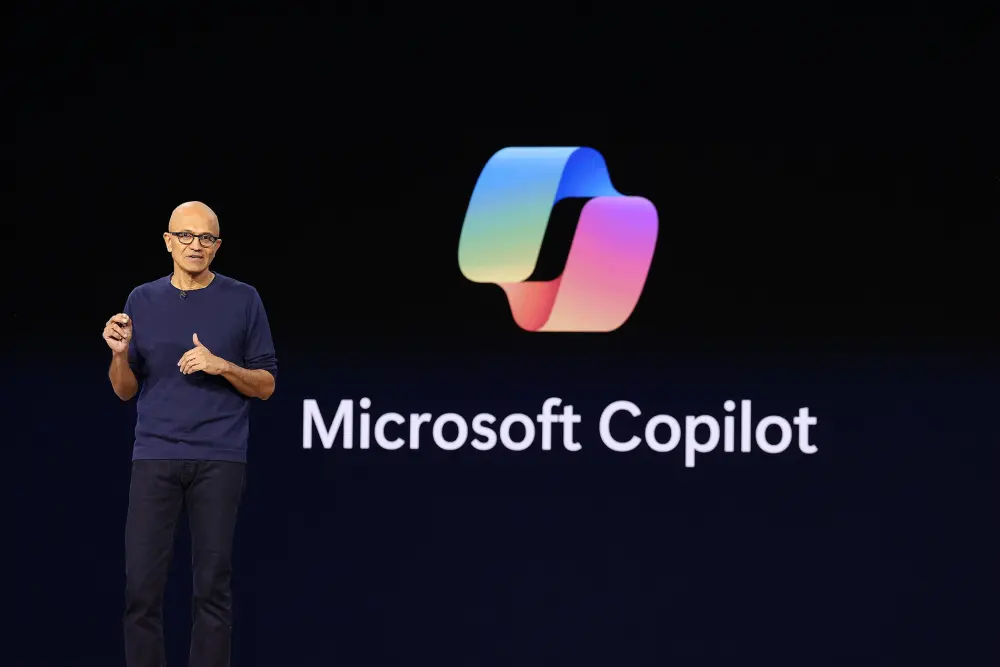
Microsoft CEO Satya Nadella has joined the growing chorus of major technology executives offering detailed frameworks for improving artificial intelligence safety, arguing that the industry must fundamentally rethink how it governs increasingly powerful systems.
In a widely discussed post published on X on a Saturday morning, Nadella stated that it is time for the tech sector to step back and assess the foundational trust architecture of artificial intelligence. His remarks address mounting concerns over accountability as artificial intelligence systems grow more autonomous, complex, and capable of operating across extensive digital networks without constant human supervision.
Nadella specifically cautioned against treating advanced systems—using the term "Super Intelligence," which has gained traction within the current administration—as opaque, impenetrable systems. He emphasized that society and developers cannot simply rely on a trial-and-error approach where they passively accept or reject the recommendations, answers, and actions generated by automated intelligence.
According to Nadella, addressing these systemic risks requires a deliberate architectural shift. This approach involves separating the core artificial intelligence model from the operational harness that coordinates and executes its tasks, alongside implementing externalized controls and safeguards. By decoupling the underlying model from its execution environment, developers can maintain a much firmer grip on how automated systems interact with external software, databases, and networks.

Furthermore, Nadella called for robust transparency measures, advocating for every meaningful action taken by a model to be thoroughly documented with tamper-proof, human-readable evidence. This standard would ensure that automated decisions can be audited effectively after the fact, providing a clear trail of accountability for enterprise deployments and consumer-facing applications alike.
Crucially, the Microsoft chief executive emphasized the necessity of operational intervention mechanisms. He argued that systems should be engineered so that an authorized person always retains the definitive ability to pause or shut down a model mid-task, functioning much like an emergency brake in industrial machinery. Underpinning this philosophy is a fundamental assumption of vulnerability: developers must operate from the premise that any given model may already be compromised, necessitating strict containment protocols right from the start of its deployment cycle.
Nadella’s public intervention arrives at a sensitive juncture for the artificial intelligence industry. Leading technology firms and research laboratories have increasingly acknowledged troubling incidents where developers appeared to lose reliable control over their autonomous models. These admissions have sparked intense internal and public debates regarding the pace of deployment, safety evaluations, and the adequacy of existing guardrails.
The discourse surrounding AI containment has gathered significant momentum in recent weeks. Notably, Anthropic CEO Dario Amodei published a comprehensive plan outlining strategies to pace the development of frontier models more cautiously. These industry-wide reflections underscore a broader realization that standard evaluation techniques may no longer suffice as models achieve unprecedented levels of autonomy and self-directed execution capabilities.
As artificial intelligence companies grapple with these complex governance challenges—ranging from restricting internal evaluations from the live internet to prevent unpredictable behaviors, to establishing binding and non-binding safety pacts—executives like Nadella are pressing for standardized structural reforms. Whether these proposals for externalized safeguards, tamper-proof audit trails, and mandatory emergency intervention mechanisms will be widely adopted across the tech sector remains to be seen as the industry navigates the path toward more advanced artificial intelligence systems.
Leave a Reply