
Federal Bureau of Investigation agents have arrested a prominent executive at a Canadian cybersecurity firm in connection with an escalating international investigation into the notorious ShinyHunters hacking collective. The arrest follows a high-profile cyber intrusion in which the threat actor group successfully compromised sensitive personnel data belonging to thousands of federal agents.
According to multiple sources familiar with the matter, the suspect was taken into custody in Pennsylvania while attending a prominent cyber insurance conference. The arrest marks a significant escalation in a sweeping multi-jurisdictional crackdown targeting not only the core members of the ShinyHunters organization, but also individuals and entities suspected of facilitating, advising, or operating adjacent to cyber extortion schemes.
The New York Times reported that federal authorities arrested a Canadian man in Pennsylvania on suspicion of assisting the hacking group. Neither the initial Times report nor a public statement published on social media platform X by FBI Director Kash Patel identified the individual by name. However, sources close to the unfolding investigation revealed that the Canadian national was visiting Pennsylvania to participate in the annual Cyber Risk Summit, held at the Loews Philadelphia Hotel.
According to online event directories and conference materials, the summit featured numerous sponsors, with the largest sponsor being a Canadian security firm known as Cypfer. Public professional profiles and industry connections tied the arrested individual to another participating Canadian security firm and conference sponsor, CyberSteward.

Federal court records subsequently confirmed that an individual named Edward Dobrovsky—with a slight spelling variation in the surname—was arrested in Pennsylvania on October 8. The defendant faces serious federal charges, including conspiracy to threaten to impair the confidentiality of information with the intent to extort money, and interference with commerce by threats.
While several core documents, including the primary criminal complaint, have been sealed by the court, a handful of filings were indexed on public legal databases such as CourtListener. These records outline the formal charges brought against the defendant and indicate that the legal proceedings were swiftly transferred to the Eastern District of Texas. Sources indicate that the FBI’s field office in Texas has become the centralized command center and epicenter for the comprehensive nationwide investigation into the ShinyHunters enterprise.
The inmate locator maintained by the U.S. Bureau of Prisons lists a 54-year-old Edward Dubrovsky as currently being held at a federal detention facility in Philadelphia, pending further legal proceedings. Court records show that the defendant has not yet retained private legal representation or been formally assigned a public defender by the court.
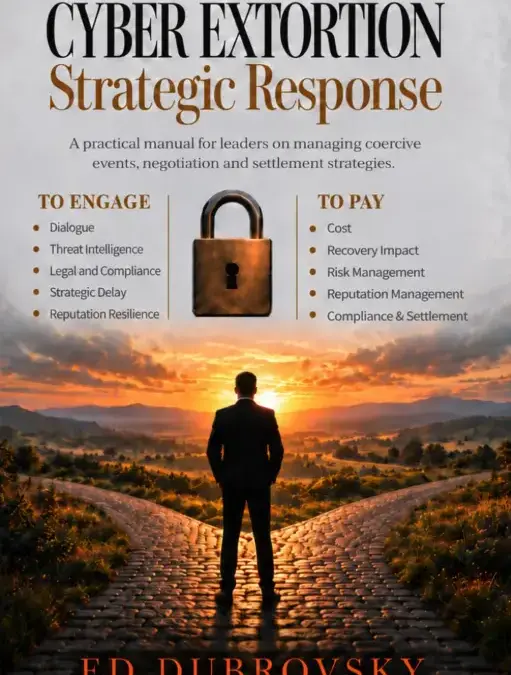
The arrested executive is a recognized figure in the specialized niche of ransomware and cyber extortion response. Publicly available professional profiles describe him as an author of a comprehensive book focusing on the intricacies of cyber extortion, strategic response frameworks, and crisis management. The publication purports to guide organizations through ransom negotiations, emphasizing the critical operational distinction between communicating with malicious actors and committing to extortion payments.
Representatives and corporate spokespersons for the firms previously and currently associated with the defendant have navigated inquiries regarding his corporate affiliations. A spokesperson for Cypfer clarified that the defendant was never a founder or co-founder of the firm as his professional networking profile previously claimed, but rather served as a managing director prior to his resignation in November 2025. Attempts to reach the defendant and other executives at his current firm for comment were unsuccessful at the time of publication.

The ShinyHunters syndicate has established a reputation within the cybersecurity landscape for executing sophisticated phishing campaigns and leveraging stolen corporate credentials to siphon proprietary data from Software-as-a-Service providers and enterprise networks. Once inside, the group typically threatens to publicly leak or sell the exfiltrated data unless substantial cryptocurrency ransoms are paid. Federal law enforcement estimates indicate that the cybercrime collective has successfully extorted more than $70 million from corporate and institutional victims over the course of the year.
The widening federal probe builds upon a series of international law enforcement actions executed over recent weeks. According to insider sources, federal investigators have spent weeks meticulously analyzing digital devices and infrastructure seized last month when Dutch police apprehended reformed cybercriminal and operative Pepijn van der Stap in connection with the ShinyHunters case. Law enforcement insiders suggest that additional criminal charges against principals and associates at other firms specializing in ransomware negotiation and incident response may be forthcoming as the investigation broadens.
The urgency of the federal investigation was amplified following the arrest of Van der Stap, after which another prominent member of the ShinyHunters organization operating under the alias "Rey" assumed operational control of the group. In an audacious display of defiance, the faction began publicly taunting federal authorities over a major breach involving the theft of sensitive internal data from the FBI’s online recruitment portal. The compromised records reportedly included detailed personnel information, including unit assignments, professional specializations, and confidential medical and psychiatric documentation.
Investigative reports later identified "Rey" as a teenager named Saif Al-din Khader. Law enforcement authorities detained Khader, who has since begun cooperating with federal investigators. The apprehension occurred as the cybercrime unit allegedly attempted to orchestrate an extortion campaign against a digital aviation and navigation unit that had been divested by aerospace giant Boeing in late 2025.
As federal authorities continue to execute search warrants, analyze seized digital evidence, and pursue co-conspirators across international borders, the investigation remains exceptionally active. Law enforcement agencies and legal representatives have declined to provide further public comments as the case develops within the federal judicial system.
Leave a Reply