Federal Bureau of Investigation agents have arrested a high-ranking executive from a Canadian cybersecurity firm in Pennsylvania, marking a dramatic escalation in the ongoing, high-stakes federal investigation into the notorious "ShinyHunters" cybercrime syndicate. The arrest comes on the heels of a massive security breach in which the hacking group successfully compromised the FBI, making off with sensitive personnel data belonging to thousands of federal agents.
According to multiple sources close to the investigation, the detained Canadian executive was visiting Pennsylvania to attend a prominent cyber insurance and risk management conference when federal authorities moved in. The suspect’s professional background is deeply rooted in the specialized sector of handling ransomware negotiations, corporate crisis management, and cyber extortion advisory services on a global scale.
The unfolding federal case gained public attention after The New York Times reported that the FBI had apprehended a Canadian man in Pennsylvania on suspicion of providing material assistance or otherwise aiding the ShinyHunters collective. While neither the initial Times report nor a public statement shared on social media platform X by FBI Director Kash Patel explicitly named the individual, subsequent legal filings and investigative reporting tied the arrest to prominent figures within the Canadian cybersecurity landscape.
Court records filed in federal court show that an individual named Edward Dobrovsky—with a slight spelling variation in the surname—was taken into custody on October 8, facing serious federal charges that include conspiracy to threaten to impair the confidentiality of information with the intent to extort money, alongside charges of interference with commerce by threats. While the core criminal complaint and several key supporting documents have been placed under seal by the court, a handful of docket items indexed on public legal tracking platforms have shed light on the initial charges.

Online public records from the U.S. Bureau of Prisons indicate that a 54-year-old named Edward Dubrovsky was initially held at a federal detention facility located in Philadelphia. However, court filings show that the case was formally ordered to be transferred to the U.S. District Court for the Eastern District of Texas. Multiple sources indicate that the Eastern District of Texas has effectively become the centralized epicenter and command post for the sprawling, multi-jurisdictional FBI investigation into the ShinyHunters operation. The FBI has consistently declined to comment on the specifics of the ongoing investigation.
The timing of the arrest aligns closely with the dates of the Cyber Risk Summit, which was held at the Loews Philadelphia Hotel. Conference schedules and promotional materials indicate that the event was heavily sponsored by several industry organizations, with the largest sponsor being a Canadian cybersecurity firm known as Cypfer. Public professional networking profiles indicate that Dubrovsky had previously been associated with Cypfer, where his LinkedIn profile claimed he was an ex-founder and managing director. However, following public inquiries, a spokesperson for Cypfer clarified that Dubrovsky was never a founder or co-founder of the firm, but rather served as a managing director until his resignation in December 2025.
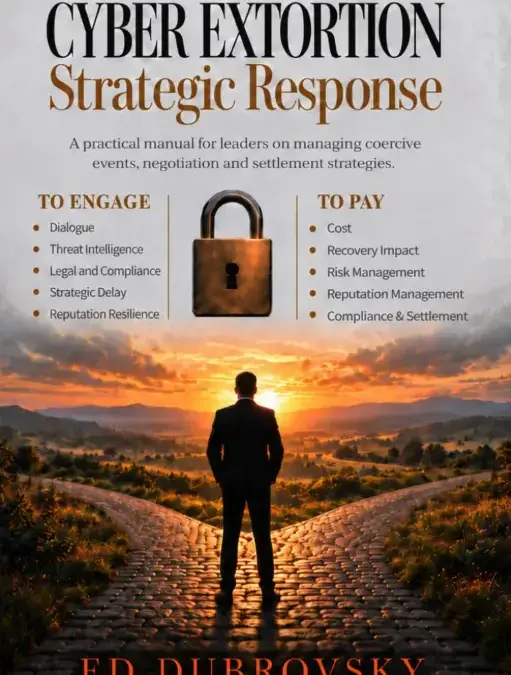
At the time of his arrest, Dubrovsky was associated with another Canadian security firm and conference sponsor, CyberSteward. Approximately a month prior to the summit, Dubrovsky had shared posts on professional networks indicating his intention to travel to Pennsylvania to attend the risk summit alongside colleagues from the CyberSteward team. In his professional communications, Dubrovsky frequently emphasized his work in strategic crisis response, regulatory-compliant advisory services, and global ransomware negotiations. He is also the author of a comprehensive book examining the tactical intricacies of ransomware negotiations and corporate incident response.
Available federal court records show that Dubrovsky has not yet retained private legal counsel, nor has a public defender been formally appointed by the court at this early stage of the proceedings. Representatives for CyberSteward could not be immediately reached for comment regarding the arrest of their associate.
The federal crackdown on individuals allegedly linked to ShinyHunters represents a major counter-offensive by law enforcement agencies against one of the most prolific and damaging cyber extortion groups operating today. According to federal estimates, the ShinyHunters syndicate has successfully extorted more than $70 million from corporate and institutional victims over the course of the year alone. The group typically relies on sophisticated phishing campaigns and stolen credentials to siphon massive volumes of proprietary data from software-as-a-service providers and enterprise accounts, subsequently threatening public data leaks unless heavy extortion demands are met.

Investigators have been rapidly expanding their operational scope following a series of international law enforcement actions. Last month, Dutch police apprehended a reformed cybercriminal named Pepijn van der Stap in connection with the broader ShinyHunters probe. Sources indicate that federal investigators have spent weeks meticulously analyzing digital devices and hardware seized during the Dutch law enforcement raid. Legal experts suggest that these forensic discoveries could pave the way for additional criminal charges against principals and associates at other firms operating within the ransom negotiation sector.
The pressure on federal investigators intensified dramatically in the wake of Van der Stap’s arrest. A leading figure within the ShinyHunters network operating under the alias "Rey" assumed operational control of the collective and launched a series of aggressive public taunts directed squarely at the FBI. The taunts stemmed from a brazen cyberattack in which the group infiltrated the FBI’s online recruitment portal, extracting highly sensitive personal records detailing agents’ specific operational units, specialized skill sets, and confidential medical and psychiatric histories.
The standoff shifted rapidly last week when international reporting revealed that the individual operating under the alias Rey had been identified as a teenager named Saif Al-din Khader. Authorities detained Khader, who has reportedly begun cooperating with federal investigators. Previous investigative findings detailed how Khader was tracked down and apprehended as the cybercrime group attempted to execute an extortion scheme against a digital aviation and navigation unit that had recently been spun off from Boeing.
As federal authorities continue to parse through seized digital evidence and untangle the complex network of individuals interacting with international cyber extortionists, legal proceedings in Texas and Pennsylvania are expected to move swiftly.