
A 26-year-old Canadian man widely regarded as one of the most consequential cybercrime threat actors of 2024 has officially pleaded guilty to computer fraud and conspiracy charges. The admissions stem from his role in a massive, coordinated hacking and extortion campaign targeting more than 165 organizations that relied on the cloud data platform Snowflake, as well as the theft of sensitive call and text history records belonging to over 100 million AT&T customers.
Connor Riley Moucka, a resident of Kitchener, Ontario, entered his guilty pleas in a federal court proceeding, admitting to a sweeping digital conspiracy that shook corporate America and exposed terabytes of proprietary and personal data. According to the U.S. Justice Department, Moucka and his co-conspirators operated between February and October 2024, leveraging stolen login credentials to infiltrate cloud-hosted data repositories managed by a major U.S.-based software-as-a-service provider.
The cybercriminal network primarily targeted Snowflake customer accounts that failed to enforce multi-factor authentication (MFA). By exploiting these security blind spots, the hackers were able to access and exfiltrate sensitive databases from a host of prominent, well-known enterprises, including Ticketmaster, LendingTree, Advance Auto Parts, and Neiman Marcus. The breach prompted Snowflake to significantly overhaul its platform security by increasing password complexity requirements and making multi-factor authentication mandatory for its users.
Throughout his cybercriminal career, Moucka frequently adopted new monikers and occasionally operated multiple online identities concurrently. However, two of his most widely known aliases within underground forums and chat rooms were “Judische” and “Waifu.” Moucka’s true identity and his prominent role in the Snowflake data thefts were first brought to light in September 2024 through investigative reporting by KrebsOnSecurity, which uncovered a dark nexus linking Western, English-speaking cybercriminals to extremist online groups that specialize in harassing and extorting minors into causing harm to themselves or others.
That initial September report identified “Judische” as an Ontario-based software engineer who had actively participated in numerous high-profile data breaches and sophisticated voice phishing attacks directed against U.S. companies since at least 2020. Just over a month after those findings were published, Canadian law enforcement authorities apprehended Moucka, acting on a provisional arrest warrant issued by the United States.
Federal prosecutors detailed the staggering scope of the stolen information, noting that Moucka and his accomplices utilized unauthorized access to steal billions of sensitive customer records and download massive tranches of proprietary data. The stolen files included non-content call and text history records, banking and financial information, corporate payroll records, Drug Enforcement Administration (DEA) registration numbers, driver’s license numbers, passport numbers, Social Security numbers, and a wide array of other personally identifiable information. Once the data was secured, the conspirators attempted to extort their corporate victims by threatening to leak or publish the stolen information online.
The gravity of Moucka’s actions extended beyond corporate extortion. Federal authorities revealed that he also engaged in the direct harassment and intimidation of government officials and independent security researchers who were actively working to track down his digital footprint. According to the Justice Department, the criminal conspiracy successfully extracted more than $2.5 million in ransom payments from panicked victims. In at least one particularly brazen instance, Moucka resorted to re-extorting a victim by threatening the further disclosure of sensitive information after an initial ransom had already been paid.
“Moucka used the stolen data of a government officer and members of a then-former government officer’s immediate family in this re-extortion attempt,” the Justice Department stated, highlighting the aggressive tactics employed by the threat actor to silence opposition and secure financial payouts.
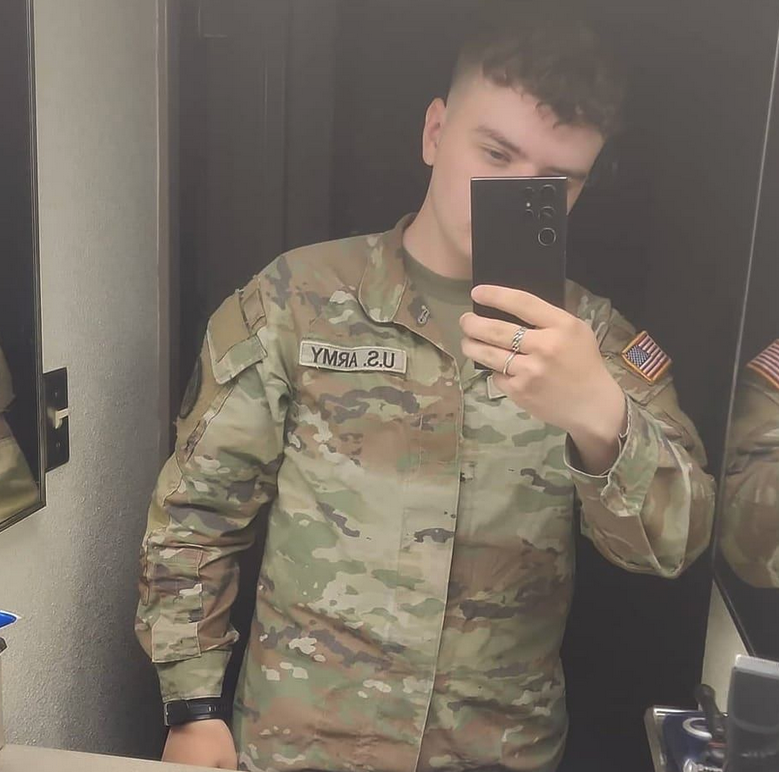
As federal investigators unraveled the conspiracy, they identified several key co-conspirators working alongside Moucka. One of these individuals is Cameron “Kiberphant0m” Wagenius, a U.S. Army soldier who pleaded guilty in July 2025 to charges related to the extortion of telecommunications giants AT&T and Verizon for their customer account data. Investigative reporting published shortly before Wagenius’s arrest had exposed his various Telegram and Discord personas, revealing that the individual operating the accounts frequently boasted to online associates about being an active-duty soldier stationed in South Korea.
Wagenius mirrored Moucka’s aggressive re-extortion tactics. Immediately following Moucka’s high-profile arrest, Wagenius posted files on hacker forums claiming to contain the AT&T call logs of then President-elect Donald Trump and then Vice President Kamala Harris, alongside technical schematics allegedly stolen from the U.S. National Security Agency (NSA). Wagenius is scheduled to be sentenced on September 3, 2026. The government has noted that he faces a maximum penalty of 20 years in prison for conspiracy to commit wire fraud, a maximum penalty of five years for extortion linked to computer fraud, and a mandatory consecutive two-year sentence for aggravated identity theft.
A third alleged co-conspirator in the broader criminal network is John Erin Binns, a 26-year-old American citizen who fled the United States after being indicted for his admitted role in a massive 2021 cyberattack against T-Mobile that compromised the personal data of at least 76 million customers. Sources close to the investigation reported that Binns, who has operated under online handles such as “IRDev” and “IntelSecrets,” was recently incarcerated in a Turkish prison before being released to resurface in the digital underground. According to those same sources, Binns acquired Turkish citizenship during or following his detention, complicating any potential extradition efforts, as Turkish law generally prohibits the extradition of its citizens to foreign jurisdictions.
Moucka’s guilty plea encompasses four distinct criminal counts, including computer fraud, wire fraud, aggravated identity theft, and conspiracy. He is scheduled to face sentencing on October 27. Under federal sentencing guidelines, he faces a mandatory minimum penalty of two years in prison specifically for the aggravated identity theft charge, coupled with a maximum potential sentence of up to 30 years in prison for the remaining counts. Ultimately, the exact length of the prison term Moucka will serve for his extensive cybercriminal enterprise will be determined by a federal judge.
Leave a Reply