Authorities in the Netherlands have arrested a 24-year-old convicted cybercriminal on suspicion of aiding in sophisticated data thefts and high-stakes extortions carried out by the prolific international hacking collective known as ShinyHunters. The detention of the suspect has triggered immediate shockwaves across the global cybercrime underground, prompting remaining members of the group to dramatically escalate their attacks. In the chaotic days following the arrest, the syndicate launched brazen operations, stealing highly sensitive data from the Federal Bureau of Investigation (FBI) and turning its sights toward extorting the notorious Russian ransomware group Cl0p.
According to three independent sources familiar with the matter, the Dutch man taken into custody by authorities this month is Pepijn van der Stap, a previously convicted cybercriminal residing in Almere and Lelystad in the Netherlands. Van der Stap had earlier faced prosecution and was convicted in 2023 for his involvement in a sweeping series of corporate data thefts and corporate extortions. Prosecutors at the time estimated that those illicit activities had generated between €1.5 million and €2.7 million in criminal proceeds.
During his trial in late 2023, van der Stap offered a candid admission of his dual existence, describing a lifestyle that mirrored a digital Dr. Jekyll and Mr. Hyde. By night, he secretly operated under the hacker handle “Umbreon,” leveraging the alias to extort corporate victims and publish stolen data troves on English-language cybercrime forums, including the now-defunct RaidForums and Breached. By day, however, van der Stap maintained a respectable professional profile, working as a software engineer at Hadrian, an Amsterdam-based cybersecurity startup, while simultaneously volunteering his time with the Dutch Institute for Vulnerability Disclosure (DIVD), a nonprofit security research organization dedicated to identifying and mitigating software vulnerabilities.
Van der Stap fully confessed to his role in the data thefts and extortion schemes, ultimately receiving a four-year prison sentence, of which one year was suspended. During the legal proceedings, van der Stap chose to remain in custody rather than return home under house arrest, arguing that he could not find adequate medical and psychological support outside of correctional facilities for his ongoing mental health struggles, which included post-traumatic stress disorder linked to childhood trauma. He was subsequently released from prison in December 2025.
In an interview with KrebsOnSecurity on September 9, 2026, van der Stap presented himself as a genuinely reformed individual who was actively attempting to rebuild his life and make a positive, constructive contribution to society. At the time of the interview, he was employed as an offensive security lead at Neo Security, a Dutch cybersecurity firm that ultimately did not respond to multiple requests for comment.
During the discussion, van der Stap noted that he was still navigating complex civil lawsuits and financial restitution obligations stemming from his past cybercrime activities, emphasizing that he was doing his utmost to make amends to those affected. However, shortly after that interview concluded, van der Stap abruptly stopped responding to electronic communications. Attempts by close associates and colleagues to reach him repeatedly failed over a span of two weeks.
According to two sources with direct knowledge of the investigation, van der Stap was arrested by Dutch law enforcement officers on or around September 16 and has remained in custody for intensive questioning ever since. One source reported that a colleague personally witnessed Dutch authorities removing boxes and technical equipment from van der Stap’s residence during the raid.
For months, Dutch law enforcement agencies have been actively probing the inner workings of ShinyHunters, publicly appealing to citizens for assistance in identifying a voice recorded during a telephone call in February 2026. In that call, a native Dutch-speaking member of the hacking collective successfully social-engineered their way into Odido, the largest mobile telecommunications provider in the Netherlands. During the intrusion, the operatives tricked an Odido employee into authenticating their credentials on a spoofed phishing website, subsequently utilizing that unauthorized access to harvest personal data belonging to more than 6.2 million Dutch citizens.

When approached by local media outlets, representatives for ShinyHunters confirmed that the individual heard in the released audio clip was indeed a core member of the hacker collective. In a public statement shared with the NL Times, the group adopted a defiant posture regarding the investigation.
“Our team member has our full support — emotionally, mentally, and financially,” the hackers stated. “Everything has been arranged, including a criminal defense lawyer. We do not look down on our staff and members; we take excellent care of them.”
The collective also launched verbal attacks against law enforcement in the region. “The Dutch police will need all the luck in the world — and everyone’s prayers — if they want to catch him before we carry out another large-scale data theft in the Netherlands,” the statement continued, dismissing the agency’s capabilities. It remains unconfirmed whether Dutch police have successfully matched the voice from the Odido intrusion to a definitive real-world identity, as the police unit managing the Odido investigation declined to comment on the ongoing proceedings.
FBI, CL0P HACKS
Just days after sources indicated van der Stap had been detained, ShinyHunters claimed responsibility for an extraordinarily bold and high-profile breach targeting the FBI’s job application portal at apply.fbijobs.gov. Reporting from 404 Media revealed that the data compromised during the incident included Social Security numbers and detailed personal information concerning more than 5,000 bureau officials and applicants.
Further analysis by 404 Media and Reuters established that the stolen FBI records contained specific job titles and operational team assignments, including personnel working in special agent roles, threat intake examination, major cybercrimes units, and divisions dedicated to investigating cyber threats originating from foreign state-backed actors. Reuters journalists who examined document samples provided by the hacking group noted that the files also contained sensitive psychiatric and medical records belonging to FBI personnel. In response to the breach, the FBI issued a brief official statement acknowledging the unauthorized compromise of the job portal.
According to ShinyHunters, access to the FBI portal and numerous other corporate systems was achieved by exploiting a recently patched zero-day vulnerability, cataloged as CVE-2026-35273, affecting PeopleSoft. PeopleSoft is a widely deployed software-as-a-service platform developed by technology giant Oracle, used extensively by major enterprises and government bodies for human resources, recruitment, benefits administration, and payroll management. Oracle swiftly rolled out a security patch after discovering that ShinyHunters had begun actively exploiting the vulnerability in June. Around the same time, Mandiant published web application firewall rules designed to assist organizations that could not immediately apply the software updates.
However, security researchers reported that ShinyHunters managed to circumvent these protective measures. BleepingComputer revealed that the hackers utilized a URL-encoding trick to bypass the mitigation rules recommended by Mandiant. In a joint threat intelligence report published on September 25, specialists from Mandiant and the Google Threat Intelligence Group confirmed that the group had engaged in a mass-exploitation campaign targeting the PeopleSoft vulnerability, successfully extracting data from dozens of organizations spanning diverse sectors, including higher education, technology, healthcare, agriculture, transportation, and government.
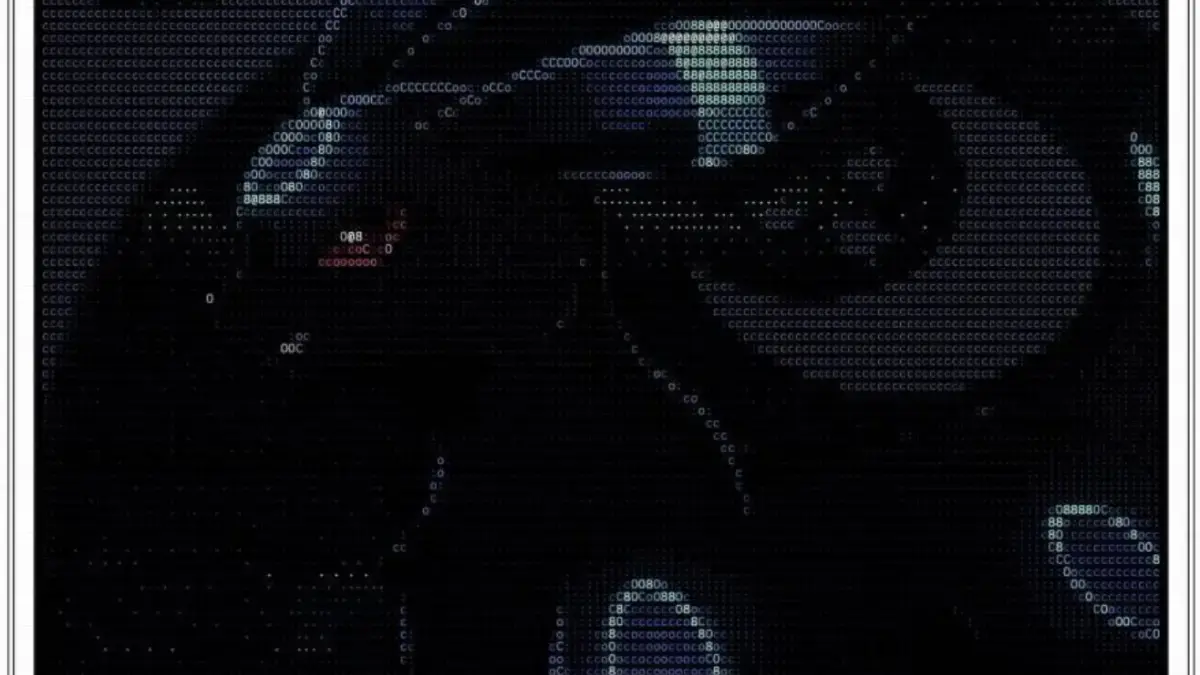
Intriguingly, van der Stap’s former hacker alias, Umbreon, appeared to be hidden in plain sight across the digital imagery utilized by ShinyHunters to publicize the FBI breach. The defacement screen left behind by the hackers on the compromised job portal featured an ASCII art design depicting the Pokémon character Umbreon. The accompanying text banner read, “This site has been seized by ShinyHunters. rooting your systems since ’19 ;).” This visual composition closely mirrored a defacement template previously employed by ShinyHunters during their 2020 infiltration of Hackforums, an English-language cybercrime community.

Sources close to the investigation into ShinyHunters noted that the group’s increasingly aggressive actions against heavily fortified targets like the FBI and prominent ransomware syndicates represent a significant departure from its historical operational style. Investigators attribute this sudden strategic pivot to a leadership transition within the collective, following a takeover by a teenage cybercriminal from Amman, Jordan, who operates under the online moniker "Rey." Rey is reportedly a prominent figure within a specialized cybercrime syndicate known as ScatteredLapsussHunters (SLSH)—an amalgamation of three distinct hacking factions: Scattered Spider, LAPSUS$, and ShinyHunters.
According to informants, Rey had maintained a longstanding interpersonal conflict with the Dutch hacker concerning operational control over the ShinyHunters brand and its vast data repositories. Consequently, cybersecurity analysts suspect that the prominent inclusion of the Umbreon Pokémon imagery in the FBI site defacement was a deliberate attempt by Rey to frame van der Stap for the attack.
Rey was first unmasked publicly by the cybersecurity firm KELA in March 2025. Ahead of a subsequent profile published by KrebsOnSecurity in November 2025, researchers contacted Rey’s father to request an interview with the teenager. The father forwarded the communication directly to his son, who subsequently acknowledged participating in various ransomware operations while expressing a desire to disengage from the SLSH collective.
BLAMING UMBREON
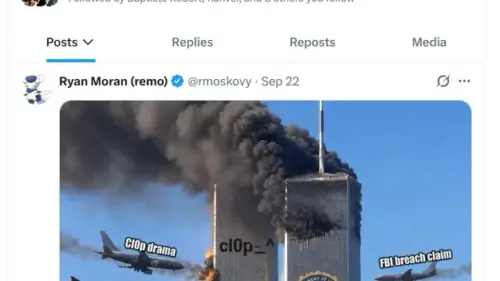
Immediately following widespread media coverage of the FBI job portal hack, the primary social media account associated with Rey on X (formerly Twitter) began taunting both the FBI and the Cl0p ransomware syndicate. One widely circulated post featured a crude graphic depicting the World Trade Center towers being struck by aircraft labeled with references to the Cl0p drama and the FBI breach claim, with a massive digital float of the Pokémon character Umbreon looming in the foreground.
On September 24, security researchers once again reached out to Rey’s family to request an interview regarding his apparent ascension to leadership within ShinyHunters. Just hours after that outreach, Rey’s long-standing social media account was permanently deleted. Meanwhile, Rey’s father, an employee of Royal Jordanian Airlines, has failed to respond to multiple inquiries regarding his son’s alleged criminal activities.
The underlying friction between the SLSH faction and core members of ShinyHunters stems from a brief, uneasy partnership formed earlier in the year. According to reporting published by Wired, the groups temporarily joined forces to better monetize valuable credentials gathered by TeamPCP, an upstart gang that successfully compromised global code supply chains using malicious software but struggled to convert stolen information into financial gain. (Two alleged leaders of TeamPCP were arrested in Australia, with reports indicating the group generated a mere $20,000 from their enterprise).
Investigative findings revealed that Mandiant had covertly infiltrated TeamPCP’s infrastructure and was quietly neutralizing the stolen credentials by immediately funneling them to major cloud providers such as Amazon and Microsoft, which quickly invalidated the compromised keys. As the operation unraveled, the cooperating hacker factions began pointing fingers and blaming one another for the rapid devaluation of the stolen data.
Wired journalist Andy Greenberg reported that shortly after the partnership dissolved, ShinyHunters went rogue, executing independent extortion attempts using the shared TeamPCP credentials while cutting out their former collaborators entirely. Despite these internal fractures, Mandiant researcher Austin Larsen noted that ShinyHunters has maintained a highly lucrative extortion campaign throughout the year, putting the collective on track to amass nearly $100 million in extortion payouts by the end of 2026.

Conversely, associates of van der Stap have maintained that his historical hacking activities were rarely driven by financial profit. In previous interviews, including discussions with Bloomberg reporters in 2024, van der Stap explained that his primary motivation was an obsessive compulsion to curate the world’s most comprehensive repository of stolen databases.
“The hacking was very easy for me, and it wasn’t a compulsion,” van der Stap told Bloomberg during the 2024 interview. “My habit was collecting. Collecting data, organizing data, downloading data, creating folders.”
Meanwhile, the Dutch Institute for Vulnerability Disclosure (DIVD), where van der Stap had previously served as a volunteer researcher, announced via LinkedIn that the organization was managing an internal cybersecurity incident involving the suspected malicious application of artificial intelligence. While DIVD has released limited details regarding the event, a spokesperson confirmed to KrebsOnSecurity that the incident does not appear to be linked to ShinyHunters, nor is there any indication that the matter involves the past contributions of any former volunteer.
Dutch law enforcement officials officially confirmed the arrest of a 24-year-old suspect in connection with the ongoing ShinyHunters investigation. In a public statement shared on social media, the Dutch police announced that the detained individual is scheduled to appear before the chambers of the Rotterdam District Court, with additional details expected to be released as the legal proceedings unfold.
Further compounding the gravity of the case, Dutch news outlet RTL reported that investigators are examining suspicions that van der Stap may have attempted to orchestrate at least two murders. According to the report, the alleged plots were intended to be executed abroad, and investigators are reviewing indications that the suspect issued direct orders for the killings.
Providing an international perspective on the dismantling of the cybercrime infrastructure, the FBI released a video statement featuring Brett Leatherman, assistant director of the bureau’s cyber division. Leatherman expressed gratitude to Dutch law enforcement partners for their critical assistance and issued a direct warning to the remaining members of ShinyHunters.
“Arrests have a way of changing who is willing to talk, and seized infrastructure has a way of showing us who’s left,” Leatherman stated. “The longer you stay in this, the more we learn about you. You know how to find us, and we know how to find you. I suggest you reach out to us while the choice is still yours.”