The timeline for a cryptographically relevant quantum computer is shrinking faster than many industries anticipated, forcing a hurried global reckoning over digital security. In September, quantum computing pioneer IonQ published a comprehensive blueprint detailing how a fault-tolerant quantum machine could break the cryptographic foundations of Bitcoin, Ethereum, and a vast array of secure corporate and government communications.
According to IonQ’s researchers, a quantum computer equipped with just 20,000 physical qubits running Shor’s algorithm could recover a 256-bit elliptic curve key in less than 26 days. Devised in 1994 by MIT mathematician Peter Shor, the eponymous algorithm solves factoring and discrete logarithm problems that underpin the public-key cryptography protecting modern digital infrastructure. While classical computers would require billions of years to solve the underlying mathematics, and previous estimates suggested a quantum attack would demand upwards of one million physical qubits, the latest research demonstrates that the threshold is drastically lower.
Even more striking is IonQ’s public roadmap. The company is scheduled to manufacture a fault-tolerant system featuring 10,000 physical qubits in 2027, followed by a 20,000-physical-qubit system in 2028. Given this hardware trajectory, the prospect of a quantum computer capable of breaking blockchain cryptography in just a few years has sparked legitimate concern across financial markets, cybersecurity firms, and government agencies.
Despite the potentially alarming implications for blockchain security, IonQ leadership emphasizes that the study was designed as an objective technical benchmark rather than an aggressive exploit.
“The important point I want to make when we’re talking about this is to not come across as threatening—we’re not trying to attack cryptography,” Chris Ballance, IonQ president, told EE Times. “Cryptography is black and white—you can either solve or not solve the problem—and we can use this as a benchmark metric for our quantum computers.”
Ballance noted that the clarity of this benchmark makes it exceptionally valuable for evaluating performance in an emerging technology sector. Measuring whether a compiler stack is operating efficiently or whether quantum algorithms are properly optimized yields a definitive, black-and-white answer, which is rare in early-stage computing fields.

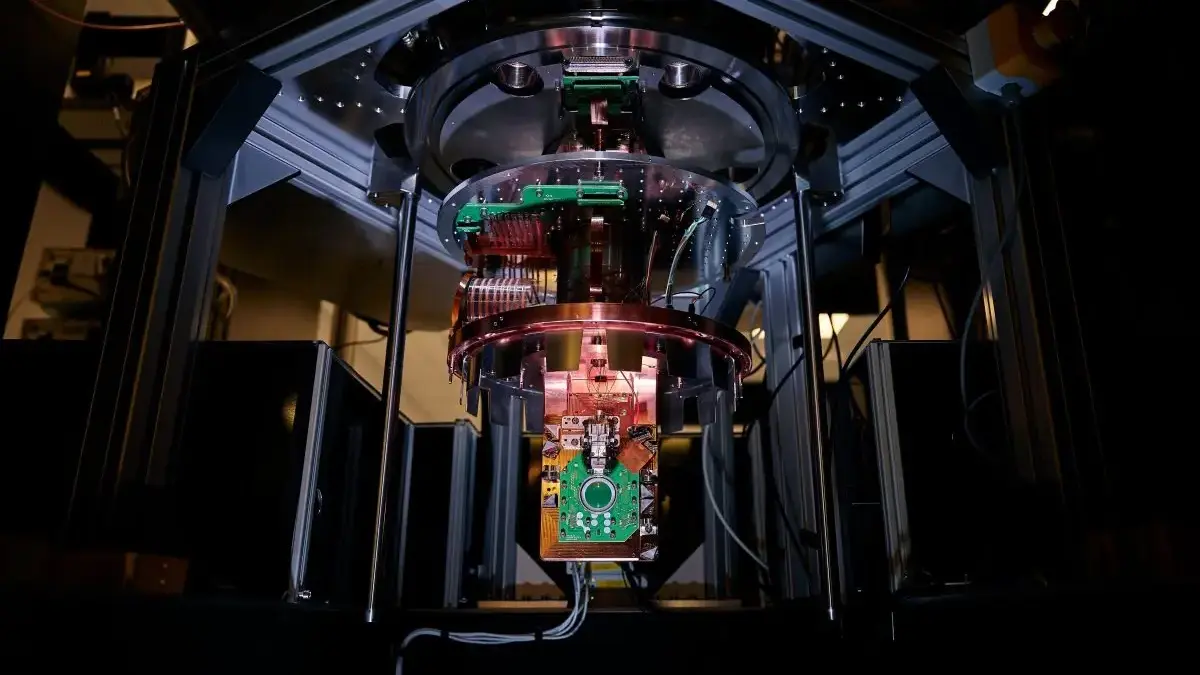
The benchmark metric was formally published under the title “Computing 256-bit elliptic curve discrete logarithms in 26 days on a fault-tolerant trapped-ion quantum computer with 20,000 qubits.” The 70-page paper outlined an end-to-end route to break secp256k1—the specific elliptic curve safeguarding Bitcoin and Ethereum—using a trapped-ion quantum architecture based on IonQ’s error-correcting “Walking Cat” approach. Trapped ions serve as IonQ’s primary qubit modality, where ions are shuttled across a grid and utilized alongside Schrödinger-style superpositions, known as cat states, to detect and correct the quantum errors that typically accumulate and destroy calculations.
By optimizing the algorithm, compiler, hardware, and error-correction layers in tandem, IonQ successfully reduced the overall resource requirements needed to break 256-bit elliptic-curve cryptography. Key optimizations included the recycling of temporary helper qubits during active calculations and the reuse of entangled cat-state resources to minimize the total qubit count.
“We have every single layer of the stack developed… and we compiled every operation down to the actual error-correction primitives our architecture runs,” Ballance said. “We haven’t just done mathematical proofs… we have put everything together all the way down to the individual instructions you can run on a quantum computer.”
Ballance believes the publication of these findings coincides with a pivotal shift in the industry. As developers transition from theoretical daydreaming to tangible engineering designs, companies are actively building and integrating the necessary hardware pieces. By demonstrating how individual elements interact and highlighting the architectural tradeoffs involved, IonQ aims to establish a clear standard for what a viable solution looks like.
From Lasers to Electronics
Historically, trapped-ion quantum computing systems relied heavily on complex, free-space laser setups to manipulate individual qubits, which presented a significant bottleneck for scaling qubit counts. However, IonQ took a major step toward overcoming this limitation in September 2025 by acquiring Oxford Ionics, an electronic qubit control (EQC) pioneer co-founded by Ballance and fellow Oxford University researcher Tom Harty.
By replacing cumbersome optical setups with integrated electronics built directly on silicon chips, the firm rapidly demonstrated prototypes achieving remarkably low error rates, yielding in excess of 99.99% two-qubit gate fidelity. By comparison, Google Quantum AI has previously reported close to 99.88% two-qubit gate fidelity using superconducting qubits.

Niccolo de Masi, chairman and CEO of IonQ, noted that achieving this level of quantum performance has served as the industry’s north star for decades. Ballance added that exceeding the 99.99% threshold on chips manufactured in standard semiconductor facilities establishes a clear, scalable path toward millions of qubits while unlocking advanced commercial applications much sooner than previously expected.
To secure its supply chain and ensure scalable hardware fabrication, IonQ subsequently acquired U.S. silicon chip maker SkyWater Technology in July, followed by the September launch of Superion 256, its 256 physical qubit platform leveraging electronic qubit control. The company’s landmark paper detailing the blueprint to break blockchain cryptography was released on the exact same day.
“Right now, we have chips at the 10,000 [physical] qubit scale designed, and these are going into the fab for our next generation products,” Ballance said. “Large-scale quantum computing requires a highly manufacturable hardware platform you can scale without dying on complexity hill—you can’t get stuck in a science experiment, building something like the Large Hadron Collider. The Superion platform allows us to scale out these chips.”
Earlier Elliptic Breakthroughs
IonQ is not alone in demonstrating the feasibility of breaking 256-bit elliptic curve cryptography using fewer physical qubits via Shor’s algorithm. In March, Oratomic—a startup founded by researchers from Caltech, Harvard, Berkeley, Google, and Amazon—alongside Caltech researchers, published a paper outlining how a neutral-atom quantum system could crack the encryption using as few as 10,000 physical qubits within a matter of days. The researchers noted that while substantial engineering hurdles remain, their theoretical analysis indicates that an appropriately designed neutral-atom architecture can support quantum computation at cryptographically relevant scales.
Concurrently, Google Quantum AI, in collaboration with researchers from the Ethereum Foundation, the University of California Berkeley, and Stanford University, released a paper demonstrating that a superconducting quantum computer could break the same encryption in roughly nine minutes using fewer than 500,000 physical qubits. The authors strongly urged vulnerable cryptocurrency communities to initiate the migration to post-quantum cryptography without delay.
Thomas Prest, a senior cryptographic researcher at U.K.-based cybersecurity firm PQShield, shares Google’s sense of urgency. His organization specializes in post-quantum cryptography (PQC), developing cryptographic algorithms engineered to withstand quantum attacks, and collaborates extensively with governments and financial institutions transitioning to quantum-safe standards.

“Cryptocurrencies [Bitcoin and Ethereum] are very vulnerable right now as they are using digital signatures that are not quantum-resistant,” Prest said. “They are aware of this, and Ethereum at least, already has a solid plan to move to post-quantum signatures.”
Prest warns that the threat extends far beyond digital assets. “From my point of view, quantum computers represent a threat to not only cryptocurrencies but entire industries that rely on cryptography,” he added. “We’re in discussions with the defense sector and large companies that work with routers, anything that needs encryption at scale—these organizations are most concerned with quantum computing.”
While Prest views recent papers from entities like Oratomic and Google as significant milestones moving the needle toward cryptographically relevant quantum computing, he maintains that additional technical breakthroughs are required before real-world systems are actively compromised. Nevertheless, he regards these findings as an urgent reminder for organizations to accelerate their migration to post-quantum cryptography, ideally targeting a 2030 completion deadline. Because protocols, software, and hardware implementations must all be updated, the migration process requires years rather than months.
Professor Jungsang Kim, chief science and technology strategist for the Provost at Duke University and a co-founder of IonQ who served as its CTO until 2024, offers a more measured perspective. While acknowledging the rapid pace of development, Kim believes substantial engineering challenges must still be resolved before a cryptographically relevant quantum computer becomes operational.
“I’m not sure if there’s any fundamental physics or fundamental questions that are left unresolved,” Kim said. “I think this is now all about the execution—and this will still require substantial technology development and innovation to pose a real threat.”
Although Kim remains skeptical that blockchain elliptic-curve cryptography will be successfully cracked by the late 2020s, favoring a longer 2030-plus timeline, he emphasizes that the trajectory of quantum computing is notoriously difficult to forecast. Increased investment, expanded research teams, and cross-industry collaboration could potentially accelerate timelines beyond current expectations.

“I’m still quite optimistic that we won’t be able to crack these codes by the late 2020s, but [the latest results] all point to us needing to go to post-quantum cryptography as quickly as possible—you don’t want to have the slightest chance of taking that risk,” Kim noted.
The broader security community is increasingly focused on Q-Day, the hypothetical moment when quantum computers break modern public-key cryptography standards such as Elliptic Curve Cryptography. Government bodies worldwide are actively advising organizations on migration timetables to avert widespread systemic disruption.
The U.S. National Institute of Standards and Technology (NIST) released an updated post-quantum cryptography migration roadmap recommending that federal high-value and high-impact systems adopt PQC standards by the end of 2030, with a broader federal transition targeted for 2035. International guidelines vary, with the governments of Canada, Japan, and the United Kingdom setting a 2035 migration target, while the Australian government suggests 2030 or sooner. Among private enterprises, Microsoft has targeted 2033, whereas Cloudflare and Google have adopted more aggressive timelines pointing toward 2029.
Driven by these industry developments, IonQ leadership suggests that Q-Day could arrive toward the close of the decade. As Ballance observed, an organization’s timeline largely depends on its internal security posture, though many institutions are currently adjusting their target horizons toward 2028.
Additional evidence highlighting the rapid reduction in required quantum resources comes from Sydney-based Iceberg Quantum. The firm updated its early-2026 estimates indicating that its fault-tolerant quantum architecture could factor the widely used public-key cryptographic algorithm RSA-2048 using approximately 98,000 physical qubits within a month. More recent estimates from the company further reduced that requirement to 72,000 physical qubits with an expected runtime of just 3.7 days.
Although Iceberg Quantum’s findings were detailed in a blog post rather than a peer-reviewed academic paper, the projections underscore a broader trend: the resources required to compromise public-key cryptography are diminishing rapidly, steadily narrowing the window for global cybersecurity preparedness. As IonQ chairman and CEO Niccolo de Masi noted when releasing the company’s blockchain-breaking blueprint, the shifting timeline underscores an immediate risk to all systems secured by elliptic-curve cryptography.