
A teenager from Amman, Jordan, suspected of operating as a key leader of the prolific data theft and extortion syndicate known as ShinyHunters, has been detained by local authorities and is reportedly cooperating with the FBI to identify other members of the hacking collective.
According to intelligence gathered by KrebsOnSecurity, the suspect—who operates online under the hacker handle “Rey”—was taken into custody just as ShinyHunters was actively attempting to extort a business unit recently divested by global aerospace giant Boeing. In a striking twist of geographic irony, the employer of Rey’s father is Royal Jordanian Airlines, a carrier whose long-haul fleet consists entirely of aircraft manufactured by Boeing.
The detention first came to light when Reuters cited three unnamed sources confirming that a suspected ShinyHunters member in Amman, identified as Saif Al-din Khader, had been apprehended by Jordanian law enforcement and was actively assisting federal investigators. KrebsOnSecurity previously identified Rey as Khader in a detailed profile published in November 2025, during which the young man admitted to collaborating with multiple ransomware operations.
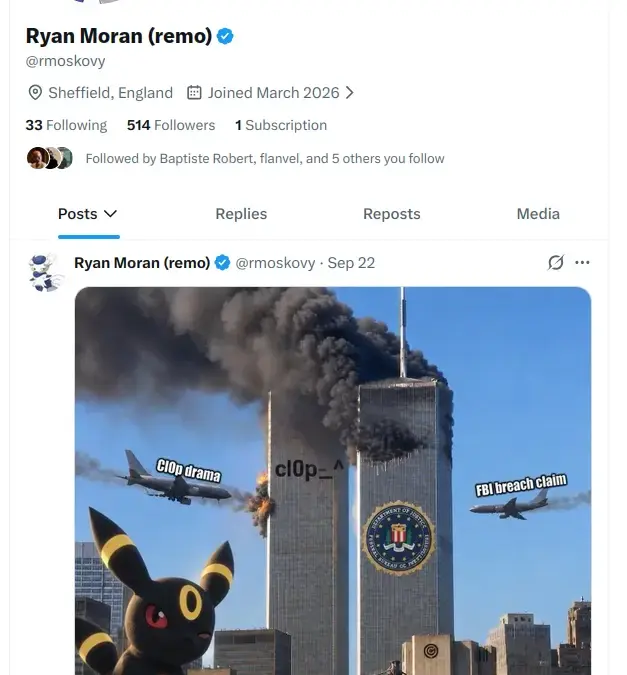
Rey’s name surfaced again in a late September exclusive detailing the arrest of 24-year-old Dutch cybercriminal Pepijn van der Stap by Netherlands police. Authorities suspect Van der Stap aided in data thefts and extortion campaigns orchestrated by ShinyHunters. According to security reports, immediately following the Dutchman’s dramatic arrest on the evening of September 15, Rey seized control of the ShinyHunters brand and publicly boasted about stealing highly sensitive data from the Federal Bureau of Investigation while attempting to extort the rival ransomware group Cl0p.
In an effort to throw investigators off his trail, Rey taunted both the FBI and Cl0p through a series of memes posted to his long-standing account on Twitter/X. He embedded images of the avatar used by Van der Stap’s former hacker alias, “Umbreon,” in a transparent bid to frame the Dutch national for the high-profile intrusions.

The security breaches orchestrated by the group relied heavily on exploiting a critical vulnerability, tracked as CVE-2026-35273, within PeopleSoft. This software-as-a-service platform, developed by Oracle, is widely deployed across corporate enterprises to manage human resources, payroll, hiring pipelines, and employee benefits. Although Oracle moved swiftly to issue a security patch after ShinyHunters began weaponizing the vulnerability as a zero-day exploit in June, and Mandiant subsequently released web application firewall rules for organizations unable to apply patches immediately, the fallout was severe.
Initial reports from BleepingComputer indicated that ShinyHunters originally targeted the FBI’s own PeopleSoft database in June, though those early attempts were reportedly unsuccessful. In subsequent weeks, however, the hackers bypassed defensive web application firewall rules implemented by Mandiant by utilizing a well-known URL-encoding trick.
A comprehensive threat intelligence report released by Mandiant and the Google Threat Intelligence Group confirmed that the syndicate mass-exploited the PeopleSoft flaw to compromise dozens of systems across critical infrastructure sectors, including higher education, technology, healthcare, agriculture, transportation, and government agencies. Subsequent media reports revealed that the security lapse forced the FBI to remove an Accenture contractor after a damaging breach exposed sensitive personal data belonging to more than 5,000 bureau personnel, including unit specializations alongside medical and psychiatric records.
“Rey” Means King, as in Royal
Sources familiar with the ongoing international investigation indicate that the FBI’s pursuit of ShinyHunters gained intense momentum following the group’s aggressive extortion attempt against the former Boeing aviation unit. The targeted entity—a navigation and digital aviation subsidiary recently divested by Boeing—was facing intense pressure from the hackers, who allegedly compromised proprietary information that investigators warn could pose significant operational safety risks.
Boeing formally acknowledged the extortion attempts in a statement, confirming that the incident involved data stolen from Jeppesen ForeFlight. Boeing had previously sold the subsidiary to private equity firm Thoma Bravo in November 2025 for $10.55 billion.

"We are aware of claims by a threat actor regarding data allegedly associated with Boeing and our former subsidiary Jeppesen ForeFlight," a Boeing spokesperson stated. "We are actively reviewing the matter with the Jeppesen ForeFlight team."
Representatives for Jeppesen ForeFlight maintained that their internal systems remained secure. In a written statement, the company noted that based on its ongoing investigation and proactive security measures, operations and products suffered no negative impact from the incident.
Rey’s alleged role in targeting the former Boeing division draws additional scrutiny given his familial ties to Royal Jordanian Airlines. The airline, primarily controlled by the Jordanian government, relies on Boeing aircraft for its international routes. While Rey claimed on Telegram in early 2025 that his father was an airline pilot, that detail could not be independently verified. However, digital forensic artifacts obtained from a password-stealing malware infection on the family’s shared computer showed that Rey’s father utilized identical login credentials across multiple online portals designated for Royal Jordanian Airlines employees.
Following outreach from security journalists seeking comment ahead of previous investigative reports, Rey abruptly began deleting his social media footprints, including the Twitter/X handle he used to mock the FBI and corporate victims. Despite the digital purge, a cybersecurity blog maintained by Rey on GitHub remained active, featuring an analytical post from March 2026 that outed two Russian nationals as the core developers and operators behind the Cl0p ransomware enterprise.
Murder-for-Hire Allegations Surface in the Netherlands
While developments unfolded in the Middle East, legal proceedings in the Netherlands revealed explosive new accusations against Van der Stap. Despite widespread media coverage portraying the young man as a reformed cybercriminal who had successfully transitioned to legitimate security work, Dutch daily newspaper RTL reported that investigators suspect Van der Stap attempted to orchestrate at least two contract murders abroad.

Van der Stap had recently completed the majority of a four-year prison sentence for data theft and extortion offenses that prosecutors estimated generated between 1.5 million and 2.7 million euros. Prior to his September arrest, he secured employment as an "offensive security lead" at Amsterdam-based Neo Security, where he claimed his responsibilities included testing client networks for vulnerabilities.
Benjamin Korper, the owner of Neo Security, told reporters that he hired an independent forensic firm to investigate whether Van der Stap had compromised the company or its clients. Thus far, investigators have uncovered no evidence that the suspect targeted his employer. Korper confirmed that Dutch law enforcement officers visited his office on the night of September 15 during a high-profile raid on Van der Stap’s residence that reportedly involved flash-bang grenades.
Before his initial legal troubles in 2023, Van der Stap worked as a software engineer for Amsterdam cybersecurity startup Hadrian while volunteering with the Dutch Institute for Vulnerability Disclosure, all while simultaneously engaging in corporate extortion schemes. When questioned previously about how clients and colleagues could trust his rehabilitation, Van der Stap maintained that his actions and remediation efforts were the only metrics that mattered.
Franchising and Burning a Brand
Cybersecurity researchers note that the individuals operating under the ShinyHunters banner today represent a distinct generational shift from the group’s original founders, many of whom are French nationals previously arrested for cybercrime activities. Rather than a cohesive traditional gang, modern cybercriminal syndicates frequently operate as franchises.
Investigators compare the dynamic to the fictional "Dread Pirate Roberts" concept, where the mantle is continuously assumed by new actors following the arrest or removal of their predecessors. Federal investigators have increasingly focused on a loose network of freelance affiliates who feed stolen software-as-a-service credentials to the brand in exchange for a percentage of any eventual ransom payments.

In the wake of Van der Stap’s arrest and Rey’s subsequent detention, underground Telegram channels used by the group descended into internal conflict. Commentators ridiculed Rey for folding under pressure after threatening law enforcement and subsequently allowing the ShinyHunters darknet portal to go offline following an FBI ultimatum. Community members accused the teenager of purchasing legacy PGP keys and forum credentials simply to larp as the infamous group, using the brand name to negotiate deals and skim extortion cuts.
A competing Telegram channel known as "The Battle" dedicated significant effort to doxing and criticizing Rey and his associates, characterizing the teenager as an inexperienced operator attempting to ride the coattails of a notorious brand. Administrators of the channel alleged that Rey was responsible for generating substantial financial damages while coordinating with smaller factions to negotiate corporate ransom payouts over the preceding months.
The heightened pressure from international law enforcement follows a public information campaign by the FBI, including a May flash notice warning organizations against paying ransoms to the group. The notice highlighted aggressive harassment tactics employed by ShinyHunters affiliates, ranging from threatening phone calls and text messages to victims’ families to malicious swatting incidents.
While hackers associated with the collective claimed in media interviews that their breaches of federal infrastructure were designed to counter official agency advisories and showcase technical capabilities, security experts emphasize that relentless law enforcement pressure and internal betrayal continue to fracture the infrastructure of modern extortion syndicates.
Leave a Reply