
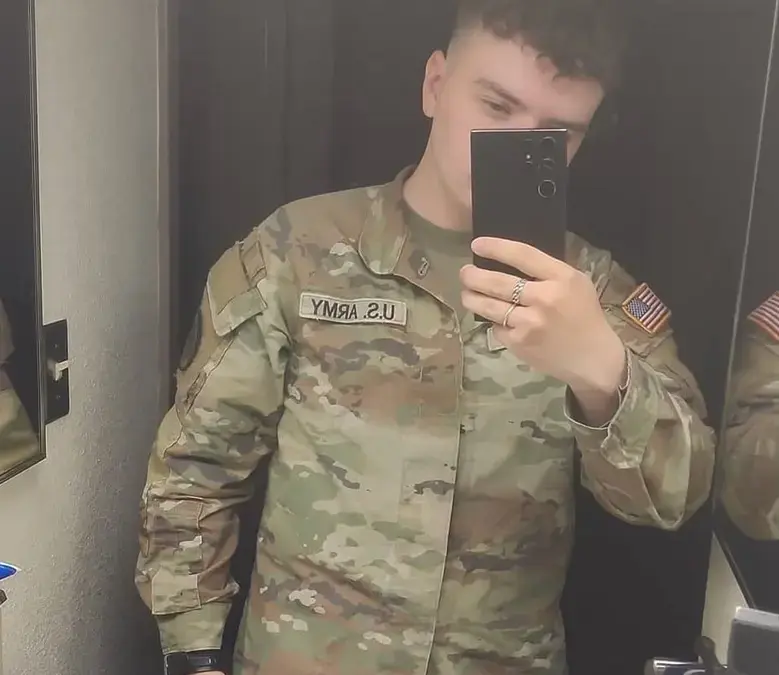
A U.S. Army soldier who pleaded guilty to hacking into multiple telecommunications companies and stealing mobile call and text metadata belonging to more than 100 million AT&T customers was sentenced in federal court today to 70 months in prison. In addition to the nearly six-year federal prison term, the former soldier was ordered to pay close to $300,000 in restitution to victims.
Cameron John Wagenius, a 22-year-old soldier who was stationed at a U.S. base in South Korea at the time of the offenses, operated under the cybercriminal persona "Kiberphant0m." Working alongside a network of alleged co-conspirators, Wagenius targeted several large customers of the cloud data storage service Snowflake. The attackers exploited exposed credentials and took advantage of accounts that failed to enforce multi-factor authentication, a security lapse that prompted Snowflake to subsequently mandate multi-factor authentication across all accounts.
The massive scale of the intrusion came to light in October 2024, when Kiberphant0m took to cybercrime forums to brag about stealing call and text metadata—including source and destination numbers, timestamps, and call durations—for tens of millions of AT&T customers. Operating under his online alias, Wagenius claimed to have breached more than a dozen telecommunications companies worldwide, including Verizon’s Push-to-Talk business, and publicly extorted these corporations with threats to publish the proprietary data unless demands were met.
Investigators began closing in late last year when cybersecurity reporting indicated that Kiberphant0m was likely an active-duty U.S. soldier stationed in South Korea. Less than a month after those initial public warnings, Wagenius was arrested and faced two separate federal indictments. He quickly chose to plead guilty to all counts across both cases.
During his sentencing hearing in Seattle, federal judges formally handed down the nearly six-year prison sentence and ordered him to pay $294,978 in restitution.
Federal prosecutors outlined that Wagenius did not operate in a vacuum, noting that he was assisted in his extortion efforts by Kenneth Schuchman, a 28-year-old resident of Vancouver, Washington, with an extensive history of cybercrime. Schuchman previously pleaded guilty in 2019 to operating the Satori botnet, a vast and dangerous collection of compromised Internet-of-Things devices that was weaponized to launch large-scale distributed denial-of-service attacks.
Wagenius also shared ties with other alleged co-conspirators who faced or are still facing charges connected to the Snowflake data thefts. Conor Riley Moucka, also known online as "Judische," a resident of Kitchener, Ontario, was arrested in 2024 and entered a guilty plea in August 2026. Another prominent figure named in the broader conspiracy is John Erin Binns, an American citizen currently residing in Turkey, who has also been wanted in connection with a massive 2021 data breach at T-Mobile that exposed the personal information of at least 76 million customers.
As the extortion plot progressed, Kiberphant0m resorted to aggressive re-extortion tactics and even threatened to release sensitive national security secrets. Immediately following the arrest of Moucka—and despite AT&T having already paid the extortion ring a $370,000 Bitcoin ransom—Kiberphant0m published what he claimed were AT&T call logs belonging to then President-elect Donald Trump and then Vice President Kamala Harris. He also shared documents and schematics that were allegedly stolen from the U.S. National Security Agency.
The unique and alarming nature of an active-duty insider threat immediately triggered a multi-agency federal response. Paul Russell, a resident agent in charge at the Defense Criminal Investigative Service, the criminal investigative arm of the U.S. Department of Defense Office of Inspector General, noted the unusual urgency of the case. When the agency received intelligence suggesting a soldier with secret clearance was trafficking in stolen data and creating hacking tools, the investigation rapidly mobilized alongside the FBI, the Army Criminal Investigative Division, and the U.S. Secret Service.
According to Russell, discovering an active-duty service member with secret clearance engaging in high-level cybercrime and extortion is an exceptionally rare occurrence. He noted that the revelation immediately galvanized all partner organizations because it represented a severe insider threat with unknown variables from the outset.
Despite the swift legal proceedings and Wagenius’s initial cooperation after pleading guilty, federal prosecutors revealed in a sentencing memo filed in Seattle that the soldier continued testing security boundaries while incarcerated and awaiting his sentencing. The government’s memo detailed that Wagenius violated the computer use policies of the Bureau of Prisons in attempts to probe the vulnerabilities of the prison system’s internal network.
According to institutional records cited by prosecutors, Wagenius used another inmate’s email system in September 2025 to instruct an email recipient to query a commercial artificial intelligence tool. The queries specifically asked for common vulnerabilities and exposures related to Windows 10 Enterprise privilege escalation and bypasses, requesting real-world working scripts without omitted code. Less than a week later, Wagenius allegedly utilized a different inmate’s account to solicit step-by-step details and code for CVE-2023-45208, a legacy command injection vulnerability affecting D-Link networking devices.
Further investigation into his prison communications revealed attempts to research how to construct improvised antennas using commissary items to extend radio reception, alongside queries regarding prison escape methods. Prosecutors noted that Wagenius often attempted to bypass commercial AI safety guardrails by framing his malicious requests as research for a book he claimed to be writing, a classic example of prompt injection used by attackers to circumvent automated restrictions against generating exploit code.
While the government acknowledged that it had no evidence Wagenius successfully deployed or utilized these vulnerabilities within the Bureau of Prisons network—with the defendant claiming his research was merely intended to help the prison identify potential security flaws—the behavior underscored a persistent disregard for cyber boundaries.
Despite the enormous perceived value and sensitivity of the data pilfered from telecommunications giants like AT&T, the financial outcome of the enterprise was remarkably poor. Court documents disclosed that Wagenius earned a total of approximately $1,500 from his attempts to sell the stolen information.
Prosecutors emphasized in their sentencing memorandum that while Wagenius proved to be largely unsuccessful as a profitable cybercriminal, his actions deliberately caused profound and widespread harm to individual consumers, major corporate entities, and the United States government.
Leave a Reply