
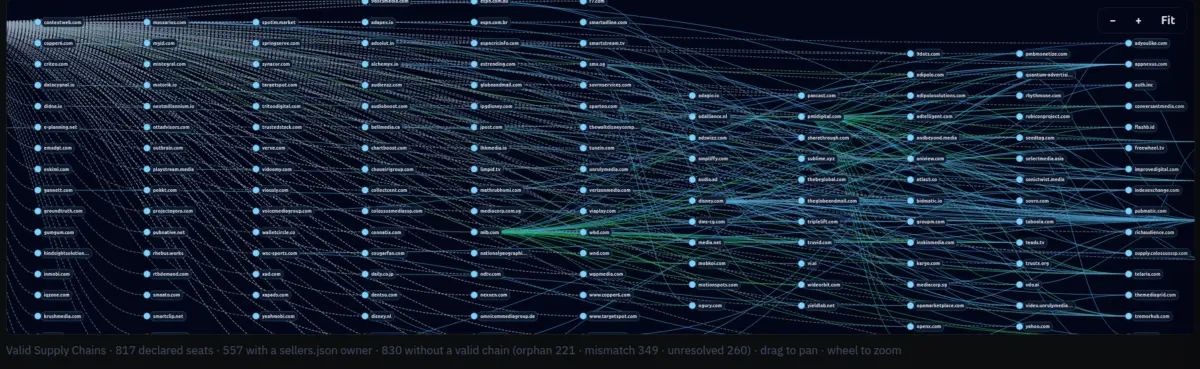
Navigating the modern internet often feels like walking through a digital maze of invisible trackers, automated data harvesters, and opaque advertising networks. Determining who is actually responsible for serving ads on a visited website or harvesting personal data from a daily mobile application has historically been an exercise in frustration. While much of this operational infrastructure is semi-publicly available, it has traditionally remained fragmented, difficult to parse, and securely locked within the proprietary ecosystems of major advertising platforms.
That landscape is shifting with the introduction of DecryptAds, a powerful and free new service designed to scrape, correlate, and simplify adtech data. Available at decryptads.com, the platform allows security researchers, privacy advocates, and everyday internet users to quickly learn a great deal about the entities tracking their digital behavior by aggregating data that websites and mobile apps are technically required to disclose.
The newly launched service operates by constantly scraping publicly accessible configuration files that publishers and app developers publish to declare their authorized monetization partners. These essential files include ads.txt, which details the adtech companies and data brokers permitted to run advertisements or harvest data from a desktop site; app-ads.txt, which performs the same disclosure function for mobile and smart TV applications; and buyers.json and sellers.json, which map out the intricate web of entities buying, selling, or reselling ad inventory for any given digital property.
Zach Edwards, chief research officer for DecryptAds and a threat researcher at the security company Infoblox, explained that he and two co-founders created the platform to address a critical blind spot in the digital ecosystem. According to Edwards, raw adtech data is generally useless unless it is cross-referenced to construct a comprehensive picture of the advertising supply chain supporting an individual website or application.
Approaching adtech from an adversarial security standpoint rather than a purely commercial one, Edwards and his team built the platform to serve underserved privacy and security use cases. These use cases include tracking down the origin points of malicious malvertising campaigns designed to distribute malware, identifying ad networks anchored in geopolitical risk zones, and detecting the rapid proliferation of low-quality, AI-generated content farms. As decryptads.com demonstrates, identifying these complex supply-chain threats is virtually impossible by inspecting a single text file in isolation.

Supply-chain integrity issues rarely live in a single file, the site notes in its analytical documentation. Instead, they manifest as broken cross-references between ads.txt, app-ads.txt, and sellers.json files; as cloned declaration sets across completely unrelated domains; as seller removals that only become apparent when viewed across multiple exchanges; and as supply paths in bid logs that never materialize within a publisher’s authorized-seller list.
To illustrate the sheer scale of modern ad exposure, a search on DecryptAds for the major sports network espn.com reveals 143 distinct advertising partners and 19 registered data broker domains listed within its authorized seller files. Information regarding these data brokers is gradually coming to light due to recent legislative shifts in states such as California, Oregon, Texas, and Vermont, which now mandate that data brokers register if they buy or sell consumer data originating within their borders. DecryptAds reports that nearly half of the data brokers linked to ESPN are engaged in collecting precise geolocation data from visitors who do not use ad-blocking software, while others disclose the collection of device fingerprints and sensitive personal information.
High-Risk Ad Partners and Geopolitical Exposure
Beyond standard ad partners, DecryptAds provides transparency regarding the ultimate beneficiaries and national origins of advertising firms operating within applications and websites. The platform displays a prominent warning when an entity is tied to geo-risk jurisdictions such as Russia and China, or to nations maintaining close financial and political alignments with both, including Cyprus and the United Arab Emirates.
For instance, the platform notes that espn.com collaborates with four advertising entities based in Russia, China, or the UAE. Among them is Between Digital, an adtech firm that lists an official corporate address in New York City. However, the DecryptAds dossier on Between Digital classifies it as a Russian enterprise, highlighting that its publisher financial offers are processed through Alfa Bank, Russia’s largest private commercial bank. Alfa Bank was among several major Russian financial institutions subjected to heavy U.S. sanctions following the 2022 invasion of Ukraine.
A broader search across several prominent U.S. military news properties—including armytimes.com, airforcetimes.com, defensenews.com, navytimes.com, marinecorpstimes.com, and federaltimes.com—reveals that all of them authorize Between Digital to serve ads and track users, alongside other entities based in the UAE and the ownership transparency haven of Panama. According to DecryptAds intelligence, Between Digital currently collects advertising data across approximately 55,000 partner websites.

Analyzing Between Digital’s app-ads.txt file exposes hundreds of domains featuring lightweight web-based games frequently interrupted by advertisements. Edwards points out that Between Digital’s own declarations indicate the firm operates simultaneously as both a publisher and a reseller on roughly two-thirds of its portfolio. This dual positioning places the company on both sides of the bidding equation, creating inherent conflicts of interest where client ad spend can be directed toward owned and operated properties or proprietary infrastructure. For years, Edwards notes, these crucial disclosure files have operated with virtually zero external oversight.
Similar complexities emerge when examining the Opera web browser, which remains popular worldwide despite being majority-owned and controlled since 2016 by the Chinese firm Kunlun Tech, while maintaining its operational headquarters in Oslo, Norway. The profile for opera.com on DecryptAds identifies 27 registered data brokers collecting user information, including 15 adtech partners in the UAE, six in China, three in Cyprus, two in Russia, and individual partners in Hong Kong and Ukraine. DecryptAds clarifies that these entities represent only seven percent of the total adtech partners explicitly declared within Opera’s authorization files.
Uncovering Legal Dossiers and Hidden Networks
One of the platform’s more advanced features is its Legal Dossier lookup tool, which compiles data on domain ownership, registration timelines, historical aliases, and underlying relationships connecting adtech firms to various web properties and mobile applications.
This capability connects directly to recent cybersecurity investigations. For example, researchers at security firm Bitsight recently uncovered a popular line of TV streaming sticks marketed under the brand H96, which quietly rented out idle consumer internet connections to unknown third parties. When not actively utilized for streaming pirated video content, these devices were discovered spoofing mobile phone signatures to automatically click on advertisements hosted across networks of low-quality, AI-generated websites. Bitsight attributed this operation to a Chinese entity known as the Fengwo Group, which simultaneously managed the malicious apps on the streaming devices and the ad-heavy content farms being targeted by the automated traffic.
A DecryptAds legal dossier on a dormant Fengwo Group domain linked to one of these AI-generated sites reveals shared seller identifiers with unrelated gaming platforms. Pivoting further on these shared identifiers uncovers hundreds of active websites operating within Russian ad systems, such as Yandex, which rely on low-quality casual games and utility tools to bombard visitors with continuous advertising streams.

Tracking Quiet Removals and Malvertising
Advertising networks frequently suspect specific partners of engaging in fraudulent clicks or distributing malicious material, yet they often quietly remove these offenders from authorized seller lists without public notification. This industry practice shields questionable adtech operators from accountability, allowing them to pivot and continue victimizing other platforms.
To counteract this visibility gap, DecryptAds features a dedicated quiet removals feed that tracks and correlates historical sellers.json removals across various ad exchanges. Because individual platforms rarely publicize their internal security bans, this feed provides researchers with a centralized view of sudden partner terminations across the broader advertising ecosystem.
Malvertising—the malicious injection of ads designed to deliver malware or drive users to phishing pages—remains a persistent threat, but Edwards emphasizes that these attacks have largely migrated away from high-traffic publishers. Major destination sites typically deploy robust security tooling and dedicated third-party protections to quickly identify and block rogue advertisements. By contrast, newly minted AI-generated content farms bypass these security investments entirely, choosing instead to integrate low-quality monetization partners. This dynamic transforms these websites into frictionless conduits for malicious ad delivery, targeting unsuspecting users who arrive via search engine results.
Addressing the root causes of malvertising and content farm exploitation will require broader data transparency from major advertising exchanges, particularly regarding supply chain objects. These structured data elements, attached to individual bid requests on the server side, allow buyers to trace every seller, reseller, and intermediary involved in passing an ad impression from publisher to buyer. Without server-side visibility into these supply paths, defending against targeted payload delivery remains exceptionally difficult. To assist researchers in automating these investigations, DecryptAds provides an application programming interface that integrates its core datasets into external analysis platforms.
Defensive Strategies for Users

In light of the complex data-sharing relationships and security risks inherent in modern digital advertising, security professionals consistently recommend deploying comprehensive ad-blocking mechanisms. Effective blocking not only curtails exposure to malvertising but also restricts the continuous data harvesting executed by adtech firms and data brokers.
For desktop and laptop users, open-source browser extensions such as uBlock Origin Lite offer robust and well-maintained filtering capabilities. Similar extensions function effectively on mobile browsers like Firefox when deployed on Android devices, while iOS users often rely on alternatives like Adblock Plus. Power users frequently leverage custom filter lists from community-maintained projects like EasyList to maximize ad removal across standard web pages. More aggressive script-blocking tools, such as NoScript, prevent all unapproved JavaScript execution but require intensive manual management to ensure websites render correctly.
For more technically inclined individuals, network-level ad blocking offers a scalable and secure alternative. By deploying lightweight hardware such as a Raspberry Pi configured with software like Pi-hole, administrators can establish a local DNS sinkhole that blocks advertisements and tracking requests across all devices connected to a home network.
At the same time, security experts caution against the growing trend of publishers pushing users toward dedicated mobile applications under the guise of an improved user experience. In practice, mobile apps frequently serve as mechanisms for extended platform engagement and the collection of highly granular device and location telemetry. Furthermore, companies increasingly utilize mobile app data harvesting to feed machine learning models. Users are encouraged to scrutinize the mobile applications they install—including those on smart TVs—and utilize tools like DecryptAds to evaluate the privacy practices and adtech partnerships underlying modern digital services.
Leave a Reply