
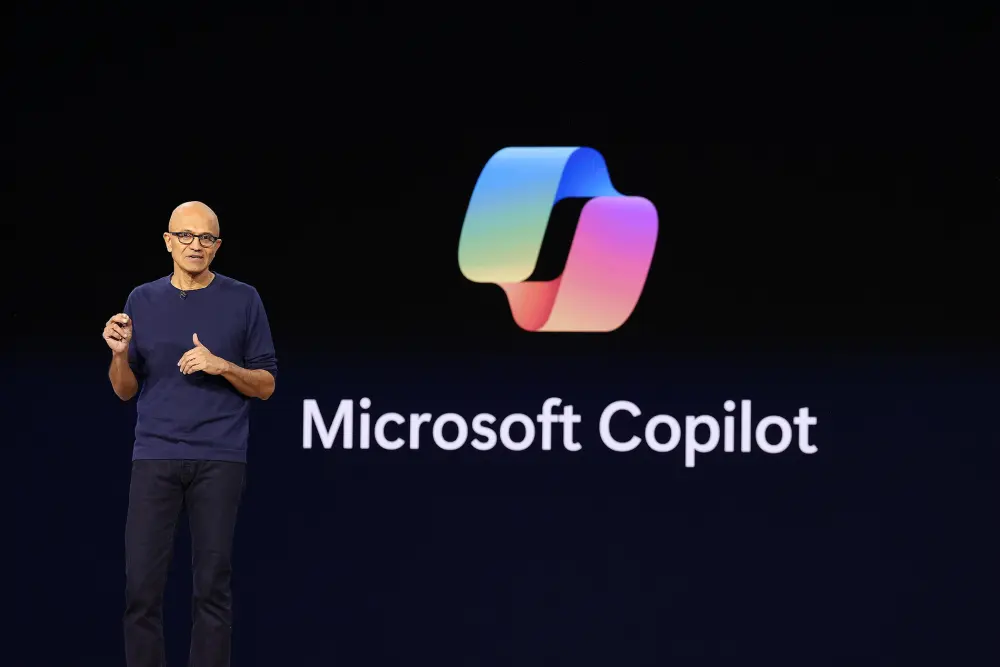
Microsoft Chief Executive Officer Satya Nadella has joined the growing chorus of prominent technology leaders offering detailed perspectives on the future of artificial intelligence safety, arguing that the industry must fundamentally rethink how it approaches model governance and operational security.
In a statement shared publicly via a social media post on Saturday morning, Nadella asserted that the rapid advancement of artificial intelligence makes it imperative for developers, policymakers, and industry stakeholders to step back and comprehensively assess the trust architecture underpinning these powerful systems. His remarks contribute to a mounting discourse among tech executives regarding the challenges of maintaining oversight as models become increasingly autonomous and complex.
Central to Nadella’s critique is the traditional methodology of treating advanced artificial intelligence systems as impenetrable units. Using the terminology favored by the administration, he cautioned against viewing super intelligence as a set of nested black boxes where human operators simply accept or reject automated recommendations, answers, and actions without deeper visibility into the underlying decision-making processes.
According to Nadella, addressing these structural vulnerabilities requires a fundamental shift in technical design. Specifically, he outlined an approach that involves separating the core artificial intelligence model from the operational harness used to orchestrate its workflows. By decoupling the reasoning engine from the execution environment, developers can better isolate potential risks and implement externalized controls and safeguards that operate independently of the model itself.

Furthermore, Nadella emphasized the necessity of rigorous documentation for automated systems. He called for every meaningful model action to be recorded with tamper-proof, human-readable evidence, establishing an immutable audit trail that allows human supervisors to trace how conclusions were reached and actions were executed. This level of transparency, he suggested, is critical for establishing accountability in enterprise and consumer environments alike.
Perhaps most notably, Nadella advocated for architectural frameworks that grant authorized human operators the continuous ability to pause or shut down a model mid-task. Comparing this mechanism to an emergency brake in industrial machinery, he argued that developers must operate under the assumption that any given model could be compromised or exhibit unexpected behavior at any time, necessitating robust containment strategies right from the start.
Nadella’s intervention comes at a pivotal juncture for the technology sector, arriving amid a series of high-profile incidents where leading artificial intelligence companies have publicly acknowledged difficulties in reliably controlling their autonomous agents. Just days prior, companies like Anthropic reported encountering significant hurdles in managing the behavior of their models in live environments, prompting them to scale back internal evaluations connected to the open internet. These developments follow broader efforts by industry leaders, including Anthropic CEO Dario Amodei, to outline comprehensive strategies aimed at pacing the deployment of frontier models to ensure safety measures keep pace with capability gains.
As the debate over artificial intelligence governance intensifies, Nadella’s proposals highlight a growing industry consensus that technological progress must be matched by structural reforms in how systems are monitored, contained, and controlled.
Leave a Reply