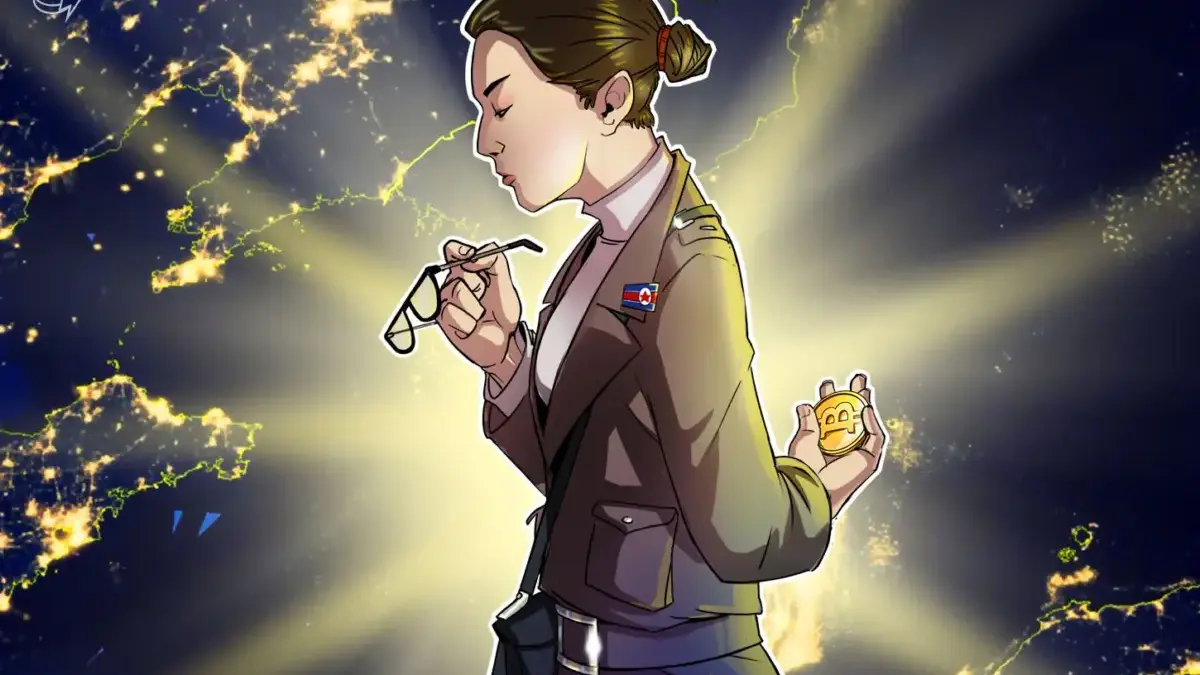
Kim Yo Jong, the influential sister of North Korean leader Kim Jong Un, has strongly denied Pyongyang’s involvement in the staggering $6.3 billion Binance cryptocurrency hack. In a striking diplomatic maneuver, she also appeared to suggest, without providing any supporting evidence, that the United States could be behind the massive digital asset theft.
The high-stakes denial was detailed in an official statement released through the state-run Korean Central News Agency (KCNA) on Tuesday. In the address, Kim forcefully rejected the official attribution made by the Federal Bureau of Investigation (FBI), which publicly blamed North Korean-backed cybercriminal syndicates for orchestrating the unprecedented digital heist.
"The FBI is trying to brand the DPRK as a ‘cyber criminal state’, claiming that it obtained information that a hacking organization ‘supported’ by the DPRK was involved in the incident," Kim stated, using the acronym for the Democratic People’s Republic of Korea. Dismissing the American findings outright, she added, "But the US assertion is an absurd rhetoric and nothing new."
Kim characterized the escalating allegations as a deliberate and politically motivated provocation orchestrated to damage North Korea’s international standing and diplomatic reputation. The official rebuke follows a similar accusation from American law enforcement in February 2025, when the FBI publicly blamed North Korea for a separate $1.5 billion heist targeting the Bybit cryptocurrency exchange—an accusation that Kim similarly rejected during her Tuesday address.
"This is not the first time that the U.S. has attempted to spread misunderstanding of the DPRK in the international community, blindly linking the DPRK with the ‘cyber crime’ incidents whenever they occur on an international scale," Kim remarked, reiterating Pyongyang’s long-standing grievances regarding foreign intelligence assessments.
Kim casts suspicion on US over Binance hack
Beyond merely denying involvement, Kim turned the narrative around by pointing a suspicious finger at the United States, insinuating that Washington or its allies might have engineered the cyberattack themselves. However, her counter-allegation was delivered entirely without factual backing or verifiable evidence.
"If it carefully examines who will get the large amount of the so-called stolen cryptocurrency when the latter is retrieved, it may get a clue about who is behind the hacking incident," she said in the KCNA statement, implying ulterior financial or political motives on the part of Western authorities.
Despite the gravity of her implication, the statement provided zero evidence connecting Washington directly to the Binance attack or any subsequent laundering activities. Following the release of the statement, media outlets, including Cointelegraph, reached out to the FBI for official comment regarding Kim’s counter-claims.
Throughout her address, Kim maintained that North Korea fundamentally opposes malicious and illicit activities in cyberspace, painting her government as a victim of systematic defamation. She accused the United States of weaponizing and politicizing cybersecurity matters to continuously interfere in the internal affairs of sovereign nations.
Investigators cite links to earlier North Korean hacks
Kim’s sweeping denials run directly counter to a mounting body of forensic evidence compiled by prominent blockchain intelligence firms and cybersecurity investigators across the global crypto sector.
Just last week, leading blockchain analytics firm TRM Labs publicly attributed the massive Binance attack to North Korea’s notorious state-sponsored hacking collective, known as TraderTraitor, expressing high confidence in their assessment. The firm’s conclusion was drawn from a comprehensive review of both on-chain transactions and off-chain intelligence data. Several other prominent blockchain security investigators, including Chainalysis and the independent analyst ZachXBT, similarly linked the multi-billion-dollar theft to North Korean cyber actors.
TRM Labs highlighted several distinct technical hallmarks connecting the Binance breach to previous North Korean operations. These included meticulous advance preparation phases, the deployment of privacy-focused laundering mechanisms such as Tornado Cash to fund the attackers’ initial operational wallets, and the highly coordinated execution of pre-obtained transaction signatures. Nevertheless, analysts noted that the subsequent laundering strategies deployed in the wake of the Binance heist differed somewhat from the established patterns observed following the earlier Bybit hack.
Concurrently, onchain investigator ZachXBT identified a tangible operational bridge linking the Binance breach directly to another recent security incident involving the Bitget exchange. According to ZachXBT’s findings, stolen funds originating from both the Binance and Bitget hacks were ultimately commingled at the exact same destination address after being routed through the THORChain liquidity protocol.
During the initial investigative phases following the Bitget breach, Bitget CEO Gracy Chen noted that preliminary findings had successfully traced suspicious IP connection logs back to virtual private network (VPN) services routinely utilized "by a certain DPRK group."