
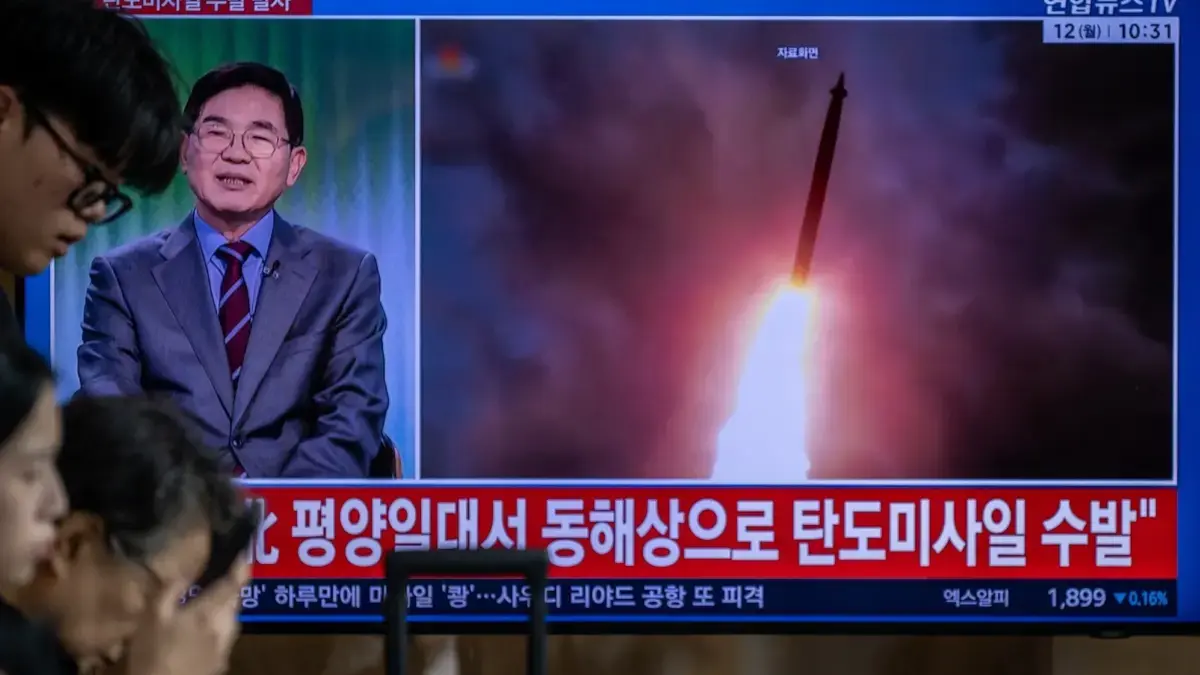
The United States Department of Justice has issued a stern warning regarding an evolving national security threat, revealing that state-sponsored hackers operating under the North Korean regime are increasingly enlisting American citizens and residents to help them infiltrate U.S. companies.
In a coordinated announcement, federal prosecutors disclosed that they have indicted and arrested at least two individuals and executed search warrants across dozens of suspected "laptop farms" located in Texas. These clandestine computer setups were allegedly utilized by North Korean operatives to remotely log into American corporate networks, bypassing geographic restrictions, masking their true locations, and stealing sensitive proprietary data and intellectual property.
According to the Department of Justice, federal law enforcement authorities have seized more than 180 computers that unsuspecting American companies had shipped directly to their newly hired remote employees. The businesses operated under the assumption that they were onboarding legitimate personnel, completely unaware that the applicants were actually sanctioned North Korean operatives. These foreign actors had successfully gained employment by using the stolen identities, Social Security numbers, and personal credentials of unsuspecting U.S. citizens.
Federal prosecutors reported that law enforcement agents raided over 40 residential laptop farms scattered across Texas. This represents the largest publicly disclosed collection of homes and residential properties utilized specifically to facilitate North Korean cyber operations. Investigators noted that these individual operations were managed and maintained by at least two primary American facilitators who acted as local logistical support for the foreign state-sponsored hackers.
The cybersecurity firm CrowdStrike, which assisted the Federal Bureau of Investigation in investigating and ultimately disrupting these latest North Korean operations, explained that these domestic laptop farms are vital to the regime’s strategy. They serve as a crucial bridge, helping North Korean hackers successfully overcome the physical, financial, and legal hurdles associated with orchestrating cyberattacks and maintaining employment from outside the United States.
Prosecutors revealed that at least 70 U.S.-based companies have been successfully infiltrated by these operatives. While the Department of Justice chose not to publicly name the affected corporations to protect ongoing investigations and corporate privacy, officials described the victims as organizations operating within critical infrastructure sectors. These include healthcare providers, cyber support firms, retail businesses, communications companies, and manufacturing enterprises spanning Ohio and 16 other states, as well as the District of Columbia. Altogether, these specific infiltrations are believed to have generated approximately $3 million in stolen funds and extorted payouts.
The Justice Department elaborated on the shifting tactics of these foreign threat actors, noting that North Korean IT workers are increasingly turning to local recruitment to counter improving private sector security detection tools and aggressive law enforcement actions. Rather than handling every phase of the operation independently, these workers are hiring local facilitators to complete a wider variety of logistical tasks. In some notable instances, they have even begun subcontracting entire corporate jobs out to third-party foreign nationals to maximize their fraudulent output and financial returns.
To maintain their deceptive cover, North Korean hackers frequently employ sophisticated social engineering techniques. They establish highly polished, realistic-looking email addresses, maintain meticulously crafted LinkedIn profiles, and build extensive digital footprints across multiple online platforms and social media networks. These digital facades are carefully curated to convince human resources departments and hiring managers that the applicants are legitimate, highly qualified professionals residing locally within the United States.
In a separate public service announcement, the FBI warned that there are currently thousands of North Korean state-controlled IT workers embedded within Western corporate structures. The bureau emphasized that these individuals pose a significant national security risk, presenting a severe intellectual property theft and insider threat to companies across various industries.
This enforcement action represents only the latest wave of arrests, indictments, and targeted disruptions directed at North Korean illicit activities within the United States over recent years. The isolated regime has systematically utilized this remote IT worker scheme as a lucrative pipeline, allowing its citizens to secure legitimate employment with American and European companies, collect steady salaries, and subsequently leverage their internal access to steal sensitive trade secrets and proprietary data. Once the intellectual property is exfiltrated, victim companies are frequently subjected to extortion schemes, forcing leadership to pay additional ransoms to prevent the public release or sale of their stolen assets.
The remote IT worker scheme constitutes just one of several sophisticated revenue streams that the North Korean regime utilizes to generate illicit capital. Other primary methods include hacking cryptocurrency exchanges and infiltrating open-source developer projects, with all generated funds ultimately channeled toward supporting the country’s internationally sanctioned nuclear weapons program. Estimates from intelligence and cybersecurity analysts indicate that the regime managed to steal at least $2 billion in cryptocurrency during the previous year alone, fueling its ongoing weapons development despite strict global economic sanctions.
Experts tracking North Korean cyber espionage operations suggest that the true scope of the problem is likely much broader than what has been officially documented, noting that the total number of compromised companies and the aggregate volume of stolen cryptocurrency are almost certainly higher than current public reports indicate.
Earlier this year, a comprehensive report published by CrowdStrike revealed that North Korean state-sponsored threat actors were responsible for roughly half of all documented "hands-on-keyboard" intrusions over the preceding year. The cybersecurity firm used the term to describe active, human-driven cyberattacks that require direct manual manipulation by skilled operators rather than relying solely on automated scripts, malware deployments, or artificial intelligence tools.
Leave a Reply