U.S. federal investigators pursuing the prolific cybercrime syndicate known as ShinyHunters have uncovered alarming ties to the upper echelons of the cybersecurity industry. According to sources close to the ongoing investigation, authorities have identified executives at two separate ransomware negotiation and incident response firms who maintained unusually close and illicit relationships with the extortion group. In one particularly startling development, a U.S.-based executive allegedly assisted the hackers in operating a public-facing website designed to pressure breach victims into coughing up ransom payments.
The revelations come as the FBI steps up its aggressive campaign against ShinyHunters, a gang responsible for dozens of high-profile data breaches and an estimated $70 million in extortion proceeds this year alone. While the group was originally spearheaded in 2019 by cybercriminals operating out of France, law enforcement attrition gradually dismantled the founding roster. Control of the brand eventually shifted to a teenage hacker based in Amman, Jordan, known online as “Rey,” who was identified by security researchers last year.
The syndicate’s brazen tactics reached a fever pitch in late September, when hackers aligned with ShinyHunters compromised the FBI’s recruitment portal, fbijobs.gov. To mock the federal law enforcement agency, the attackers threatened to dump a massive cache of sensitive personnel records online. The stolen files reportedly included Social Security numbers, home addresses, sensitive medical and psychological documentation, and detailed unit specializations for individual employees.
The compromise of the FBI jobs site prompted an immediate and lightning-fast response from federal authorities, who began detaining and questioning individuals linked to Rey and his co-conspirators. Reuters reported on October 3 that Jordanian authorities had detained Rey, who is reportedly cooperating with the FBI.
Rey’s rise to power had been facilitated just weeks prior by the sudden incapacitation of a senior confederate. On the evening of September 15, Dutch law enforcement officers conducted a dramatic raid in the Netherlands, arresting convicted hacker and ShinyHunters suspect Pepijn van der Stap. Police reportedly deployed flash-bang grenades to stun Van der Stap while he remained actively logged into various online accounts.
According to sources close to the investigation, authorities apprehended Van der Stap while he was using his Signal instant messaging application. This tactical seizure allowed investigators immediate access to recent communications, unmasking frequent contacts that included ransomware negotiators stationed in Canada and the United States.

Multiple sources with direct knowledge of the matter revealed that Van der Stap’s Signal archive served as the Rosetta Stone for unraveling a separate, chilling plot. The decrypted chats reportedly contained evidence of a murder-for-hire scheme that emerged immediately following his arrest. Dutch news outlet RTL reported last month that two planned murders were targeted abroad, with indications pointing to Van der Stap as the individual who issued the orders, though law enforcement found no evidence that the attacks were ultimately carried out.
The digital trail left by Van der Stap ultimately led directly to the doorstep of the professional cybersecurity community. On October 9, KrebsOnSecurity broke the news that the FBI had arrested Edward Dubrovsky, a 54-year-old Canadian cybersecurity executive, in connection with the broader ShinyHunters probe. Dubrovsky, who recently authored a book on cyber extortion management that advised victims to always engage with threat actors, faces federal charges of threatening to disclose hacked data and interfering with interstate commerce through extortion, according to federal court records. Politico reported that prosecutors requested Dubrovsky be held pending trial and successfully placed court records under seal.
Investigators analyzing Van der Stap’s decrypted messages discovered that the Dutch hacker maintained a steady dialogue with Dubrovsky as well as an executive at a prominent U.S.-based consulting firm. Remarkably, these executives frequently possessed granular details regarding fresh ShinyHunters victims before the victim organizations themselves had even detected the network intrusion.
Perhaps most explosively, federal investigators concluded that Dubrovsky knew well in advance that ShinyHunters had siphoned highly sensitive data from FBI servers. Despite this knowledge, Dubrovsky never alerted the bureau to the breach prior to the criminal group publicly taunting the agency on social media with threats to release deeply personal personnel files.
SHINYWIRE
As the dragnet widened, investigators uncovered an even deeper operational crossover between the corporate consultancy world and the cyber underworld. Sources close to the probe revealed that federal authorities believe at least one executive at a prestigious U.S. consulting firm played an active, hands-on role in operating “shinywire[.]com,” a now-defunct extortion portal utilized by ShinyHunters. While investigators have refrained from publicly naming the U.S. firm or the suspected executive because formal criminal charges have not yet been filed, the company is recognized as an elite enterprise employing more than 1,000 associates.
The Shinywire website operated openly from approximately May 3 until October 16, cataloging nearly 100 corporate and institutional victims of ShinyHunters breaches. Each entry on the portal functioned as a high-pressure billboard, urging victim organizations to initiate contact with the cybercriminals to discuss payment terms. The pages featured genuine samples of stolen proprietary files, accompanied by explicit warnings that the full data caches would be leaked publicly if demands were ignored.

Cached internet scans captured extortion listings targeting high-profile entities, such as Intuitive Surgical, an American medical technology giant whose network was breached in March after an employee fell victim to a targeted phishing campaign. Under the mechanics of the scheme, victim companies that refused to engage or negotiate within a strict seven-day window saw their proprietary information dumped onto the group’s primary shaming blog, which was accessible exclusively via the Tor anonymity network.
The fallout from the investigation has also exposed bitter corporate warfare within the upper tiers of the cybersecurity sector. In mid-October, The Globe and Mail reported that Dubrovsky had filed a lawsuit in Ontario earlier in the year against Daniel Tobok, the former chief executive of Cypfer, a prominent Toronto-founded incident response firm with global offices. Dubrovsky alleged that he had been made collateral damage in a campaign by his former business partner designed to destroy him professionally.
The two men originally partnered in 2017 to build Cypfer, where Dubrovsky served as managing partner and chief operating officer. However, by 2024, their relationship fractured. Dubrovsky claimed Tobok progressively marginalized him from corporate governance and executed increasingly erratic business decisions. Tobok denied the allegations, filing a counterclaim accusing Dubrovsky of misappropriating confidential information and competing unfairly through a separate venture called CyberSteward Inc., while also disputing Dubrovsky’s self-identification as a founding partner.
GHOSTBYTE
The scrutiny surrounding Tobok’s historical associations has brought older cyberattacks back into the spotlight. Interviews with former colleagues revealed that years ago, ransomware affiliates recognized Tobok by a distinct digital moniker: “Ghostbyte.”
In 2018, a Canadian enterprise fell victim to Dharma, a prolific Russian-language ransomware affiliate program active since 2016. When the victim company expressed willingness to pay a ransom to recover unrecoverable encrypted files but demanded structural guarantees that the hackers would honor the agreement, the Dharma representative pointed them toward professional help. A redacted copy of the negotiation transcript shows the ransomware operator instructing the victim to contact an IT professional in Canada who specialized in resolving such crises, directing them to the email address [email protected].
“If you want guarantees, you can write to the IT company,” the Dharma representative wrote. “Take the phone and negotiate with them. This IT company often solves such problems in Canada. You can contact them and sign a contract for services. You’ll still have to pay.”

While it remains unverified whether Tobok actively monitored or utilized the Ghostbyte inbox, breach tracking intelligence from Constella Intelligence indicates that a personal email address frequently used by Tobok—[email protected]—was tied to online accounts operating under the username “ghostbyte,” including a Snapchat profile. Furthermore, Constella established that the Dharma representative’s wallet address was linked to cryptocurrency transactions processing millions of dollars during that era.
In official statements issued in mid-October, Cypfer distanced itself from the unfolding criminal proceedings, emphasizing that its operational mandate does not involve making or facilitating ransom payments. A company spokesperson maintained that Cypfer had no prior knowledge of Dubrovsky’s arrest and noted that the firm had received no outreach from law enforcement agencies regarding any investigation.
The statement further clarified that Cypfer and CyberSteward operate as distinct corporate entities sharing no overlapping officers, directors, or employees. Cypfer was recently acquired by the Apros Group, a holding company led by Jason Hogg, a former FBI special agent and former CEO of Aon Cyber Solutions Group. Aon previously acquired Cytelligence, a security consultancy where Tobok served as founder and CEO and Dubrovsky operated as managing partner.
CONFLICTING INTERESTS
The legal landscape surrounding ransomware payments in the United States remains complex. While paying cybercriminals for decryption keys or data deletion promises is not explicitly illegal under U.S. law, organizations face severe criminal liability if they inadvertently disburse funds to groups designated as terrorist organizations or entities sanctioned by the U.S. Treasury Department. At present, ShinyHunters remains absent from official government sanctions lists.
Insurance providers typically steer compromised enterprises toward specific incident response contractors. However, because a segment of the cybersecurity forensics market refuses on principle to facilitate extortion payments, corporate clients frequently cycle through firms until they find partners willing to handle the financial transaction.
This dynamic played out prominently during the late 2024 extortion campaign against education technology giant PowerSchool, which saw sensitive data belonging to millions of students and teachers compromised. PowerSchool reportedly paid a $2.85 million ransom with the assistance of CyberSteward—an incident that later resulted in a four-year prison sentence for 20-year-old ShinyHunters affiliate Matthew Lane. Despite the payout, the protection proved illusory; by mid-2025, individual school districts began receiving secondary extortion demands utilizing identical stolen records, illustrating the impossibility of verifying whether threat actors truly delete exfiltrated files.

Industry leaders such as Coveware and Unit 221B have long cautioned victims against yielding to ShinyHunters’ demands, warning that stolen information is routinely retained, monetized elsewhere, or leveraged in secondary shaming campaigns. The FBI reinforced this stance in a May public safety advisory urging organizations not to pay the syndicate.
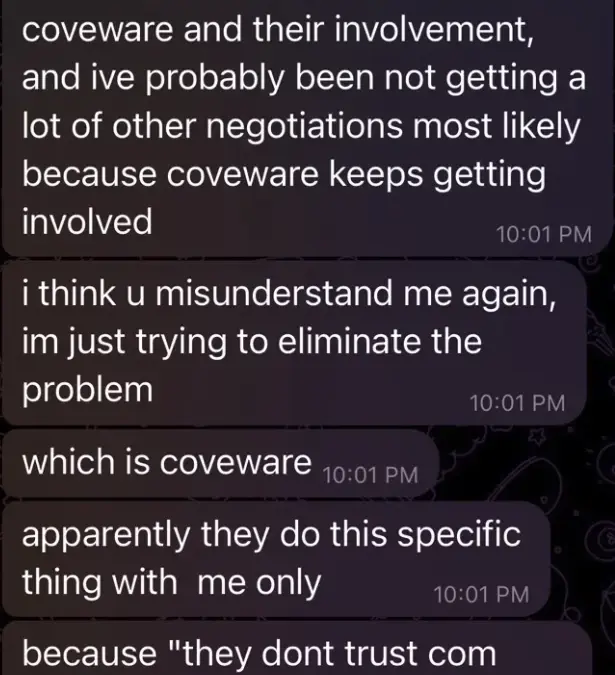
Internal communications recovered by investigators demonstrate just how severely these anti-ransom advisories disrupted the hackers’ business model. In private Telegram chats from April and May 2026, ShinyHunters operators openly complained that Coveware’s public guidance was severely depressing their payment success rates. In one message, the primary account administrator fumed that victims would have paid were it not for Coveware’s “misinformation,” vowing to eliminate the obstacle.
Mark Camillo, chief executive of CyberAcuView, an organization established by cyber insurance carriers, pointed out that the fee structures utilized by certain negotiation firms create an inherent conflict of interest. While some providers operate on flat retainers, others charge a percentage of the total ransom recovered.
“It has come to the industry’s attention that many of the ransomware payers charge a percentage of the final payment which may or may not be disclosed,” Camillo noted. “This makes no sense if they are also the negotiator. There needs to be more transparency in the process as no one in the ecosystem should be profiting purely on the size of the ransomware transaction or payment itself.”
Federal prosecutors have increasingly targeted these misaligned incentives through criminal indictments. In October, the Department of Justice charged MonsterCloud CEO Zohar Pinhasi with wire fraud and conspiracy, alleging he charged clients millions for remediation while secretly paying hackers behind his customers’ backs. Similarly, in July, Florida ransomware negotiator Angelo Martino was sentenced to nearly six years in prison for conspiring with the Blackcat/ALPHV syndicate to extract maximum payouts by leaking confidential client negotiating strategies directly to the threat actors.