The cybersecurity landscape has undergone a dramatic shift over the past month, marked by an unprecedented surge in autonomous Large Language Model (LLM) penetration testing and orchestration frameworks. Security telemetry gathered globally across the world’s largest networks reveals that defenders are increasingly struggling to keep pace with the sheer volumetric scale and autonomous precision of AI-guided attacks. What began as a single, isolated open-source project has rapidly fractured into a sprawling ecosystem of thousands of derivative tools, fundamentally challenging the status quo of modern cyber defense.
Just a few weeks ago, the open-source agentic penetration testing system known as ARTEX stood virtually alone as a tool designed to automate offensive security workflows. However, the ecosystem has experienced an explosive transformation. In a span of just three days, more than 50 distinct framework families were observed actively attempting to scan Cloudflare customers globally, with the number of unique Internet Protocol (IP) addresses operating these frameworks scaling rapidly into the thousands on a daily basis.
The trajectory of this phenomenon traces back to October 8, when ARTEX was officially taken down by its creator, known online as Autumn-27. In a statement written in Chinese at the time, the creator noted that the malicious exploitation of the tool ran entirely counter to its original intent. Paradoxically, rather than halting the spread of autonomous offensive capabilities, the removal of the original repository triggered a powerful hydra effect. In the month following the takedown, the open-source community witnessed an exponential proliferation of fragmented versions and forks.
Current metrics indicate that there are now over 12,000 repositories, including several hundred unique forks tracing their lineage directly back to the original ARTEX codebase. Furthermore, hundreds of entirely new, similar agentic orchestration frameworks have been launched since October 8. Daily requests involving AI penetration testing and exploitation tools have surged by 30 times compared to figures recorded on October 1. More concerningly, advanced threat actors have begun leveraging these tools to chain stolen customer credentials, executing complex multi-stage attacks such as lateral movement across internal environments.
What is an LLM Penetration and Exploitation Orchestrator?
Open-source penetration testing frameworks of this new generation possess the capability to orchestrate AI agents to execute traditional stages of the Cyber Kill Chain at unprecedented scale. Tools like ARTEX integrate seamlessly with the existing Model Context Protocol (MCP), connecting standalone traditional penetration testing utilities in entirely novel ways. Some frameworks even permit direct operator guidance regarding specific tactical objectives.
These autonomous tools are capable of mapping and enumerating enterprise environments from both external and internal vantage points. Utilizing graph-based architectures, ARTEX and its various forks map enterprise assets and target environments onto interconnected graphs. This allows multiple independent, parallel agents to enumerate, verify, prototype, and execute attacks at the speed of machine inference. By framing network compromises as a hill-climbable problem—an area where artificial intelligence agents excel—these orchestrators drastically shorten the time required for an adversary to escalate privileges and achieve persistence.
The technical diversity among these emerging frameworks is significant. Security analysts are currently tracking over 50 distinct AI LLM agents. Prominent examples include LuaN1aoAgent, which employs a supervisor agent, a planner agent, and generic executor agents alongside a complex three-graph system tracking goals, evidence, and targets. Another major framework, Decepticon, utilizes an orchestrator agent that dispatches specialist sub-agents within a Kali container environment, equipped with dedicated Active Directory and cloud pivoting skills. Other notable tools such as Cairn, PentestGPT-Agent, and the broader family of ARTEX derivatives demonstrate varying architectures, ranging from dispatcher models utilizing existing AI harnesses to dedicated task-list planners with built-in tunneling and reconnection capabilities.
Observations from the World’s Largest Network
Data gathered across global networks illustrates the rapid adoption curve of these technologies. As of November 12, ARTEX and its derivative forks account for more than 60 percent of all currently identified AI penetration testing orchestrators. Traffic volume has multiplied tenfold since the removal of the original repository on October 8, reflecting the decentralized distribution of the tooling.
The removal of the primary repository catalyzed a profound dispersion of codebases. Rather than eliminating the threat, public visibility and reporting around the takedown inspired widespread community modification, driving a steep acceleration in unique tool instances. Threat intelligence teams note that a single IP address frequently runs multiple distinct frameworks, complicating attribution and defensive filtering efforts.
Over the past eight weeks, incident response investigations involving ARTEX and related LLM exploitation frameworks have revealed how exposed credentials are routinely chained with automated logic to outpace traditional defenders. In multiple observed incidents, threat actors gained initial access to a hyperscaler environment and subsequently pivoted directly into customer cloud environments. Root-cause analysis consistently pointed to foundational credential hygiene failures, specifically the compromise of static, non-expiring tokens embedded within CI/CD pipelines. These tokens frequently grant broad, cross-environment permissions across an organization’s cloud infrastructure, and LLM frameworks exponentially increase the probability that an API key will be leveraged laterally to compromise secondary tenant environments.

During one specific incident response investigation, security teams observed ARTEX successfully leveraging a compromised account-level API token previously utilized for continuous integration and deployment workflows. The token lacked both IP restrictions and rate limiting, and evidence suggested the initial compromise originated through a third-party hyperscaler. Following initial access, the framework rapidly deployed numerous custom Worker scripts with distinct functional naming conventions, generating request volumes exceeding 69 requests per minute across multiple segments of the infrastructure alongside hundreds of database dump requests within a single hour. While human operators lightly guided certain aspects of the operation, the incident underscored the extreme speed and operational breadth achievable by modern AI-driven orchestration tools post-compromise.
The Modern Security Model
Large Language Models fundamentally alter the threat landscape by granting adversaries the advantages of speed and real-time validation throughout the Cyber Kill Chain. Because every phase of an attack can be computationally tested and immediately fed into subsequent stages, traditional cybersecurity architectures struggle to keep pace.
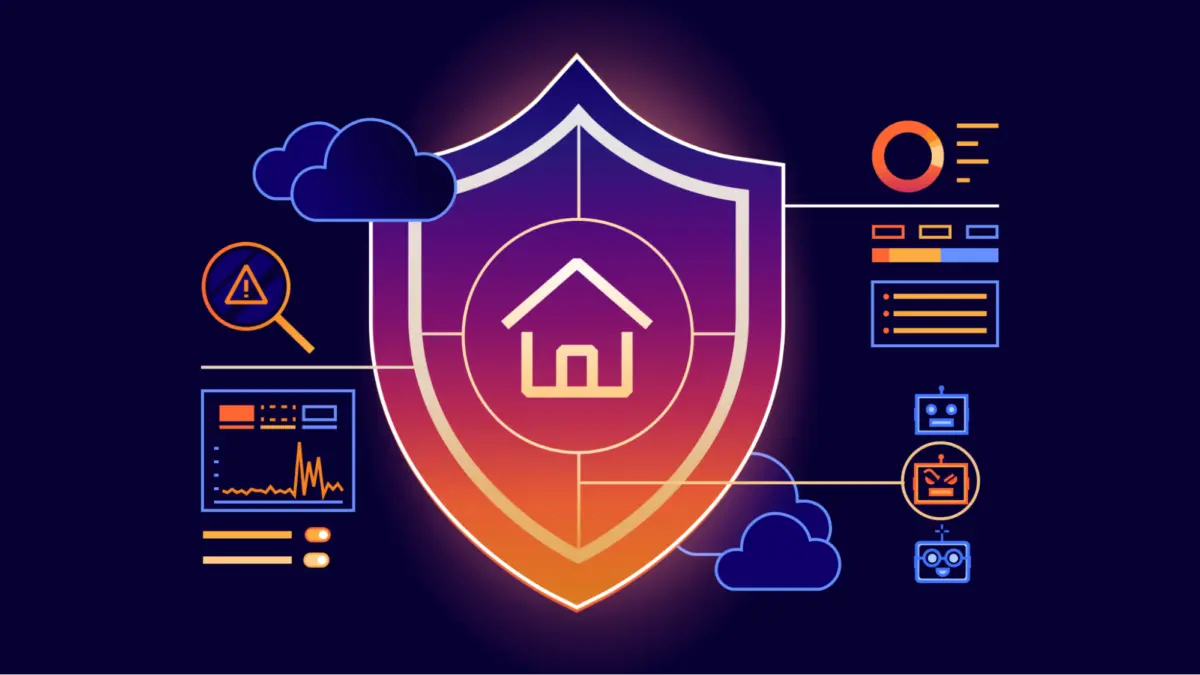
To address the vulnerabilities exposed by autonomous penetration testing frameworks, organizations are being urged to adopt a comprehensive Modern Security Model. This framework relies on a multi-layered defensive strategy designed to intercept automated threats at every level of the network architecture.
The first pillar involves fortifying the perimeter through advanced network traffic control and Web Application Firewalls (WAF). Without robust traffic management, adversaries can overwhelm entry points with volumetric floods and direct IP probing. Distributed perimeter controls help filter out unauthorized automated traffic before it reaches core infrastructure.
The second pillar centers on anomaly detection and rigorous request validation at the application entry point. Because automated agents frequently employ obfuscation techniques and non-standard syntax to probe application logic, security stations equipped with anomaly detection and strict rate-limiting rules are essential for identifying unauthorized exploration.
The third pillar incorporates sophisticated Bot Defense mechanisms. While advanced intruders and automated reconnaissance agents often attempt to mimic human traffic, behavioral analysis tools can detect the rigid cadence, mechanical patterns, and synthetic characteristics of headless browsers and AI reconnaissance scripts, quietly diverting them before they interact with sensitive endpoints.
The fourth pillar focuses on eliminating traditional back doors through identity-gated access and micro-segmentation. By restricting external visibility into internal administrative panels and diagnostic endpoints, organizations can prevent adversaries from discovering exposed entry points. Furthermore, micro-segmentation limits lateral movement, ensuring that a compromised credential cannot easily bridge the gap between development, test, and production systems.
The fifth pillar mandates rigorous schema validation and explicit security controls for all incoming API traffic and data deliveries, preventing threat actors from injecting unvalidated payloads or forged manifests intended for restricted internal systems.
Finally, the sixth pillar emphasizes threat intelligence sharing. Because isolated organizations remain vulnerable to novel infiltration techniques developed across the broader digital landscape, integrating real-time threat intelligence feeds allows security teams to receive early warnings regarding emerging command-and-control infrastructure and dynamic tunneling tactics, enabling proactive defense adjustments.
Organizations facing active security incidents or requiring assistance with threat intelligence support and the implementation of the Modern Security Model are advised to coordinate directly with specialized incident response and enterprise solutions engineering teams as autonomous threat tooling continues to evolve.