
A newly uncovered identity theft service operating on the dark web has begun selling digital scans of more than 153 million driver’s licenses belonging to individuals across the United States and Canada. According to independent investigations, including interviews with multiple individuals whose personal documents have appeared on the platform, the operation appears to be systematically siphoning high-resolution identity images collected by a prominent, widely utilized identity verification firm headquartered in Louisiana. The unfolding digital security crisis has already drawn the attention of federal authorities, with the Federal Bureau of Investigation’s New Orleans field office launching an official inquiry into the origin of the compromised records.
The operation first came to light on Monday, August 31, when a cybersecurity source alerted researchers to a newly established service advertised on a well-known Russian cybercrime forum called Exploit. The threat actor behind the platform claimed to offer access to digital scans of identity documents covering more than 170 million people throughout North America. The source flagged the listing because the proprietor of the illicit service used the researcher’s own Virginia driver’s license as a promotional free sample within the initial sales thread on the forum.
Dubbed "Nexus," the dark web service boasts an inventory containing more than 153 million driver’s licenses from the United States and Canada, alongside over 10 million identification cards, more than three million international identity and travel documents, and at least 579,000 medical cards. An initial exploration of the platform suggests that these staggering figures are entirely accurate. Running a blank search query with no parameters specified yields approximately 11.5 million pages of results, averaging roughly 15 records per page. While the database includes individuals from both sides of the northern border—such as roughly 1.1 million Canadian records, with the largest concentration originating in Ontario—the vast majority of the indexed documents belong to U.S. citizens.
Beyond standard driver’s licenses, the database incorporates a peculiar variety of credential types, including marijuana dispensary loyalty and verification cards. Some records carry internal source notations such as "CDL," presumably denoting commercial driver’s licenses, while others are marked with "CAC," a designation that typically refers to Common Access Cards, which are government-issued credentials utilized to grant physical entry to secure federal facilities and restricted rooms. High-ranking U.S. government officials have also been caught up in the exposure; previews of the database reveal records belonging to prominent figures, including U.S. Defense Secretary Pete Hegseth.

The individuals operating Nexus claim that the massive cache of license images stems from an active, ongoing data breach at a major identity verification enterprise whose customer base includes a multitude of Fortune 500 corporations. In their introductory post on the Exploit forum, the operators boasted that they had been continuously exfiltrating fresh data into a private backend database for over a year. The platform allows potential buyers to preview records prior to purchase with sensitive text fields redacted while prominently displaying subject photographs when available. Demonstrating the active nature of the pipeline, the total number of available driver’s license records surged by nearly 400,000 in a span of just 24 hours, indicating that newly harvested credential data is being fed into the marketplace on a regular schedule.
Examining individual records reveals a high level of detail. A file featuring the researcher’s own driver’s license contained six distinct image files, comprising three front-and-back pairs alongside a standard image scan accompanied by infrared and ultraviolet versions of the same documents. Every image file featured an appended date and timestamp. For the researcher, the timestamp corresponded directly to a date in June 2025 when they took a commercial flight to the American Midwest to attend a family funeral.
To trace the origin of the compromised records, researchers reached out to more than a dozen friends and family members, requesting permission to search the Nexus service for their credentials. Among those whose licenses were successfully located, every single individual confirmed having traveled on dates that closely matched the timestamps attached to their digital files. While the exact timezone of the timestamps remains slightly ambiguous, a review of car rental documentation shared by participants suggests that the system operates on Greenwich Mean Time.
Initial hypotheses centered on airport security checkpoints as the vector for the leak were quickly discarded. Notably, the database contained no passport images, and several participants whose licenses appeared in the system reported not showing their driver’s licenses at airports on their travel days. One individual whose record was indexed on Nexus had not flown at all during the relevant timeframe, though they had maintained an active car rental agreement with Hertz for several months surrounding the timestamped date. Furthermore, federal employees participating in the research noted that while they presented alternate government-issued credentials at airport security, they subsequently handed over their state-issued driver’s licenses later that same day when picking up rental vehicles from Hertz at their destinations.

Another researcher noted that during a June 2025 flight out of Reagan National Airport, they bypassed showing a driver’s license at the Transportation Security Administration checkpoint because they had not yet acquired a Real ID, relying instead on a U.S. passport. However, a search revealed their mother’s driver’s license in the same database, with timestamps separated by only a few seconds from their own. Both individuals had handed their physical licenses to a Hertz rental car counter representative simultaneously. According to accounts, the rental agent retained the physical cards behind the counter for several minutes while processing paperwork.
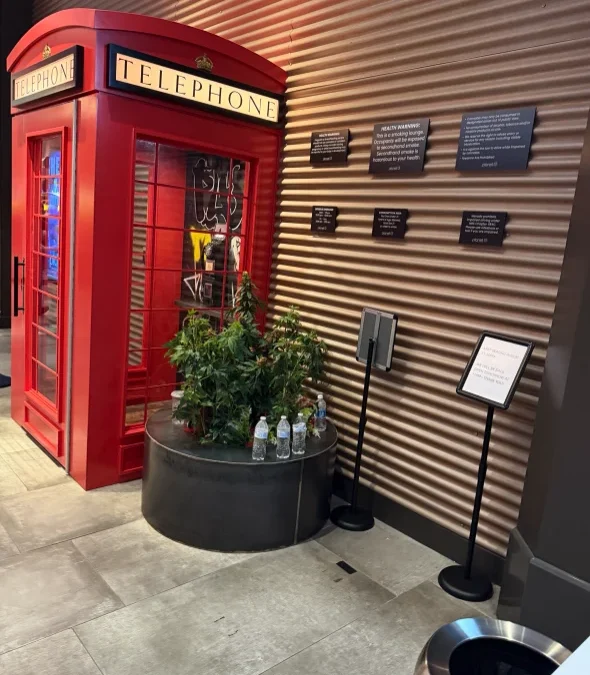
Other prominent technology and security figures have also discovered their credentials in the database. Zach Edwards, a privacy researcher who developed the tracking analysis service DecryptAds, found his driver’s license available for purchase on Nexus. The timestamp on Edwards’ record corresponded precisely to the middle of a trip to Las Vegas for the annual DEFCON security conference. While Edwards did not rent a car during the excursion, he noted that he presented his identification at an airport TSA checkpoint, his hotel, and a local cannabis dispensary. Out of those locations, only the dispensary—identified as Planet13, a multi-state retail chain—scanned his ID using an electronic verification device.
Public records indicate that Planet13 partnered with idscan.net, a New Orleans-based identity verification provider, to manage identity checks across its national storefronts. Idscan.net provides verification technology for more than 1,000 cannabis dispensaries spanning 19 states. According to the company’s corporate literature, its verification infrastructure handles more than 21 million checks monthly across over 20,000 global locations, utilizing specialized hardware capable of scanning documents with infrared and ultraviolet light. The company’s online trust documentation lists several major brands and enterprises among its client roster, including Hertz, Target, FedEx, Motorola Solutions, financial services provider Jack Henry, and Caesars Entertainment.
When contacted regarding the incident, representatives for idscan.net confirmed they were investigating the matter. Jillian Kossman, a marketing and operations leader at the company, acknowledged the communication from researchers, noting that the provided information proved helpful to the internal investigation.

Word of the privacy crisis quickly escalated within federal law enforcement circles as researchers probed the underlying infrastructure of the leak. Investigators learned that the Nexus database also indexed the driver’s license information of an assistant director within the Federal Bureau of Investigation, prompting swift institutional action. Senior leaders from the FBI’s cyber division confirmed that the agency’s New Orleans field office had formally initiated an official inquiry into the security incident implicating idscan.net.
Security experts have underscored the severe societal risks posed by the widespread exposure of state-issued identification scans. Larry Baldwin, a principal intelligence researcher at the cybersecurity firm Cybera, whose own credential scan was found on Nexus with timestamps matching a Hertz car rental, emphasized that driver’s licenses serve as foundational documents for establishing identity when opening lines of credit or executing financial transactions. Baldwin noted that the compromise places vulnerable populations at acute risk, including individuals fleeing domestic violence and persons participating in federal witness protection programs who rely on maintained identities that cannot easily be altered to bypass modern facial recognition and image-matching algorithms.
Following initial reports, idscan.net published an official notice acknowledging that an unauthorized third party may have accessed and subsequently copied customer information, including full names, driver’s licenses, and other government-issued identification numbers. The firm stated that it had begun notifying affected individuals and providing credit protection services. Meanwhile, a spokesperson for Caesars Entertainment clarified that the hospitality giant had not maintained an active client relationship with idscan.net or utilized its VeriScan software since February 2025, asserting that the company held no active accounts at the time of the breach and that the security incident should have no operational impact on its properties.
Shortly after initial reporting on the breach surfaced publicly, the Nexus dark web service infrastructure abruptly went offline. The portal replaced its login interface with a concise text message declaring that the service was no longer available.
Leave a Reply