
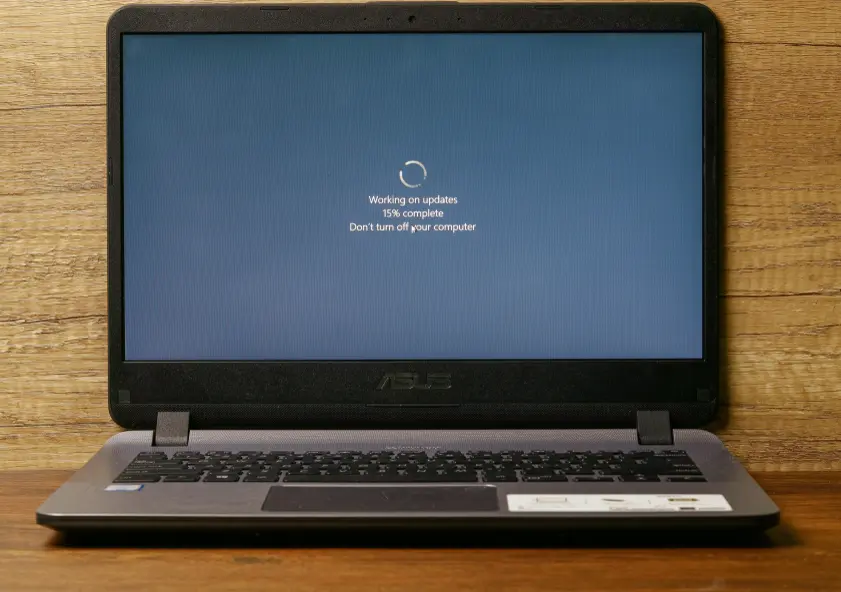
Microsoft Corp. has released its software updates for July’s Patch Tuesday, delivering fixes for at least 570 security holes across its Windows operating systems and various other software products. This massive update nearly triples the number of vulnerabilities the software giant addressed in its previous record-smashing release just a month prior. According to Microsoft, this staggering surge in patch counts is directly attributable to vulnerability discoveries that are increasingly aided and accelerated by artificial intelligence.
The scope of the July updates highlights a shifting landscape in cybersecurity. Nearly 60 of the bugs quashed in this month’s Patch Tuesday earned a critical severity rating. This classification means that malicious actors or automated malware could potentially exploit these flaws to seize remote control over a vulnerable Windows device with little to no help or interaction from the user. Furthermore, Microsoft addressed three distinct zero-day flaws in this deployment, including two critical vulnerabilities that are already being actively exploited in the real world.
Among the zero-day weaknesses are two separate issues that allow an attacker to elevate their user rights on a targeted Windows system. These join approximately 250 other elevation of privilege flaws that Microsoft patched during the same cycle. Notable inclusions in this group are CVE-2026-56155, an Active Directory Federation Services bug, and CVE-2026-56164, a security vulnerability impacting Microsoft SharePoint.
Another notable flaw addressed in the July batch is CVE-2026-50661, which represents a security feature bypass in Windows BitLocker. This vulnerability could theoretically allow unauthorized attackers to gain access to encrypted data on a device, provided they have direct physical access to the hardware. Microsoft noted that while this particular bug has been detailed publicly and is well known within the security community, the company is not currently aware of any active exploitation happening in the wild.
The underlying driver behind these unprecedented numbers is a fundamental shift in how software vulnerabilities are found and analyzed. In a blog published on July 9, Microsoft Executive Vice President Pavan Davuluri wrote that Windows users will inevitably notice a higher volume of security updates included in each recurring security release as a direct result of AI aiding in the vulnerability discovery lifecycle.
Davuluri explained that the pace of vulnerability discovery is changing rapidly with advances in artificial intelligence, making it possible to find more issues, faster, across significantly more code. He added that new mechanisms are now available that can accelerate both the discovery and the deep analysis of software codebases, fundamentally altering how development and security teams manage their software environments.
The impact of these AI-driven discoveries extends deeply into specialized components of the modern software ecosystem. Jack Bicer, director of vulnerability research at Action1, called specific attention to CVE-2026-48561, a severe remote code execution flaw discovered in Microsoft Copilot. Carrying a heavy 9.6 CVSS threat score, this vulnerability allows an unauthorized attacker to execute arbitrary code over the network. Microsoft explained that an attacker could successfully exploit this bug by hosting a malicious website that causes Microsoft Edge for Android to automatically send crafted prompts to Copilot whenever an unsuspecting user visits the site.
While artificial intelligence is advancing the state of vulnerability discovery and remediation for software vendors, it is simultaneously making it far easier for bad actors to quickly devise working exploits for known software flaws. For years, Microsoft has categorized security bugs using its proprietary exploitability index, which represents the company’s best assessment of how likely it is that attackers will figure out a reliable way to exploit a given vulnerability in real-world scenarios.
However, industry experts argue that these traditional models are no longer keeping pace with technological reality. Satnam Narang, senior staff research engineer at Tenable, argues that Microsoft’s exploitability index needs to evolve to better account for the machine-speed capabilities of modern AI discovery tools. As an illustrative example, Narang pointed out that Microsoft originally gave this month’s SharePoint zero-day an exploitability rating of less likely, even though the flaw was serious enough to be added directly to the Cybersecurity and Infrastructure Security Agency’s Known Exploited Vulnerabilities catalog on July 1.
Narang highlighted findings from Anthropic’s Red Team regarding known vulnerabilities, known commonly as n-days, which revealed how fragile the current human-centric evaluation system has become. According to Narang, Anthropic’s Mythos Preview model was able to successfully produce proof-of-concept exploits for 13 out of 14 vulnerabilities that had been officially rated by traditional metrics as exploitation less likely or exploitation unlikely. He emphasized that this means our collective way of looking at Patch Tuesday has fundamentally changed because the traditional exploitability index is centered around humans rather than AI tools, meaning defensive strategies must improve just as quickly to keep pace.
The massive scale of Microsoft’s July update is not happening in a vacuum. Chris Goettl at Ivanti observed that the record-breaking patch numbers from Redmond arrive as several other major software makers are also increasing their overall patch cadence. Adobe announced that it is moving toward a twice-monthly security bulletin schedule published on the second and fourth Tuesday of each month, explicitly citing artificial intelligence as a primary factor accelerating their internal patch cycles. Similarly, Cisco, Mozilla, and Oracle are all shipping software updates with greater frequency, while Google’s patch batches in June of 2026 totaled more than 900 individual security fixes.
Given the sheer volume of patches addressed in this month’s release cycle, IT professionals and everyday end users alike face a delicate balancing act between maintaining robust security and ensuring operational stability. Industry analysts suggest that it may be wise for regular end users to wait a few days before eagerly applying these fixes to their production machines. It is not historically uncommon for complex security patches to inadvertently introduce system stability or performance issues, and the statistical probability of encountering such complications likely increases substantially with a gigantic patch count of this magnitude. Taking standard precautions, such as backing up important Windows systems and personal data before initiating the operating system update process, remains a recommended best practice for anyone navigating this rapidly evolving digital landscape.
Leave a Reply