
Authorities in Australia have successfully arrested two men believed to be key members of TeamPCP, a prolific and destructive cybercrime and data extortion group held responsible for orchestrating what is widely regarded as the longest-running software supply chain attack spree in history.

In a joint statement released today, the Australian Federal Police (AFP) announced that two men from Western Australia, aged 21 and 23, were taken into custody following a coordinated international operation involving the AFP, the Federal Bureau of Investigation (FBI), and the Western Australia Police Force (WAPF). The suspects are accused of being part of a sophisticated cybercrime syndicate that allegedly created malicious open-source software to target and steal from thousands of global businesses.
While the AFP initially withheld the specific identities of the defendants, independent investigative reporting by KrebsOnSecurity revealed the 21-year-old suspect’s real identity months prior, leading to ongoing communications. That suspect, operating under multiple aliases, served as a primary spokesperson for the collective. The international takedown follows months of digital tracking, threat intelligence analysis, and clues left behind by the syndicate’s core leadership that ultimately facilitated their undoing.

TeamPCP forcefully entered the global cybercrime landscape in late 2025 by embedding malicious code into hundreds of widely used open-source software tools, subsequently extorting victims for financial gain. The group made international headlines by compromising corporate cloud environments utilizing a self-propagating worm known as "Shai-Hulud." This malware surreptitiously injected malicious payloads into open-source programs maintained by developers whose credentials at public code repositories, such as GitHub and NPM, had been systematically phished or stolen.
Writing for Wired, journalist Andy Greenberg detailed TeamPCP’s core cyclical exploitation strategy, describing how the hackers infiltrated networks where foundational open-source tools were actively developed. By planting malware into these utilities, the attackers infected the machines of other software developers who were simultaneously writing tools for the broader coding community. This compromised code then allowed the syndicate to harvest additional credentials, publish malicious versions of subsequent development tools, and continuously expand their collection of breached corporate networks.

In addition to direct supply chain exploitation, TeamPCP engaged in a calculated form of cyclical recruitment. In May, after publishing the source code for the third iteration of the Shai-Hulud worm online, the group launched a competitive incentive program. They offered a $1,000 prize in Monero cryptocurrency to whichever participant could execute the largest supply chain operation using the worm’s codebase. Contestants were scored based on the weekly and monthly download counts of the packages they successfully compromised, directly incentivizing them to target the most widely utilized code libraries.
Security firm Dataminr noted at the time that the contest functioned primarily as a talent identification mechanism and a method for acquiring malicious access at scale. While the initial cryptocurrency prize was dismissed by organizers as a nominal participation trophy, participants were assured that successfully harvesting high-value corporate access would result in substantially larger payouts.

The syndicate’s operational footprint was vast and economically disruptive. In March, TeamPCP executed a high-profile supply chain attack targeting artificial intelligence infrastructure by compromising the code for LiteLLM, an open-source AI gateway connecting users to more than 100 different large language models. A subsequent analysis by security firm CloudSEK revealed that this specific breach harvested cloud service keys and sensitive credentials from more than 2,500 organizations, including many of the world’s leading technology enterprises. By May, TeamPCP further claimed credit for compromising at least 3,800 code repositories on Microsoft-owned GitHub after an individual developer installed a compromised code extension.
Security experts emphasize that TeamPCP operated less as a traditional, hierarchically structured hacking crew and more as an amalgamation of threat actors drawn from multiple cybercriminal gangs who occasionally collaborated toward shared objectives. Austin Larsen, a principal threat analyst with the Google Threat Intelligence Group, described the entity as a peer community of individually skilled operators rather than a structured criminal enterprise with a single director, though it maintained a clear center of gravity.

That operational center of gravity has been tied to George Prepakis, an accomplished security researcher and self-described exploit developer who operates the X profile @kernelstub. Earlier this year, Prepakis distributed a public invite link to a Matrix chat server he established, which members dubbed "Cybercats." TeamPCP and various associated cybercrime entities utilized this private server for daily coordination over a span of several months.
Administrators within the Cybercats chat frequently operated under their public social media handles, occasionally taunting victims online before attacks were publicly reported by the media. Prominent figures within this ecosystem included individuals using handles such as "Boxturtle," linked to a data breach broker active on underground forums who sold data stolen from major automobile manufacturers—including BMW Group, Audi, Honda, Mercedes-Benz, Volvo, and Toyota—as well as Snapchat and SportRadar. Another key figure, "SeesawSec," was identified as an alias behind the Fulcrumsec extortion group, which claimed credit for attacks against pharmaceutical giant Novo Nordisk, data broker LexisNexis, and Fortune 500 electronic component distributor Avnet.

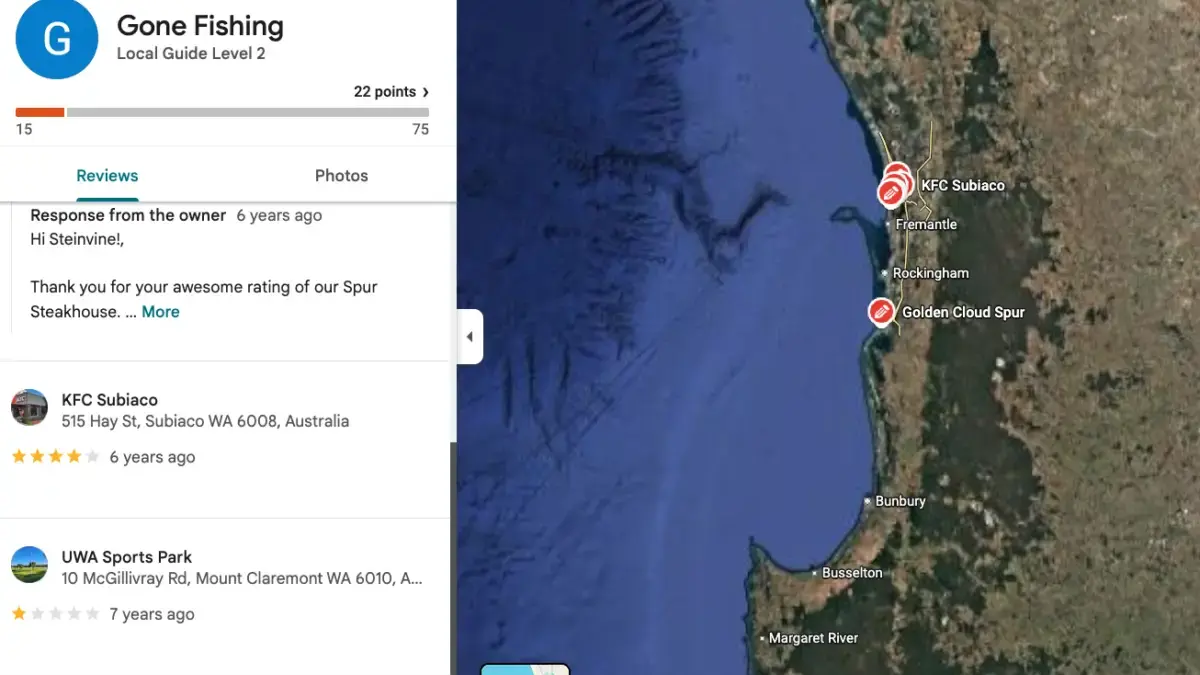
Among the chat administrators was an account using the handle "@pcpcasper," whose extensive message history on Telegram linked them directly to the National Socialist Network, an Australian neo-Nazi organization. Shared media within these chats placed the user in Western Australia, with sources close to the investigation confirming that this individual was one of the two men arrested by federal authorities.
The group’s primary spokesperson and a central leader within TeamPCP operated under various handles, including "T" and "@pcpcats," before being apprehended. Investigators mapped a complex web of alternative personas utilized by the leader across various underground forums, including EllisD25/LSD on Darkforums, BulkDMT on Breachstars, and Express on Breachforums. These aliases were tied together through shared instant messaging identifiers such as Tox IDs and Session IDs, as well as digital infrastructure like a virtual private server hosting service known as DMT Host.

Threat intelligence platforms, including Intel 471 and Flashpoint, tracked the leader’s activities across multiple jurisdictions. Forum posts and chat messages indicated periods of residency in South Africa, aligning with Google’s technical findings that traced residential and mobile internet connections used during several TeamPCP attacks to the region. Publicly shared grievances regarding local land policies and personal struggles with methamphetamine addiction provided additional behavioral markers that investigators utilized to map the threat actor’s digital footprint.
Critical breakthroughs in the investigation emerged through foundational operational security failures. Identity threat protection firm SpyCloud discovered that an email address associated with the suspect’s early forum accounts had been used to register an account on Raidforums as early as 2022, with nearly all associated IP addresses originating from Internet Service Providers in Perth, Australia. Passive DNS records maintained by DomainTools traced these IP addresses to residential file servers managed by a family with the surname Thomson in the Perth suburb of Cottesloe.

Open-source intelligence and public records revealed that the family, originally from South Africa, included a young man named Ruben Thomson. Further digital profiling linked Ruben Thomson to multiple business entities registered in Australia, including Secure Computing Solutions, Tensor Industries, and OPSEC Express—the latter bearing an ironic moniker referencing the concept of operational security. Additional exposure occurred when an account registered under the name Ruben Thomson on the HackerOne bug bounty platform utilized the username Deadcatx3, an alias previously flagged by multiple security firms as belonging to TeamPCP.
In interviews conducted prior to his arrest, the TeamPCP leader—known online as Ellis—was remarkably candid about his motivations, substance abuse struggles, and involvement in the syndicate. Admitting that he began working with TeamPCP after completing a sobriety program and seeking a distraction, he described blackhat hacking as an environment that offered genuine intellectual rewards and peer community for individuals lacking formal professional pathways. He estimated earning roughly $20,000 through his activities with the group, asserting that his primary drivers were technical engagement and camaraderie rather than financial accumulation.

Security researchers point out that TeamPCP represents an emerging class of threat actors who defy traditional categorization. Charlie Eriksen, a security researcher at Aikido Security, noted that the group’s motivations blended financial gain, disruption, attention, and ideology. Eriksen emphasized that the accessibility of modern artificial intelligence and large language models has significantly compressed the knowledge gap required to execute complex cyberattacks, enabling actors to operate at scale without necessarily possessing the operational discipline or foresight traditionally associated with sophisticated cybercrime syndicates.
Despite the disruptive nature of their campaigns, Eriksen credits TeamPCP’s Shai-Hulud worm with accelerating crucial security reforms across the software development industry. By successfully compromising high-profile repositories and demonstrating systemic vulnerabilities, the group’s actions compelled platforms like GitHub to implement stronger safeguards, including mandatory cooldown periods for package dependency updates designed to thwart malicious code propagation.

Following their arrests in Perth, the two suspects—identified by Australian media as Ruben Ian Thomson and Michael Gaebler—were scheduled to appear before the Perth Magistrates Court. Authorities confirmed that Thomson was denied bail, while legal counsel for Gaebler did not request bail, ensuring both defendants remain in custody pending their next scheduled court appearance.
Leave a Reply