
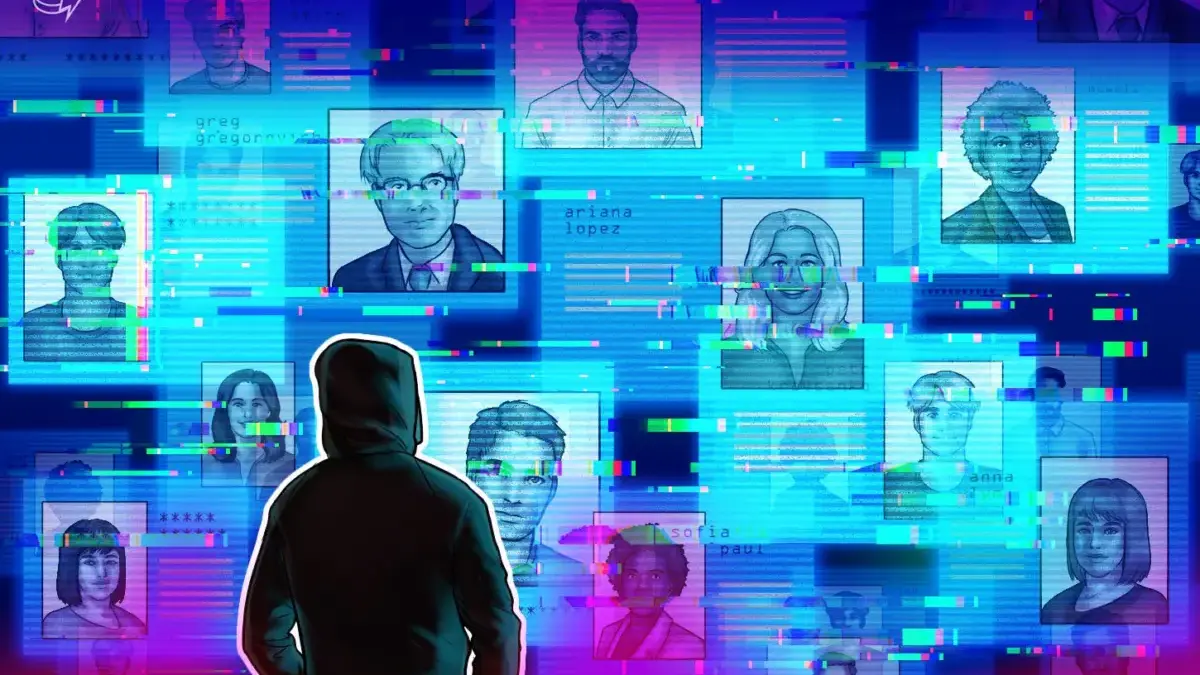
Threat actors who successfully compromised and obtained sensitive Revolut customer information appear to have escalated their campaign, beginning to post the stolen data online while threatening to release more information every single day until the financial technology company meets their financial demands. The situation has intensified following claims from the attackers that they will continue leaking sensitive files on public channels unless a ransom is paid.
The newly leaked information reportedly includes high-risk personal data, specifically selfies and copies of official identity documents belonging to high-profile individuals. Among those whose documents have surfaced online are professional tennis player Alexander Shevchenko and Felix Römer, the Chief Executive Officer of the online crypto casino Gamdom. This development came to light following a post shared on the social media platform X by the International Cyber Digest.
According to statements attributed to the hackers on the encrypted messaging platform Telegram, the extortion campaign is set to expand rapidly in the coming days. The attackers reportedly stated that they are going to start releasing more and more data every day until Revolut pays for leaking their customers. Major industry publications, including Cointelegraph, have reached out to both Revolut and Felix Römer for official comments regarding the ongoing data dump and the specific individuals affected.
The public exposure of official identity documents, facial-verification images, and KYC (Know Your Customer) photographs significantly increases the potential risk of targeted identity theft, financial fraud, and social engineering attacks against the impacted individuals. This unfolding crisis follows previous disclosures made by Revolut. On Friday, the digital banking platform informed affected customers that the leaked database encompasses a wide array of personal and financial information.
According to Revolut’s communications with its user base, the exposed data fields include customers’ full legal names, dates of birth, listed occupations, private contact information, detailed account statements, and exhaustive transaction histories. Crucially, these historical financial records reportedly feature comprehensive logs of Bitcoin transactions and other digital asset movements, raising serious privacy concerns for cryptocurrency holders who utilize the platform for their day-to-day financial activities or digital currency management.
The security incident itself stems from a specialized breach method rather than a traditional technical exploit of Revolut’s core digital infrastructure. Revolut previously disclosed that the customer data was compromised due to what the company described as a sophisticated external impersonation scam. In this targeted attack, the malicious actor successfully utilized an email address originating from a legitimate government agency domain. By leveraging this trusted communication channel, the attacker was able to submit fraudulent requests for customer information, successfully deceiving personnel or bypassing standard administrative checks to siphon off the sensitive data files.
Despite the severity of the data leak and the ongoing public extortion attempt, Revolut has maintained that the breach remains relatively contained in terms of overall user base impact. The company later informed reporters that the security incident affected only a limited number of customers rather than the platform’s broader global user base of millions of account holders. Furthermore, Revolut has repeatedly emphasized that its core operational systems, internal servers, and customer funds remain entirely safe, secure, and unaffected by the external impersonation scam or the subsequent data extortion efforts.
As the situation continues to develop on messaging apps and social media platforms where the threat actors publish their ongoing leaks, affected individuals and security researchers are closely monitoring the situation to gauge the full extent of the compromised records. Meanwhile, media outlets and industry watchdogs continue to track the digital footprint of the stolen files as the ultimatum issued by the threat actors progresses. Revolut has continued to handle inquiries regarding the incident while reiterating its position on the scope of the breach and the nature of the external deception that initially allowed the unauthorized data access to occur.
Leave a Reply