
A 26-year-old Canadian man, once characterized by investigators as one of the most consequential cybercrime threat actors of 2024, has formally pleaded guilty to computer fraud and conspiracy charges. The charges stem from an expansive campaign to hack and extort more than 165 prominent organizations that utilized the cloud storage provider Snowflake. The defendant, Connor Riley Moucka of Kitchener, Ontario, also admitted to his role in stealing sensitive call and text history records belonging to more than 100 million AT&T customers during the height of the cyberattacks.
According to documents released by the U.S. Justice Department, the illegal operation unfolded between February and October 2024. During this period, Moucka and a network of co-conspirators leveraged stolen login credentials to infiltrate cloud-hosted databases belonging to at least 165 corporate customers of the U.S.-based software-as-a-service company. The threat actors specifically sought out Snowflake customer accounts that failed to enforce multi-factor authentication, exploiting these security oversights to access vast repositories of corporate data.
Armed with unauthorized access, the hackers launched a wave of extortion attempts targeting a host of well-known corporate entities, including TicketMaster, Lending Tree, Advance Auto Parts, and Neiman Marcus. The fallout from the campaign prompted Snowflake to overhaul its security posture significantly, responding to the data thefts by implementing stricter password complexity requirements and mandating multi-factor authentication for user accounts.
Throughout his cybercriminal operations, Moucka routinely cycled through a rotation of aliases, frequently maintaining multiple digital identities concurrently to obscure his tracks. However, two of his most prominent monikers became widely known within the cybersecurity community: "Judische" and "Waifu." The connection between the alias "Judische" and the widespread Snowflake data thefts was first exposed by security researcher Brian Krebs in September 2024. That investigative reporting detailed the troubling overlap between English-speaking cybercriminal syndicates and extremist groups that harass and extort minors into committing acts of self-harm or violence against others.
The September 2024 report identified Judische as an Ontario-based software engineer who had spent years participating in high-profile data breaches and voice phishing campaigns targeting American enterprises since at least 2020. Just over a month after those findings were published, Canadian law enforcement officials apprehended Moucka on a provisional arrest warrant issued by the United States, initiating the international legal proceedings that ultimately led to his guilty plea.
Federal prosecutors outlined the staggering scale of the data stolen during the conspiracy, noting that Moucka and his associates downloaded terabytes of proprietary information and billions of sensitive records. The compromised data included non-content call and text history records for individuals, banking and financial information, corporate payroll records, Drug Enforcement Administration (DEA) registration numbers, driver’s license numbers, passport numbers, Social Security numbers, and other forms of personally identifiable information. Armed with this sensitive material, the conspirators attempted to coerce victims into paying ransoms by threatening to publish the stolen records on public forums.
Beyond corporate extortion, the investigation revealed that Moucka actively threatened and harassed government officials and security researchers who were working collaboratively to track down the perpetrators. The U.S. Justice Department reported that the criminal enterprise successfully extorted more than $2.5 million in ransom payments from their targets. In at least one particularly brazen instance, Moucka targeted a victim with a secondary wave of extortion, threatening further disclosure of sensitive materials.
Court documents detail that Moucka utilized the stolen personal data of a government officer and members of that former government officer’s immediate family during this re-extortion attempt, highlighting the aggressive and malicious nature of the campaign.
Federal investigators have steadily unraveled the broader network supporting these intrusions, identifying several key co-conspirators. Among them is Cameron "Kiberphant0m" Wagenius, a U.S. Army soldier who entered a guilty plea in July 2025 to charges stemming from the extortion of AT&T and Verizon for customer account data. Weeks prior to Wagenius’s arrest, security researchers published an in-depth analysis tracking his various Telegram and Discord profiles, which exposed statements from the account holder boasting about active military service and deployment in South Korea.
Wagenius also engaged in secondary extortion tactics against victims. Immediately following Moucka’s capture, Wagenius published files on illicit hacker forums that he claimed were the AT&T call logs belonging to then-President-elect Donald Trump and then-Vice President Kamala Harris, alongside engineering schematics allegedly stolen from the U.S. National Security Agency (NSA).
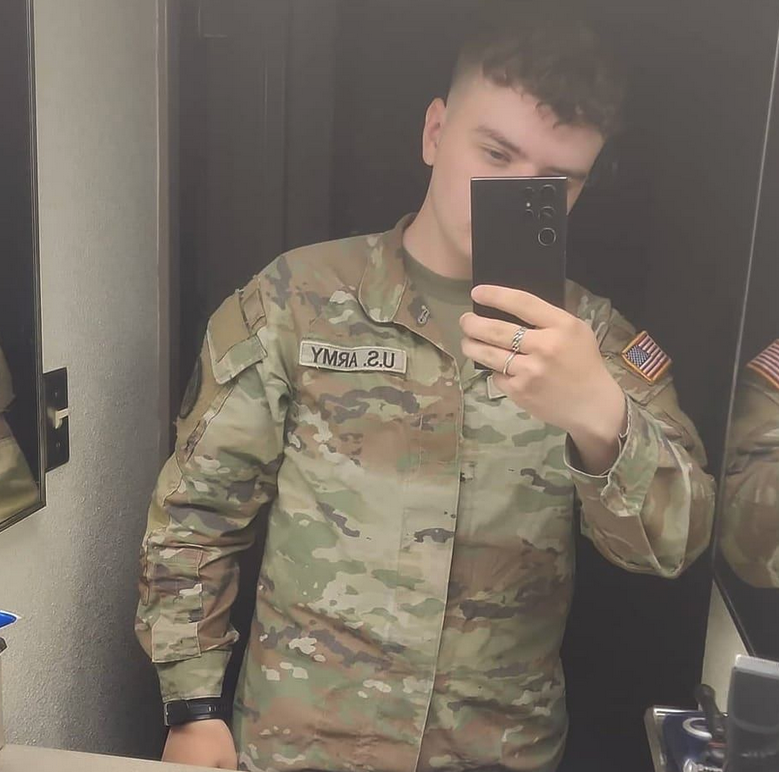
Wagenius is scheduled to be sentenced on September 3, 2026. Prosecutors noted that he faces a maximum prison sentence of 20 years for conspiracy to commit wire fraud, an additional maximum penalty of five years for extortion linked to computer fraud, and a mandatory two-year consecutive prison term for aggravated identity theft.
A third key figure linked to the broader investigative orbit is John Erin Binns, a 26-year-old American citizen who fled the United States after being indicted for his role in a massive 2021 breach at T-Mobile that exposed the personal data of at least 76 million customers. Sources close to the ongoing investigation indicated that Binns, who operated under aliases including "IRDev" and "IntelSecrets," had spent time incarcerated in a Turkish prison before being released and reappearing online. According to these sources, Binns recently acquired Turkish citizenship. Under domestic Turkish law, citizens cannot be extradited to foreign jurisdictions, complicating potential efforts to bring him before U.S. courts.
In his own legal proceedings, Moucka pleaded guilty to four distinct criminal counts: computer fraud, wire fraud, aggravated identity theft, and conspiracy. He is scheduled to appear for sentencing on October 27. Under the terms of the federal charges, Moucka faces a mandatory minimum sentence of two years in prison specifically for the aggravated identity theft count, paired with a maximum potential penalty of up to 30 years in prison across the remaining counts. The final determination of his prison term rests with the federal judge presiding over the case, who will weigh the extensive scope of his cybercriminal conduct.
Leave a Reply