
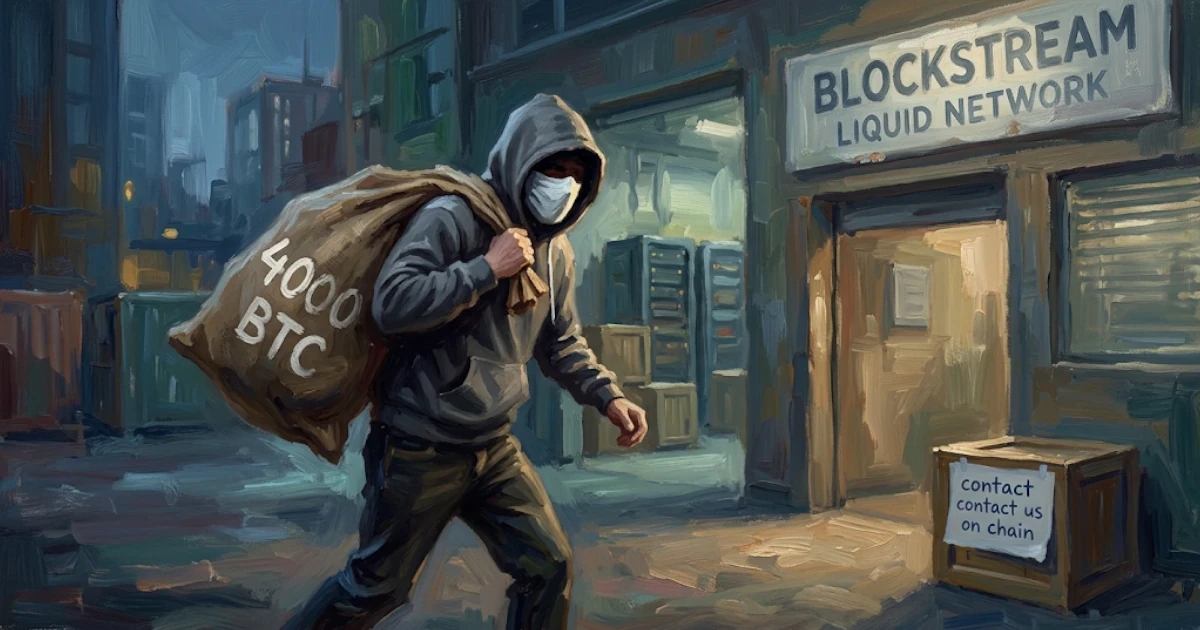
The Liquid Network, a prominent federated sidechain of Bitcoin founded by Adam Back’s Blockstream, was forced to halt its bridge nodes and pause network operations on Sunday following a massive security breach. According to official statements from the network, purported white-hat hackers managed to withdraw approximately 4,000 bitcoin, valued at roughly $320 million, from the core federation wallet that backs L-BTC.
The incident has sent shockwaves through the broader cryptocurrency ecosystem, raising urgent questions about sidechain security, consensus mechanics, and the vulnerabilities inherent in multi-signature federation models. Despite the scale of the breach, officials confirmed that other issued assets operating on the Liquid Network—including USDT, DePix, and various real-world assets (RWAs)—remained entirely unaffected by the exploit. However, the sudden drain of the underlying capital backing L-BTC has left users and stakeholders grappling with immediate liquidity and redemption concerns.
Understanding the Liquid Network Architecture and the Federation Treasury
To fully comprehend the mechanics of Sunday’s breach, it is necessary to examine how the Liquid Network operates. Founded as a federated sidechain of Bitcoin, the network is designed to enable faster, more confidential transactions for traders, exchanges, and financial institutions. The system issues a variety of assets, most notably L-BTC, which is pegged 1:1 with native Bitcoin held on the Bitcoin main chain.
This capital backing L-BTC is stored in a massive, highly secure multi-signature treasury managed by 15 corporate and known members of the Liquid Federation. Security protocols dictate that a valid multi-signature transaction requires the cryptographic sign-off of at least 11 of the 15 members to successfully move coins out of the treasury.
Prior to the hack, the federation treasury held a robust reserve of over 4,200 BTC. Following the unauthorized withdrawal, Blockstream’s public proof-of-reserves page reported a dramatic decline, leaving a little over 207 BTC remaining in the treasury address. This staggering depletion highlights the immense concentration of risk inherent in federated bridge models, where a quorum of trusted institutional validators acts as the custodian for millions of dollars in user funds.
The Exploit: Peg-Out Transactions and an Alleged Inflation Bug
According to on-chain data and transaction records, the hackers successfully withdrew 4,019.4 BTC from the primary reserve address in a single peg-out transaction. This transaction was executed using the SideSwap Peg-out Authorization Key. SideSwap functions as a bridge exchange and is an officially recognized member of the Liquid Federation.
While comprehensive technical details regarding the exact exploitation mechanism are still being investigated and confirmed, early analysis suggests that an inflation bug on the L-BTC sidechain was manipulated by the attackers. By exploiting this consensus vulnerability, the perpetrators were able to artificially mint over 4,000 units of L-BTC that did not previously exist within the system. They then utilized these newly created tokens to cash out for authentic, on-chain bitcoin directly from the federation’s reserves.
Because the transaction was structured in a way that appeared entirely valid under the rules governed by the compromised consensus state, the federation members’ hardware security module (HSM) servers processed and signed the massive BTC withdrawal transaction, which was valued at approximately $320 million at the time of execution. The technical sophistication required to leverage an inflation bug of this nature underscores the persistent threats facing complex sidechain architectures that attempt to mirror or bridge main-chain consensus rules.
Communications From the Hacker Address and On-Chain Messaging
Following the massive withdrawal, the funds were swiftly moved to a distinct receiving address ending in "6gyqjlte." Shortly after the transfer, the entity controlling the address utilized the OP_RETURN arbitrary data field to broadcast a transactional message to the network, declaring, "we are whitehats. contact us on chain." At the time of writing, the stolen coins remain stationary at that specific address.
In an effort to establish a secure line of communication with the actors behind the breach, a small mainnet transaction was sent to the hacker’s address, accompanied by an OP_RETURN message stating, "Please contact support@…". While presumed to originate from a Blockstream public address, this attribution remains formally unconfirmed. A subsequent OP_RETURN spend originating from the hacker address countered with a message instructing observers to "Please contact us on Signal @m671aw.70." Industry analysts note, however, that this secondary message may potentially be spam, as it did not directly share a verifiable link or cryptographic association with the address holding the stolen funds.
Immediate Industry Response and Impact on Users
In immediate response to the security breach, industry exchanges and custodial platforms were instructed to temporarily suspend all L-BTC deposits and withdrawals to prevent further financial exposure. Bridge nodes across the Liquid Network were systematically disabled, effectively limiting external access to the sidechain, though the underlying chain continues to produce blocks independently.
Public commentary from industry leaders quickly followed the disclosure. JAN3 CEO Samson Mow addressed the situation publicly, noting that Aqua’s Liquid features had been impacted while confirming that standard on-chain bitcoin operations continued to function normally. Other wallets and financial applications throughout the digital asset industry that rely on the Liquid Network are also expected to experience disruptions.
For everyday users holding L-BTC, the breach introduces severe uncertainty. Because the underlying bitcoin backing the tokens is currently not redeemable due to the depleted treasury reserves, savings held in L-BTC are effectively at risk. Due to the inherent privacy features of the Liquid chain, public on-chain analytics remain scarce, making it difficult to accurately determine the exact distribution of L-BTC holdings between retail users, corporate entities, and Blockstream itself. Should the stolen funds ultimately fail to be recovered, the incident would deliver a heavy reputational and financial blow to the Liquid Network’s user base.
As the situation unfolds, holders of L-BTC have few immediate alternatives other than to monitor developments closely and await the outcome of communications between the core developers, federation members, and the hackers. Given the unprecedented scale of the hack and the high visibility of the addresses involved, experts suggest it would be exceptionally difficult for the perpetrators to permanently liquidate or launder such a massive volume of bitcoin without detection. Market observers speculate that a resolution may involve negotiations centered around a substantial bounty or finder’s fee in exchange for the return of the majority of the stolen funds.
Leave a Reply